 Have a question? +971 56 404 0503

Tech Features
MAXION on the Rise of Behavioural AI in Consumer Apps

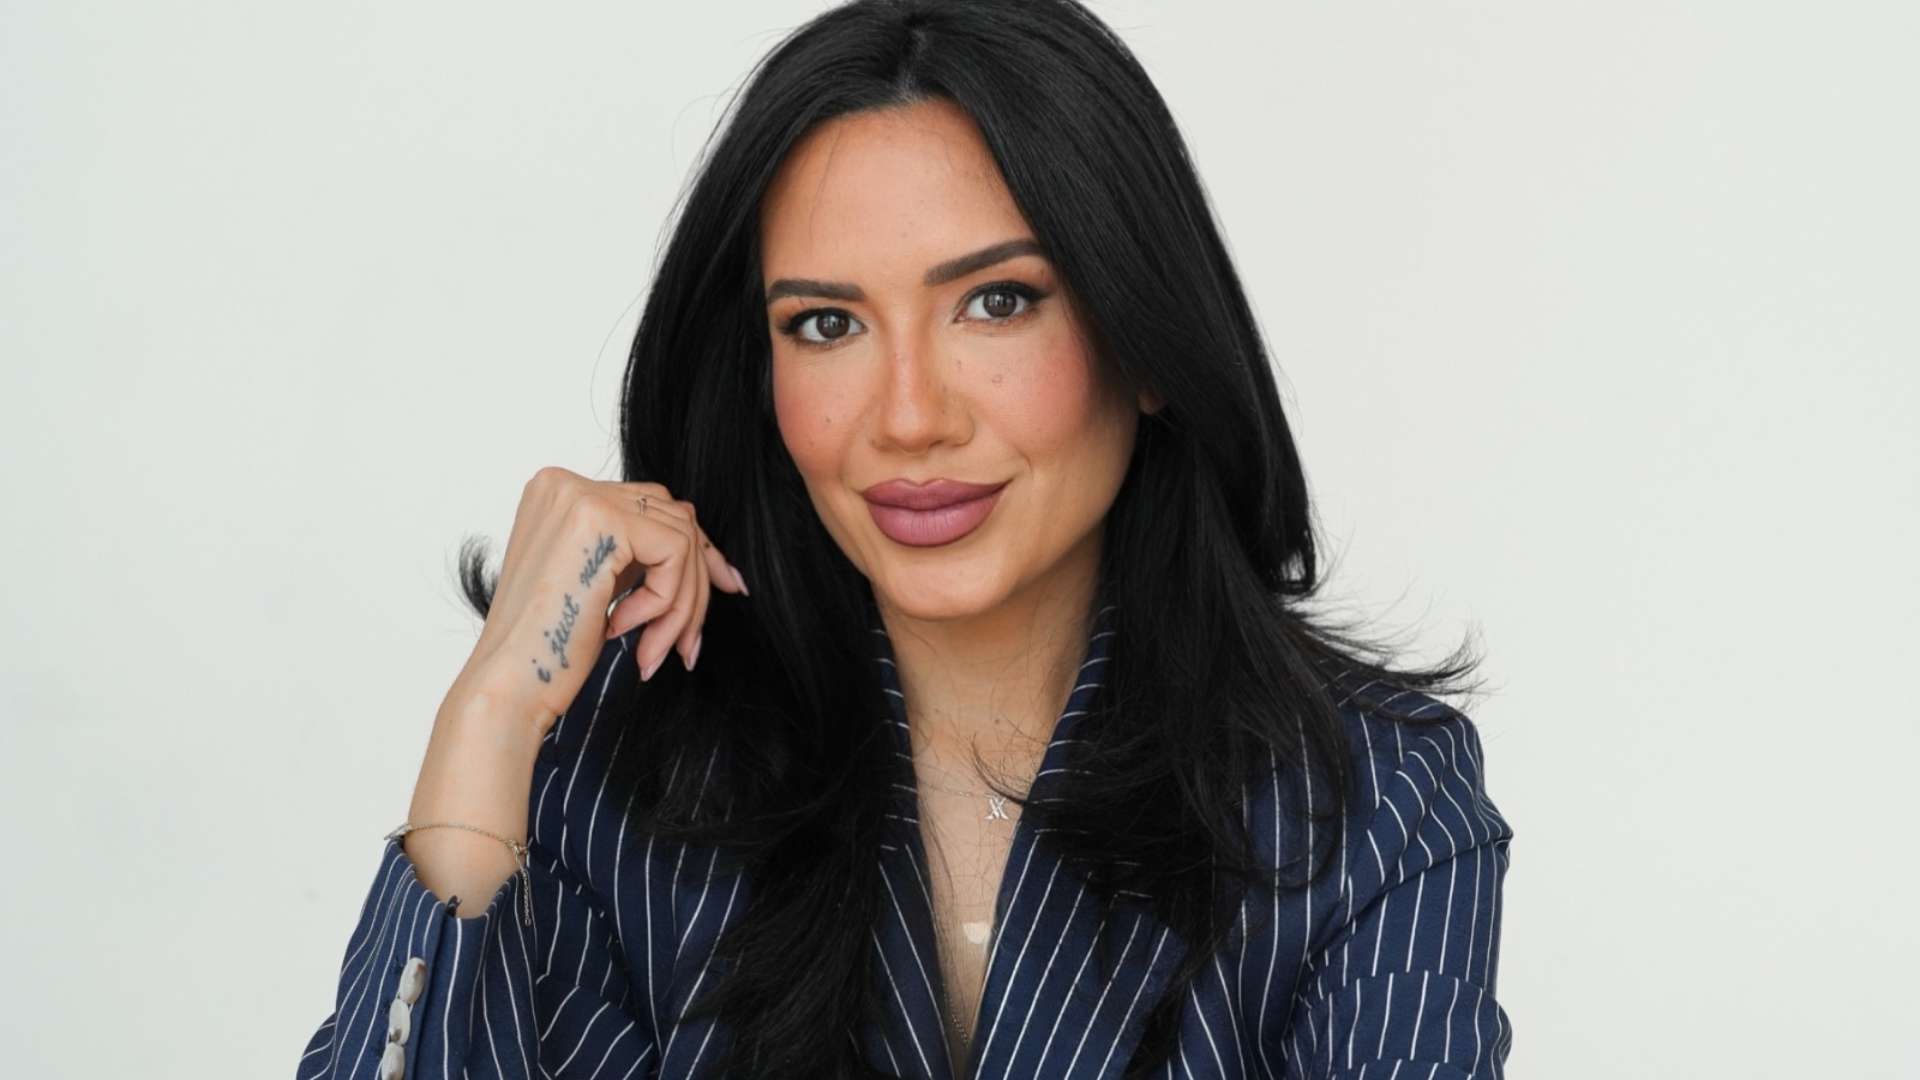
Christiana Maxion, Founder and CEO of MAXION
Consumer apps have never been easier to use. With AI improving navigation, personalization, and responsiveness, platforms now offer a far more seamless experience, helping users move through tasks, content, and decisions with little visible effort. But convenience alone is not the same as value. Recent research found that the average adult now spends 88 days a year on their phone, highlighting both the scale of digital dependence and the urgency of building products that deliver something more meaningful than another scroll session.
Concurrently, expectations have changed. McKinsey has reported that 71% of consumers expect personalized interactions, while KPMG’s UAE research shows that integrity has now overtaken personalization as the strongest driver of customer experience. People still want services that understand them, but they also want trust and clarity that technology is working in their interest.
This is the backdrop for the rise of behavioural AI in consumer apps. The next phase of app design will be judged by its ability to predict what a user may click next, and more by how well it turns intent into action with less friction.
The problem with designing for activity, not action
For years, most consumer platforms have optimized for clicks, scroll depth, watch time, and repeat visits. Those metrics are useful, but incomplete. They show that a user remained active, not whether the user made progress.
A person may spend 20 minutes in a fitness app and still not complete a workout. A user may open a finance platform several times and still delay a decision. Someone on a social app may swipe through dozens of profiles and leave with no meaningful connection, no meeting arranged, and no clearer sense of what they are actually looking for. In each case, the platform can still record engagement, even while the user experiences indecision, overload, or disappointment.
That is why the intention-action gap has become such an important issue in consumer technology. Most people do not fail to act because they lack interest. They fail because friction builds up. Too many options, poor timing, and repetitive interfaces make follow-through harder than it should be. Traditional engagement design often worsens that problem because it rewards prolonged activity instead of successful resolution.
How behavioural AI changes the model
Behavioural AI is valuable because it looks beyond isolated clicks and interprets patterns in context. It can identify hesitation, momentum, preference shifts, and likely drop-off points. More importantly, it can respond to those signals in ways that make decisions easier and outcomes more achievable.
That changes the app’s role. Instead of acting primarily as a feed, a storefront, or a passive interface, it starts to function more like an active guide. It can narrow choices when users are overwhelmed, surface the next best action when intent is clear, and adapt when behaviour suggests a mismatch. This can mean recommending fewer but better options, improving prompts, changing timing, refining compatibility logic, or reducing unnecessary steps between interest and action.
The commercial relevance of this shift is growing. SAP reported that 82% of UAE marketers say AI is central to their personalization efforts, yet only 31% of consumers believe brands actually personalize content to their needs. Data and automation alone are not enough. Relevance depends on using insight in ways that feel useful, proportionate, and credible to the user.
From digital engagement to real-world outcomes
Behavioural AI becomes especially powerful in categories tied to everyday behaviour and human relationships. In social discovery, for example, the challenge has never been a lack of available profiles. It has been helping people move from superficial activity to meaningful connection.
That is where a social platform like MAXION sits within a more important conversation about the future of consumer apps. Success should not be measured only by how many profiles a person sees or how long they stay active on the app. It should be measured by whether the app improves the quality of interactions and increases the likelihood of real-world meetings.
Behavioural AI can support that by learning from interaction patterns. It can identify where conversations stall, what kinds of introductions lead to better follow-through, how timing affects responsiveness, and which recommendation patterns create genuine alignment rather than short-lived engagement. That creates the possibility of designing around success signals that matter outside the app.
This is also highly relevant in the UAE, where AI adoption is already part of everyday life. KPMG reported that 97% of UAE respondents use AI for work, study, or personal purposes. That level of familiarity creates a more sophisticated user base.
The broader point is that consumer AI is becoming more outcome-oriented. Whether the category is education, wellness, finance, or social connection, the products that stand out will be those that reduce noise, respect user intent, and drive real-world progress. The next generation of successful apps will be defined by how effectively they help people do something worthwhile with them.
By Sourav Guha Roy, Practice Head – Cyber Academy, CPX
Prevention remains essential to cybersecurity, but it is no longer enough on its own. As AI-enabled threats become increasingly complex, convincing and harder to detect, a new question is gaining prominence in boardrooms across the region: if an attack succeeds, how quickly can the business recover? How effectively can teams recognize a threat, leaders make critical decisions under pressure and coordinate a response before disruption escalates?
For business leaders, the focus is shifting from simply keeping attackers out to containing damage, restoring critical services and maintaining business continuity. Building this capability requires more than technology safeguards. It means preparing people, establishing clear processes and ensuring teams can act decisively under pressure.
Recovery readiness: From prevention to preparation
Cyber readiness is often measured by what an organization puts in place before an incident: clear responsibilities, tested response plans and technology that supports detection and decision-making. But when an attack succeeds, the real measure of preparedness is how effectively are the people able to use these capabilities to limit disruption and restore critical services.
Cyber resilience extends beyond the initial response. It is an organization’s ability to adapt to disruption, maintain essential functions and recover while managing the wider impact on customers, employees and business performance. The speed and effectiveness of that recovery depend on more than the tools available. People must interpret alerts, assess business impact and make decisions that enable the organization to move forward.
This distinction has important implications for leadership. Preventing every incident may not be realistic, but organizations can prepare for the moments when prevention fails. The priority is to ensure that response plans work in practice, responsibilities are understood and teams can make coordinated decisions under pressure.
Three connected pillars of cyber readiness
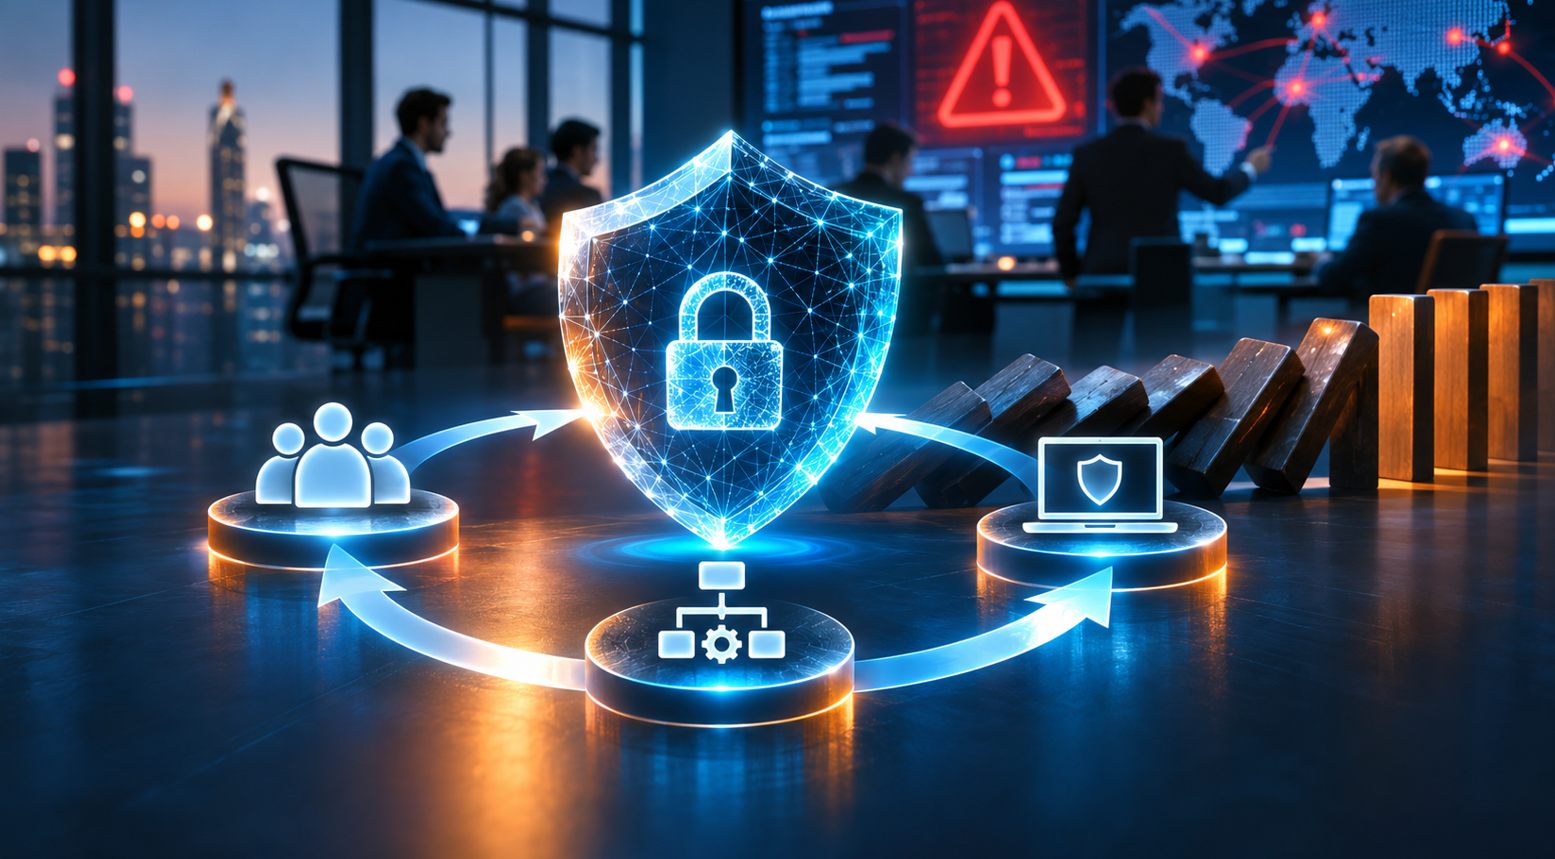
A human-centric approach does not reduce the importance of technology. Instead, it aligns three interdependent pillars: people, process and technology.
- People provide context, judgment and ethical oversight. They need the confidence to pause when an instruction appears unusual, verify a request through a trusted channel and report concerns without delay. In an environment shaped by AI-generated impersonation, these behaviors are increasingly important.
- Process turns individual awareness into a coordinated response. Clear escalation routes, decision authority and defined ways of working help employees and specialist teams understand what happens after a concern is raised. Processes should also clarify the responsible use of AI, including which tools are approved, what information may be shared and how AI-related risks should be reported.
- Technology protects systems and supports human decisions by detecting suspicious activity, controlling access and monitoring how AI and organizational data are used. Yet an alert is only an indication that something requires attention. Without context, ownership and action, it does not create readiness or guarantee a timely recovery.
Consider a finance employee who receives an urgent payment instruction that appears to come from a familiar executive. Technology may flag unusual activity, process determines how the request is verified and escalated, and people apply judgment and involve the right decision-makers.
From the frontline to the boardroom
Cyber readiness should reflect the decisions expected of each role. Employees must recognize and report warning signs. Specialists must assess the impact, coordinate the response and restore operations securely. Leaders must make informed decisions when facts are incomplete, balancing security, continuity and accountability.
Readiness depends on the handoffs between these groups: employees need clear reporting routes, specialists need the authority and information to act, and leaders need timely insight into business impact.
Build capability through a continuous cycle
Human-centric readiness is not achieved through a one-time awareness campaign. A practical model is to Assess, Train and Simulate continuously.
Do employees verify unusual requests? Can specialist teams build a shared view of impact? Do leaders know when to intervene? Can critical services be restored within acceptable timeframes? The findings should feed back into the next assessment and improvement cycle.
Conclusion: Make recovery a business priority
No organization can guarantee that every cyberattack will be prevented. But every organization can decide how prepared it will be when one occurs. That means moving beyond prevention metrics to test how effectively teams contain incidents, protect critical services and restore operations.
The most important shift is to stop treating people as the weakest link and start preparing them as an active part of the defense. This does not mean turning every employee into a cybersecurity expert. It means ensuring that each person knows what to recognize, how to respond and when to escalate.
The strongest organizations will not be those that eliminate every human error. They will be those that give people the judgment, processes and support to prevent a single mistake from becoming a business crisis.
For boards and executive teams, the call to action is clear: ask not only how likely an attack is, but how long the business could operate under disruption. Cyber resilience is ultimately measured not by the absence of incidents, but by the ability to withstand them and recover. The organizations best positioned for the future will be those that make recovery readiness a business priority before the next attack begins.
Exclusive interview with Diego Parra, Managing Partner, Megarme
How are oil and gas companies in the GCC changing the way they inspect and maintain their equipment and infrastructure?
We see a stronger emphasis on equipment condition and the consequences of failure when operators plan inspection. Scheduled inspections remain important, alongside operating history, service conditions and the role each asset plays in the operation.
Two similar pieces of equipment may need different inspection plans because their service conditions, exposure or importance to the operation are different. A critical process line, for example, may require a different approach from a low-consequence utility line. The inspection method, coverage and timing should reflect those differences while meeting the applicable requirements.
Inspection history and equipment monitoring can help maintenance teams identify changes early enough to investigate and plan work. This is particularly useful offshore or where access depends on a shutdown, because arranging people, equipment and materials can take time.
At Megarme, we support this approach by providing condition information from the locations included in the inspection scope. Our findings help the operator and its engineering team decide what needs attention, what requires further assessment and what can be included in a planned maintenance campaign. We aim to make the findings clear enough to support those decisions.
What are the biggest challenges companies face when inspecting and maintaining offshore and onshore facilities, and how does Megarme help address them?
A practical challenge is obtaining a reliable assessment while working within the facility’s operating constraints. Access, process safety and inspection quality have to be planned together. The easiest location to reach may not be the one most likely to deteriorate.
Offshore, marine corrosion and possible fatigue at connections subject to repeated loading need attention. Weather windows, restricted deck space and transport arrangements also affect the work. Under-deck steelwork, derricks and flare structures can be demanding, particularly when inspection must be coordinated with lifting or other activities nearby.
Onshore, congested pipe racks, hot surfaces and operating process systems can restrict access. Isolation requirements and shutdown schedules often determine when work is possible. Entry into tanks or vessels introduces additional atmospheric and rescue considerations.
We help by planning the access and technical work together. An under-deck survey may require surface preparation, thickness measurements and weld examination before the engineering team can assess the findings and approve repairs. Identifying these dependencies early helps the operator prepare the work.
Our reports need to make inspection coverage and limitations clear. Work during operation is considered only where the process conditions, risk assessment, permits and required isolations allow it.
How does rope access help Megarme carry out inspection and maintenance work in hard-to-reach areas safely and efficiently?
Rope access allows us to position a qualified technician directly at the work location, including beneath a jetty, beside an elevated pipe support or at a derrick connection. For localised inspection and repair, it can reduce the access structures, material handling and space required.
We are an IRATA Operator and Trainer member. The normal rope access arrangement uses two independently anchored lines: a working line and a safety line. An IRATA Level 3 supervisor oversees the rope access safety arrangements, including equipment checks, rope protection, communication and a rescue plan suited to the location. Team size must support both the task and a potential rescue.
Our technicians also need the qualifications and authorisations for the work being performed. Rope access competence is separate from competence in NDT, welding or coating inspection. An ultrasonic examination carried out on ropes must meet the applicable inspection requirements, including calibration, surface preparation, probe positioning and coverage.
We select the access method around the task, duration, equipment loads and rescue requirements. Depending on the work, that may involve rope access alone or a combination of access arrangements. The practical benefit is being able to reach the required locations with a method suited to the inspection or repair.
How does Megarme use non-destructive testing (NDT) to identify corrosion, cracks and other damage before they become serious problems?
We use NDT to assess remaining wall thickness and look for indications of cracking or other damage. We select the method to suit the material, expected deterioration and inspection requirements.
For pipework corrosion, ultrasonic measurements establish wall thickness at the inspected locations. If we find an unusually low reading, we verify it, promptly raise any critical concern and extend the examination as required to establish the extent of the thinning. Corrosion mapping can provide more detailed coverage where localised attack is suspected. The lowest measured thickness and size of the affected area matter, because an average can conceal a severely thinned location.
Magnetic particle testing can reveal surface and near-surface discontinuities in ferromagnetic materials, such as carbon steel. Penetrant testing can reveal discontinuities open to the surface in suitable nonporous materials. Ultrasonic testing, including phased array, and radiography can be used to examine welds for internal discontinuities. Selection depends on the expected damage, component geometry and applicable requirements; each method has limitations.
We record the component, examination location, coverage, measurements and relevant images or scan data. The findings support the responsible engineer’s decision on further assessment, monitoring or repair. Repaired welds are re-examined as required by the applicable procedure and acceptance criteria. Qualified personnel, suitable procedures and prompt reporting are essential to making the results useful.
How do extreme heat, humidity and salt exposure in the Gulf affect industrial equipment, and what can companies do to protect their assets?
In the UAE and Saudi Arabia, asset protection has to reflect the location. Offshore and coastal facilities face salt exposure and periods of high humidity alongside heat. Further inland, heat and dust become more prominent considerations. The protection system must suit both the local exposure and the equipment’s operating conditions.
We pay particular attention to pipe supports, bolted connections, undersides of structures and insulated pipework. Corrosion can develop in a small, critical area while the wider structure appears acceptable. Moisture entering through damaged insulation cladding can remain against the steel, making targeted inspection and repairs to water-entry points important.
Coating performance depends on preparation and application. Salt, dust and other contamination must be controlled to the specified cleanliness limits, with the required surface preparation and coating thickness verified. Steel temperatures in summer can exceed a product’s application limits. Cooler hours still require checks for humidity and condensation. Some specifications require the steel to remain at least 3°C above the dew point, alongside the product’s other temperature and humidity limits.
Our inspection, surface preparation, coating and repair work can help address deterioration and its causes. Metal loss needs assessment and, where required, an approved repair before protection is reinstated. Leaving a water trap or damaged insulation seal in place can expose the asset to the same problem again.
How does Megarme help oil and gas operators extend the life of their assets while maintaining safety standards?
We support asset life extension by gathering inspection evidence and carrying out approved maintenance or repairs. The starting point is understanding the condition of the equipment, the extent of any damage and its significance for continued operation.
For pipework, thickness measurements and corrosion mapping provide information for assessing metal loss. Our access capability helps reach components that would otherwise be difficult to examine or replace. The inspection scope needs to reflect the expected damage and provide the information required for the engineering assessment.
Our maintenance and repair scope can include surface preparation, coating, work on columns and piping, structural welding and composite repairs, where appropriate to the assessed condition and approved scope. Composite repairs require an engineered design approved for the specific damage and service conditions, controlled installation and the required inspection and verification. Completed work needs the specified quality records before acceptance.
Life extension also requires a plan beyond the immediate intervention. The operator needs to know what should be monitored, when further inspection is required and which operating limits apply. We contribute inspection data and execution capability. The responsible operator and engineering authority determine fitness for continued service and approve any extension of operating life.
What steps does Megarme take to protect workers when carrying out inspection and maintenance work in challenging environments?
We plan our work around a task risk assessment, competent supervision, personnel fit for the assigned work and the facility’s permit requirements. The controls must be confirmed at the worksite, and any change in scope or conditions requires reassessment.
At operating facilities, this includes verified energy isolation, atmospheric testing and monitoring as required, and controls for hazards such as hydrogen sulphide or flammable atmospheres. We seek to avoid confined-space entry where a suitable alternative exists. Where entry is necessary, the arrangements must address unsafe oxygen levels and other identified hazards, with suitable ventilation, communication and a rescue plan specific to that space.
At height, we consider the people below as well as the technicians. Tools need suitable retention and checked attachment points, with exclusion zones appropriate to the task. Heavy equipment requires its own handling and securing arrangements. Accounting for tools when work is complete helps prevent a later dropped-object hazard.
Our heat management arrangements need to reflect the site conditions, workload and protective clothing. The assessment guides acclimatisation, work and rest arrangements, hydration and access to shaded or cooled recovery areas.
We expect personnel to stop work when conditions are unsafe. Supervisors must respond to fatigue, changing weather and any condition that compromises the controls or rescue arrangements.
How are new technologies changing the way oil and gas companies inspect equipment and plan maintenance?
Technology can improve inspection coverage and the speed at which information reaches maintenance teams. Across the industry, drones can support visual surveys, robots can carry sensors across suitable surfaces, and permanent monitoring can identify changes between periodic inspections. Their suitability depends on the asset and the information required.
Encoded ultrasonic scanning is a practical example. It links measurements to their positions, allowing wall loss to be mapped and compared with later examinations when the scan locations and measurement conditions are comparable. Digital records can connect those results with the asset reference, earlier findings and repair history.
We assess a technology by the information it provides and the decision it supports. A visual image may identify an area for closer examination. Confirming wall loss or characterising a defect requires a method suited to that task. AI tools can assist with screening where their performance has been validated for the intended use, with qualified personnel reviewing the results.
Our priority is to select methods that suit the component and expected damage, and to produce clear, traceable records. We use inspection findings to plan any further examination and support the engineering assessment and approval of required repairs.
How can companies reduce maintenance costs and downtime without compromising safety or equipment reliability?
Better preparation and fewer repeat interventions can help control maintenance costs and downtime. The cost of a task includes access, mobilisation, materials, permits, isolation, production disruption and verification. These need to be considered together when comparing ways to execute the work.
Before a shutdown, available inspection findings should be used to define repair scopes, prepare materials and spare parts, agree procedures and secure the necessary personnel. Operations, engineering and maintenance teams need to resolve dependencies early. Discovering that a repair needs additional materials or approval after equipment has been shut down can put the programme under pressure.
We help by coordinating compatible activities within an access campaign. Elevated steelwork, for example, may need condition assessment, NDT, a dropped-object survey and authorised coating repairs. When safely sequenced, these activities can share access arrangements and reduce repeat mobilisation. Required approvals and inspection hold points still apply.
Prompt decisions on findings and investigation of recurring defects also help prevent delay and rework. Useful performance measures include total maintenance cost, unplanned downtime, repeat failures and closure of critical findings. Any cost-reduction plan must preserve required inspections and the maintenance and testing of safety-critical equipment.
What are the main inspection, maintenance and safety challenges you expect the GCC oil and gas industry to face over the next few years, and how is Megarme preparing for them?
We expect an important challenge to be balancing maintenance of operating assets with inspection needs during construction and commissioning. When shutdowns and project activities overlap, there can be pressure on the availability of experienced personnel and technical supervision.
Advanced NDT technicians, welding and coating inspectors, and rope access supervisors need the competence and approvals for each assignment. Our preparation includes attention to training, personnel allocation and the technical support available to site teams. Resources need to match the work being accepted.
The quality of records handed over from construction to operations is another priority. Traceable weld records, baseline thickness measurements and coating inspection results give maintenance teams a useful starting point. Consistent component identification helps later inspection results be compared with the correct earlier records.
For existing facilities, corrosion in difficult-to-access areas and beneath insulation will continue to require attention. On safety, overlapping inspection, lifting and hot work need careful coordination. Heat exposure and fatigue also need to be reflected in staffing and schedules.
We are focusing on consistent technical review, equipment readiness and clear reporting across our regional operations. Our aim is to keep the standard of execution consistent as workloads change, with appropriate supervision and follow-up on significant findings.
Tech Features
SANS Institute Strengthens Regional Cyber Readiness with AI-Focused Training at SANS Gulf Region 2026

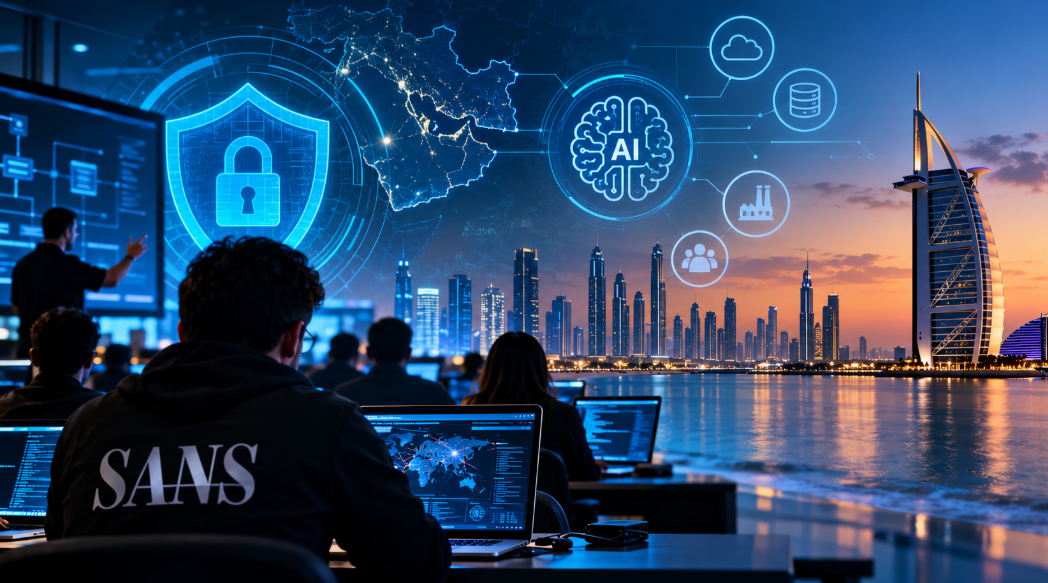
SANS Institute, a global leader in cybersecurity training and certifications, has announced the 2026 edition of SANS Gulf Region. The event every year brings together cybersecurity professionals for an extensive program of hands-on training designed to address the Middle East’s threat landscape. Taking place from October 31 to November 26, 2026, at the Hilton Dubai Jumeirah Beach Resort, the event will feature 13 specialized courses and two NetWars tournaments. The program will cover key areas such as AI security, advanced threat detection, industrial control systems security and cyber resilience.
As Middle East enterprises advance digital transformation and adopt more AI-driven technologies, cybersecurity investment continues to grow. According to Mordor Intelligence, the regional cybersecurity market is estimated to reach USD 23.54 billion in 2026, growing at a CAGR of 14.55% through 2031. However, there are still challenges in developing the expertise needed to secure complex digital environments. PwC’s 2026 Global Digital Trust Insights: Middle East findings reveals that 53% of regional respondents identified lack of knowledge in applying AI to cyber defense as a major hurdle, highlighting the need for specialized cybersecurity training to keep pace with technological advancements.
As AI is integrated into business processes, cybersecurity expertise should go beyond traditional threat detection and response to securing AI systems themselves. For going through this shift, SANS Institute has developed the AI Security Maturity Model – Gulf Region. The framework provides a structured approach to evaluating AI security readiness, identifying gaps and prioritizing improvements across AI protection, utilization and governance. It offers a clearer path towards building stronger, more mature AI security practices, while reinforcing the need for continuous, hands-on training.
“The Middle East has seen remarkable progress in digital transformation, but the pace of adopting technologies must be matched by an equally strong investment in cybersecurity capabilities,” says Ned Baltagi, Managing Director, Middle East, Turkey and Africa at SANS Institute. “As businesses incorporate AI and interconnected systems, the challenge is ensuring that they have the specialized skills and practical experience to manage the risks that come with it. This calls for a shift from reactive skills development to continuous, forward-looking training that anticipates how threats and technologies are evolving. With SANS Gulf Region 2026, we are putting this approach into practice, focusing on the skills and real-world challenges that matter most to companies across the region.”
This year’s curriculum covers five key areas, including Cyber Defense, Offensive Operations, Industrial Control Systems, Cloud and AI Security, and Leadership. The program introduces SEC545: GenAI and LLM Application Security, a new course focused on securing generative AI applications and large language models. Also, there are major updates to LDR519: Cybersecurity Governance, Risk, and Compliance. Six courses are focusing on AI, reflecting the growing importance of understanding and managing AI-related cybersecurity risks.
Other key training areas include network monitoring and threat detection, enterprise penetration testing, security automation for red, blue and purple teams, ICS/SCADA protection, and defensible security architecture built around Zero Trust principles. Together, these courses address a broad range of technical and strategic requirements, helping to strengthen capabilities across both traditional and new cybersecurity domains.
Complementing the training program, the event will feature two NetWars Core tournaments, giving participants an interactive environment to apply their skills to simulated cybersecurity challenges. This year’s AI-forward scenarios will explore areas like prompt injection, malware reverse engineering, MFA bypass, web application security and IoT vulnerabilities. Set within a fictional organization facing compromised systems and vulnerable AI models, attendees should investigate and respond to interconnected security threats.
The event will also host a series of evening community talks. Sessions will explore cybersecurity leadership, the role of AI in learning, and modern influence operations, with contributions from SANS experts including Mark Williams and Jeff McJunkin. The courses will be available in person and through online live sessions.
Through SANS Gulf Region 2026, SANS Institute continues its commitment to strengthening cybersecurity capabilities across the region, supporting businesses in developing the technical expertise, leadership skills and practical readiness needed to protect complex digital environments.

H&H’s AED 30 Billion Dubai Peninsula Development Takes Shape, Home to Five World-Renowned Hospitality Brands

The Best Festive Turkey Takeaways in Abu Dhabi This Christmas

Qatar Airways Connects Doha to Caracas, Venezuela, and Bogotá, Colombia with First Flight


-
 Trending1 year ago
OPPO A6 Pro 5G Review: Reliable Daily Driver
-

 Tech News2 years ago
Denodo Bolsters Executive Team by Hiring Christophe Culine as its Chief Revenue Officer
-
 VAR2 years ago
Microsoft Launches New Surface Copilot+ PCs for Business
-
 Automotive2 years ago
AGMC Launches the RIDDARA RD6 High Performance Fully Electric 4×4 Pickup
-
 VAR11 months ago
Huawei Nova 14 Pro Review: Where Camera Excellence Meets Ecosystem Evolution
-
Tech Interviews3 years ago
Navigating the Cybersecurity Landscape in Hybrid Work Environments
-

 Hospitality2 years ago
Gulfood 2025 30th Edition Kicks Off Today, Setting New Benchmarks in F&B Growth and Innovation
-

 Tech News1 year ago
Nothing Launches flagship Nothing Phone (3) and Headphone (1) in theme with the Iconic Museum of the Future in Dubai