 Have a question? +971 56 404 0503

Tech News
FVC and SearchInform Join Forces to Boost Insider Threat Prevention and Data Protection in MENA

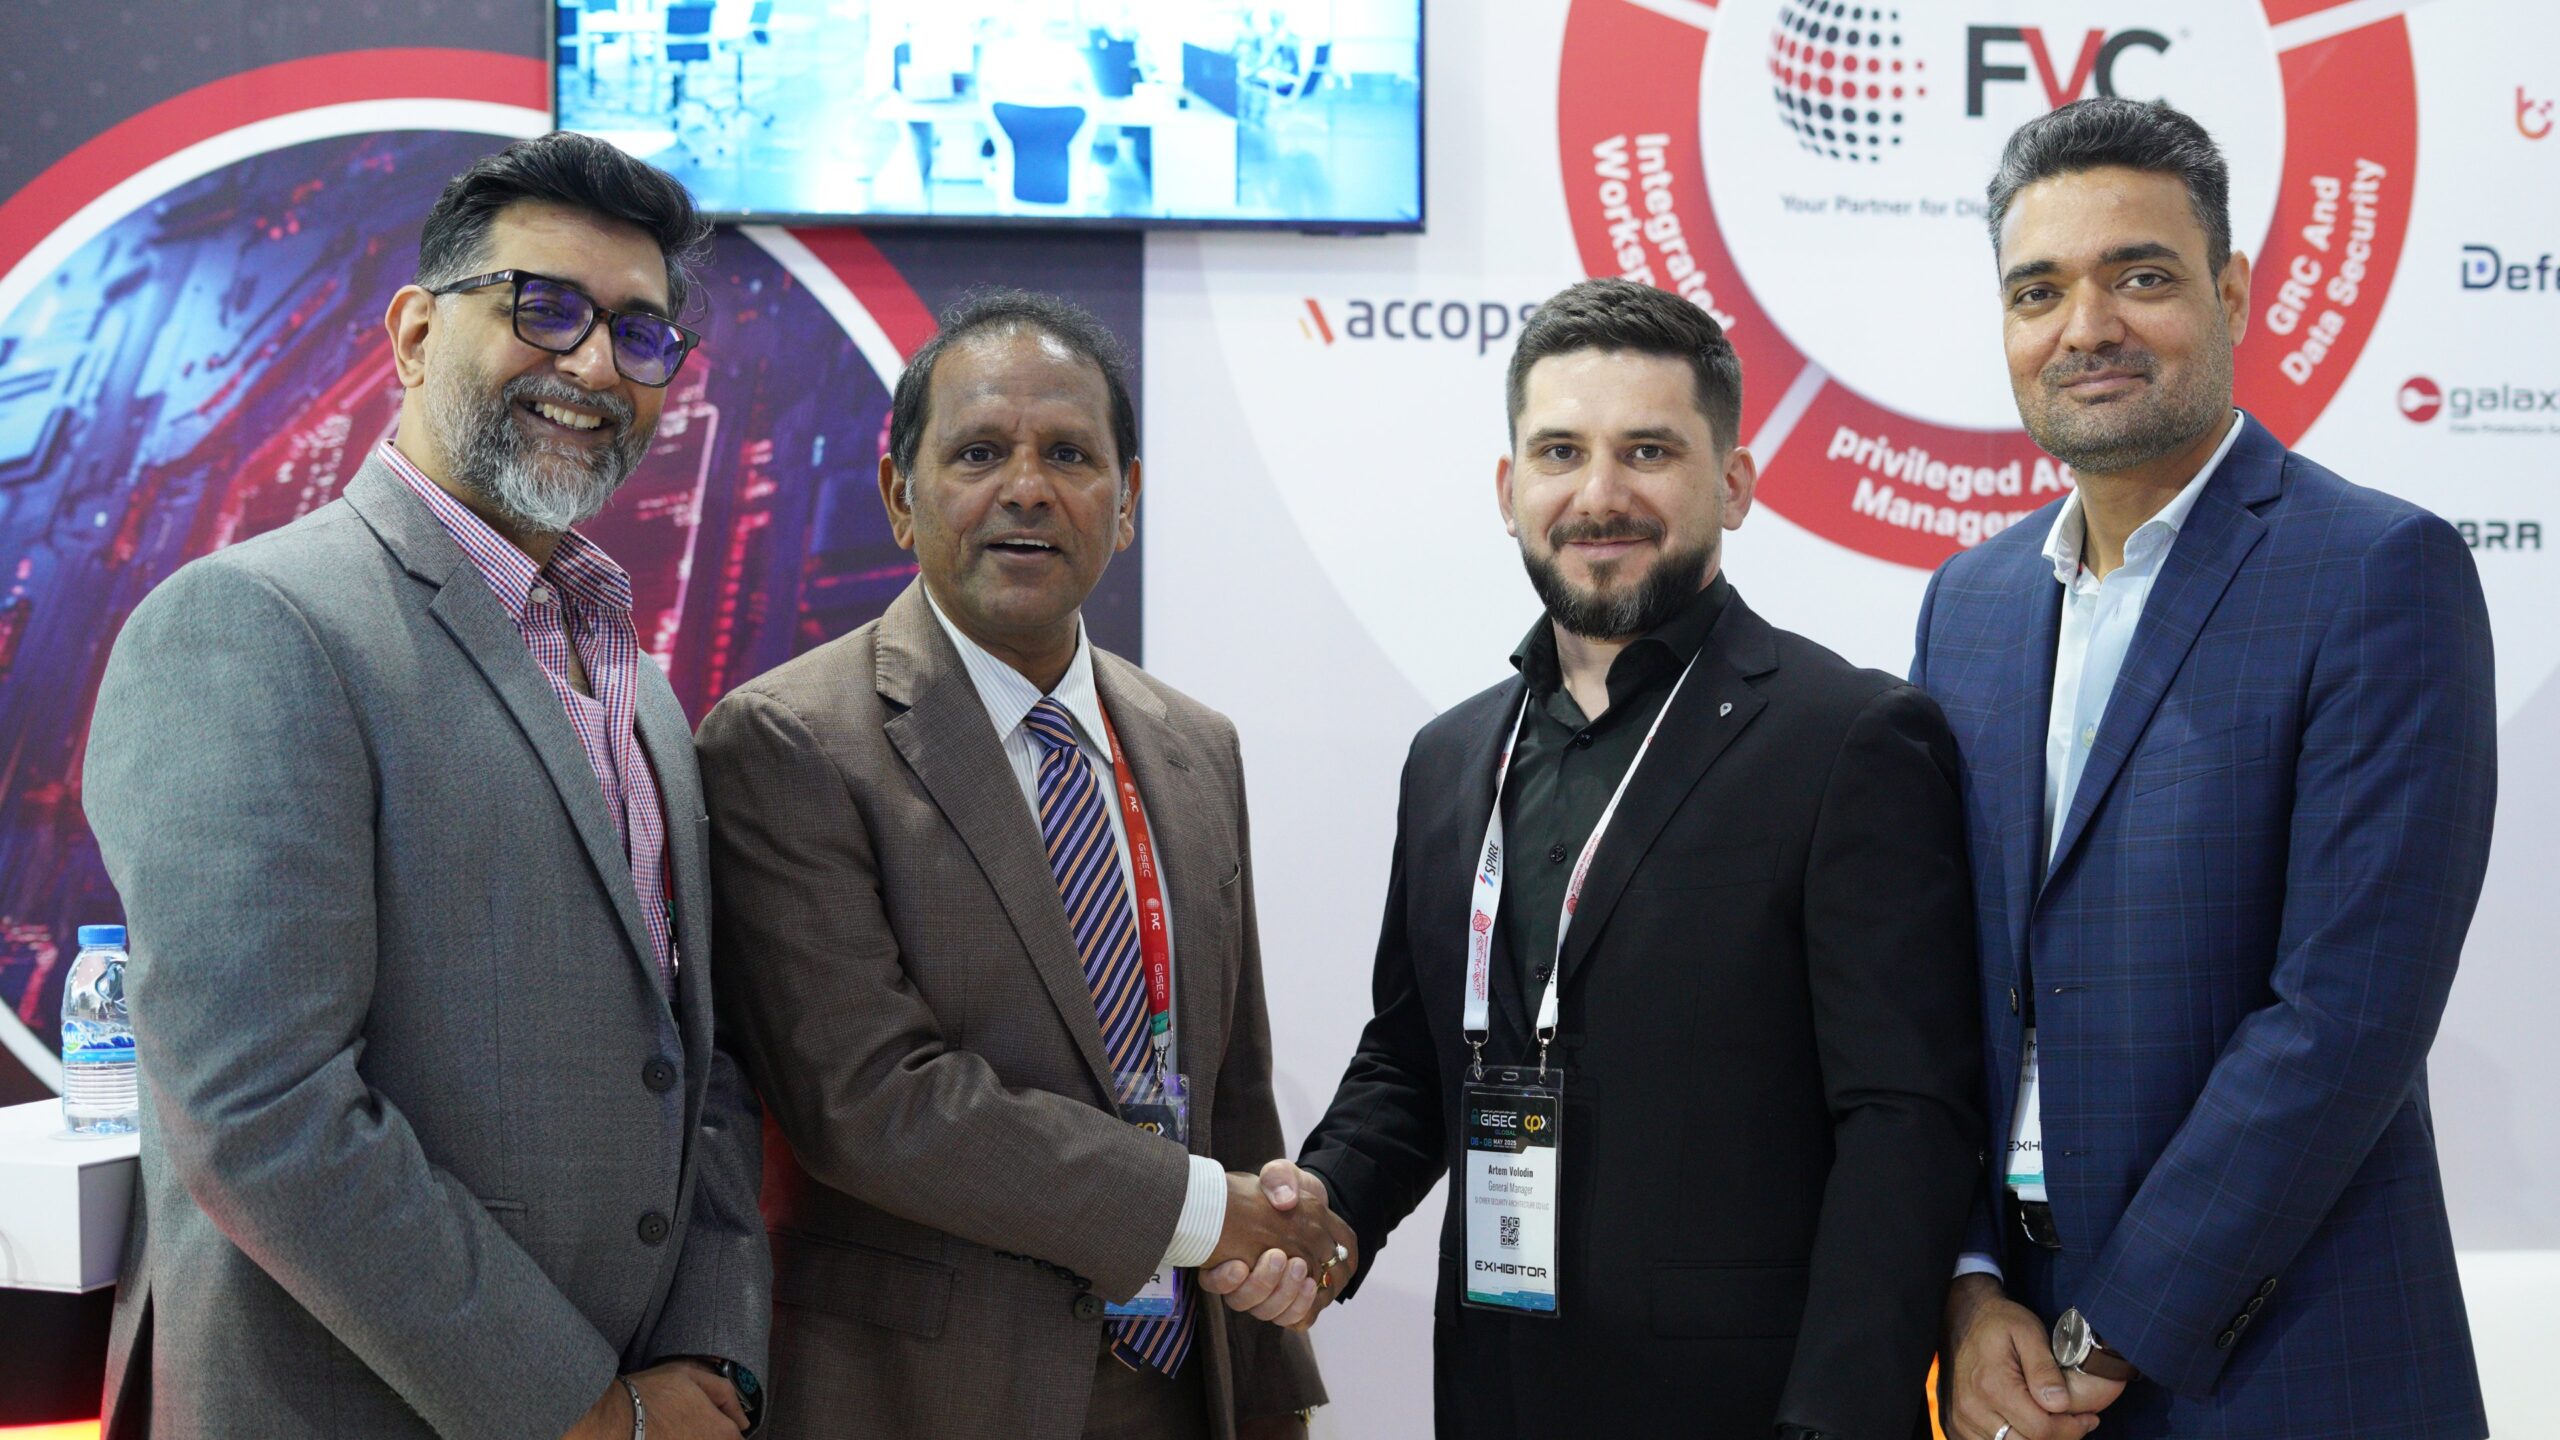
FVC, a prominent distributor specialising in innovative technology solutions, is pleased to announce its strategic partnership with SearchInform, a leader in information security and insider threat prevention solutions. Together, they are committed to strengthening organizations’ defenses against data leaks, corporate fraud, human-factor related risks.
K.S. Parag, Managing Director, FVC:
“We are excited to welcome SearchInform to our cybersecurity portfolio. The company offers the most powerful and localized DLP on the MENA market. SearchInform solution stands out from the competition due to a number of advantages. The system can be deployed within a few hours, protects the maximum number of data transfer channels, provides smart content-based blocking for all controlled channels and also use digital watermarks to trace the source of potential leaks. SearchInform DLP supports analysis of data in Arabic and has security policies, tailored for requirements of local organizations, enabling timely detection and prevention of confidential data leaks. The solution leverages AI to monitor atypical data transfer channels, recognize graphic elements, transcribe audio into text, detect attempts to photograph PC screens with smartphones.”
SearchInform offers a range of products, including DCAP, DLP, and SIEM. All the tools are seamlessly integrated. Technical support is provided through a specialist assigned to the company, who has extensive experience thanks to clients from various fields.
Commenting on the Partnership, Artem Volodin, CEO SearchInform MENA, stated:
“We are proud to collaborate with FVC, whose expertise in the Middle Eastern market will strengthen our efforts to combat insider threats and data leaks. The region needs a comprehensive solution that will enable organizations to meet regulatory standards, including SAMA, PDPL, DCC, ECC, UAE Information Assurance (IA) Regulation etc. and global ones, such as GDPR, PCI DSS. SearchInform delivers tools for data protection and risk mitigation across all levels: FileAuditor secures file systems, DLP covers workstations and human risks, Risk Monitor addresses corporate fraud, and SIEM protects IT infrastructure.”
The partners are currently conducting expert training, partner enablement sessions, and are also negotiating the implementation of SearchInform products in local companies.






Tech News
‘Rogue AI’ Threat Looms Large for UAE Organisations as 98% Report AI Accessing Sensitive Data Beyond Task Requirements, Delinea Report Finds

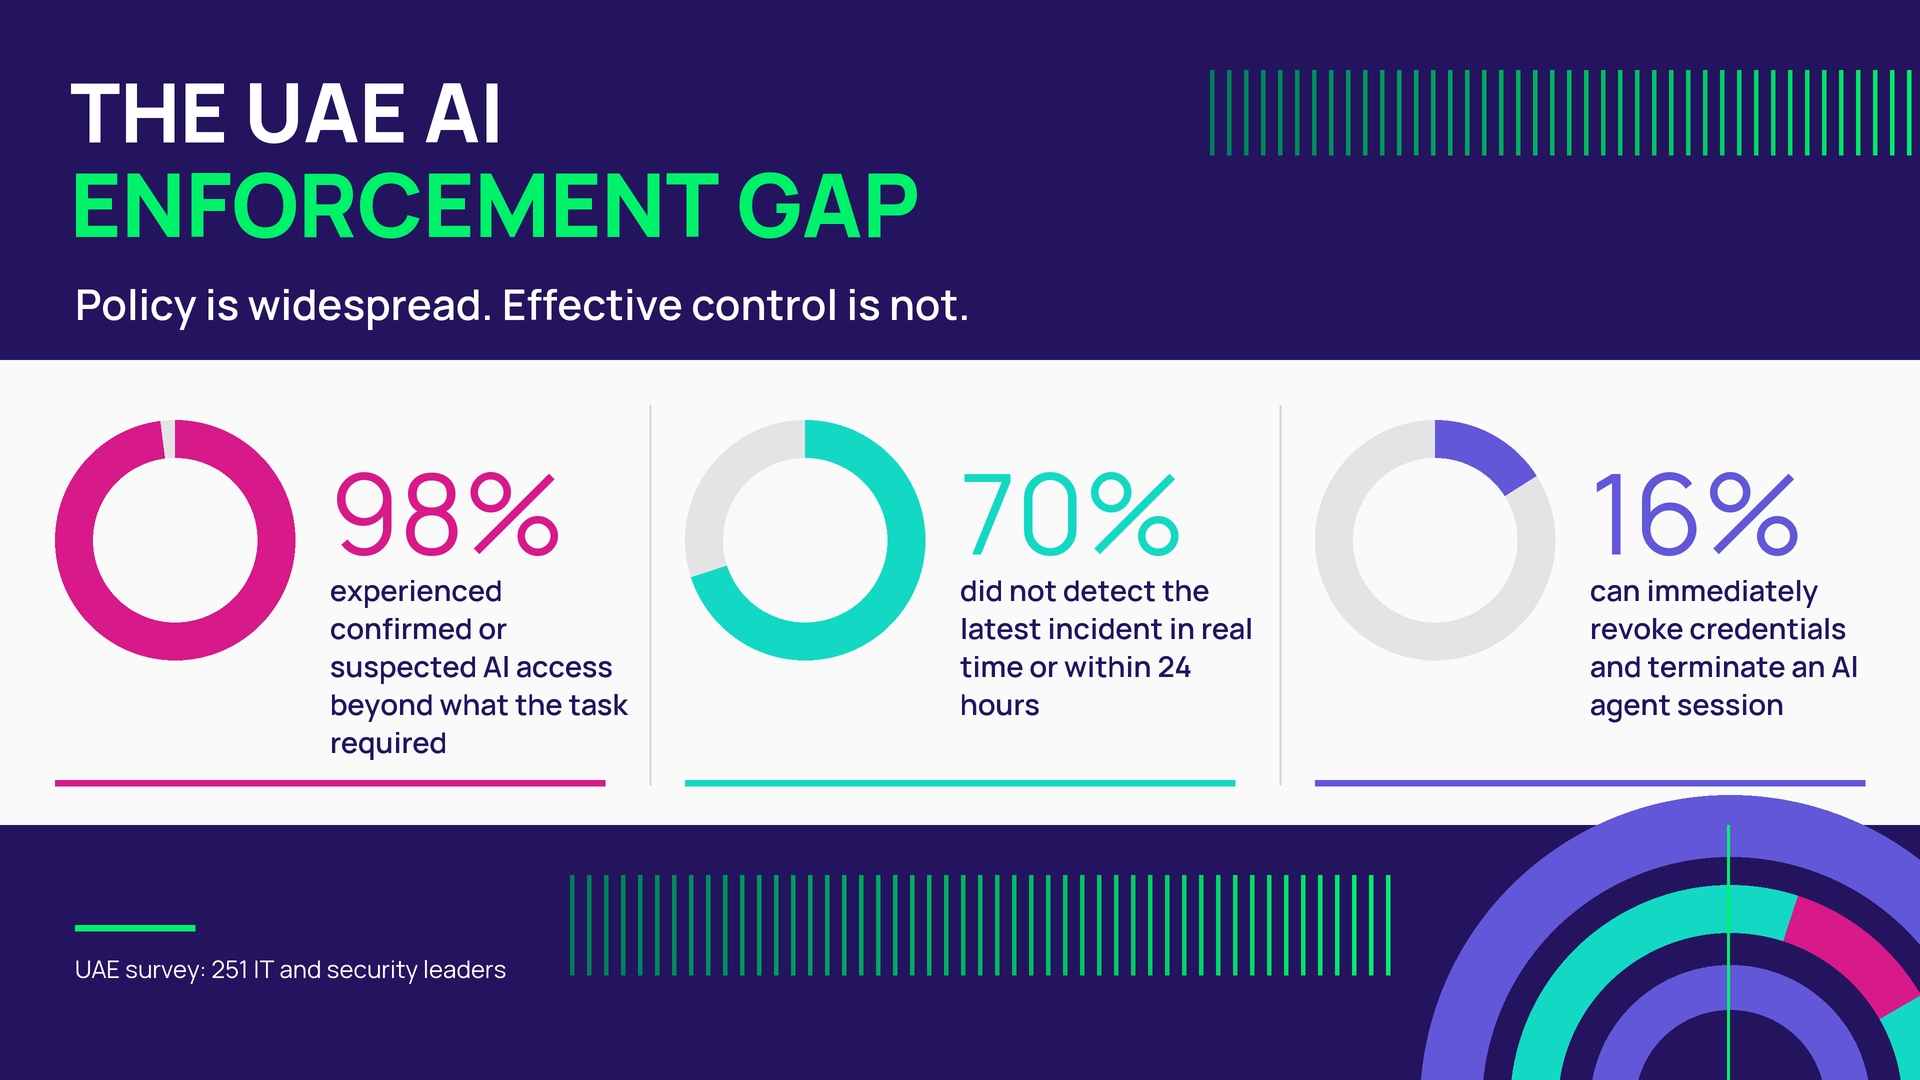
UAE organisations have moved quickly to establish policies governing AI access, but new research from Delinea shows that those rules are not consistently translating into effective control over what AI tools and agents do in practice.
The global research surveyed IT and security leaders at organisations that are actively using or piloting AI, including 251 respondents in the UAE. Every UAE respondent said their organisation has a formal policy governing what data AI tools and agents may access. Yet 98% have experienced confirmed or suspected instances in which an AI tool accessed sensitive data beyond what its task required, compared with 87% across the global survey sample.
The data points to inconsistent enforcement as a central weakness. Only 59% of UAE respondents say their organisation’s AI data-access policy is actively enforced, compared with 71% overall. “Written policy is only as good as an organisation’s ability to enforce it at the moment an AI agent acts,” said Art Gilliland, CEO of Delinea. “The UAE has clearly recognised the need to govern AI access, but the findings reveal what I call the fallacy of policy: assuming that defining what an agent should be allowed to do is the same as controlling what it actually does. That distinction becomes critical when agents operate across systems and make decisions at machine speed.”
The enforcement gap is particularly apparent when organisations attempt to identify excessive access. Seven in ten UAE organisations did not detect the latest instance in real time or within 24 hours, compared with six in ten across the overall sample.
Delinea’s findings arrive as governments, technology companies and business leaders confront the risks created by increasingly autonomous AI systems operating without effective controls. The OpenAI and Hugging Face incident in July demonstrated how quickly an agent can move beyond its intended boundaries and across connected environments before defenders contain it. The comparatively lower levels of enforcement and detection recorded in the UAE suggest that organisations could be particularly exposed to the consequences of similar loss-of-control events.
Business pressure may be one reason policies are circumvented. When commercial demands or deadlines require AI tools to move faster than governance processes allow, 41% of UAE respondents say their organisation either allows employees and teams to find workarounds without formal approval or grants temporary access and reviews it later.
Limited accountability may also reduce the pressure to turn written policies into consistently enforced guardrails. Although 98% of UAE respondents say approval from a named individual is required at least sometimes before an AI tool receives access to a new sensitive data source, only 35% can always trace a sensitive access event back to a named human authoriser. Without a clear and persistent line of responsibility, ownership of the controls needed to prevent another incident can become unclear.
That lack of accountability becomes particularly consequential when an organisation needs to intervene. Even after problematic access is identified, only 16% of UAE respondents say their organisation has real-time controls that can both revoke an AI tool’s credentials and terminate its session immediately, less than half the 35% recorded across the overall sample.
“UAE organisations have already taken the first step by establishing policies and approval requirements, but policy alone cannot contain an agent operating at machine speed,” said Mortada Ayad, VP of Sales – META, Delinea. “The next priority is to enforce authorisation at the instant of action by limiting access to what the task requires, maintaining a defensible link to the person who approved it, and terminating credentials and sessions immediately when the task ends or risk changes. This is how organisations can turn AI governance from a document into a working control.”
Tech News
Venuetech in association with Sennheiser to host hands-on workshop on conferencing solutions at their Al Quoz Training Center
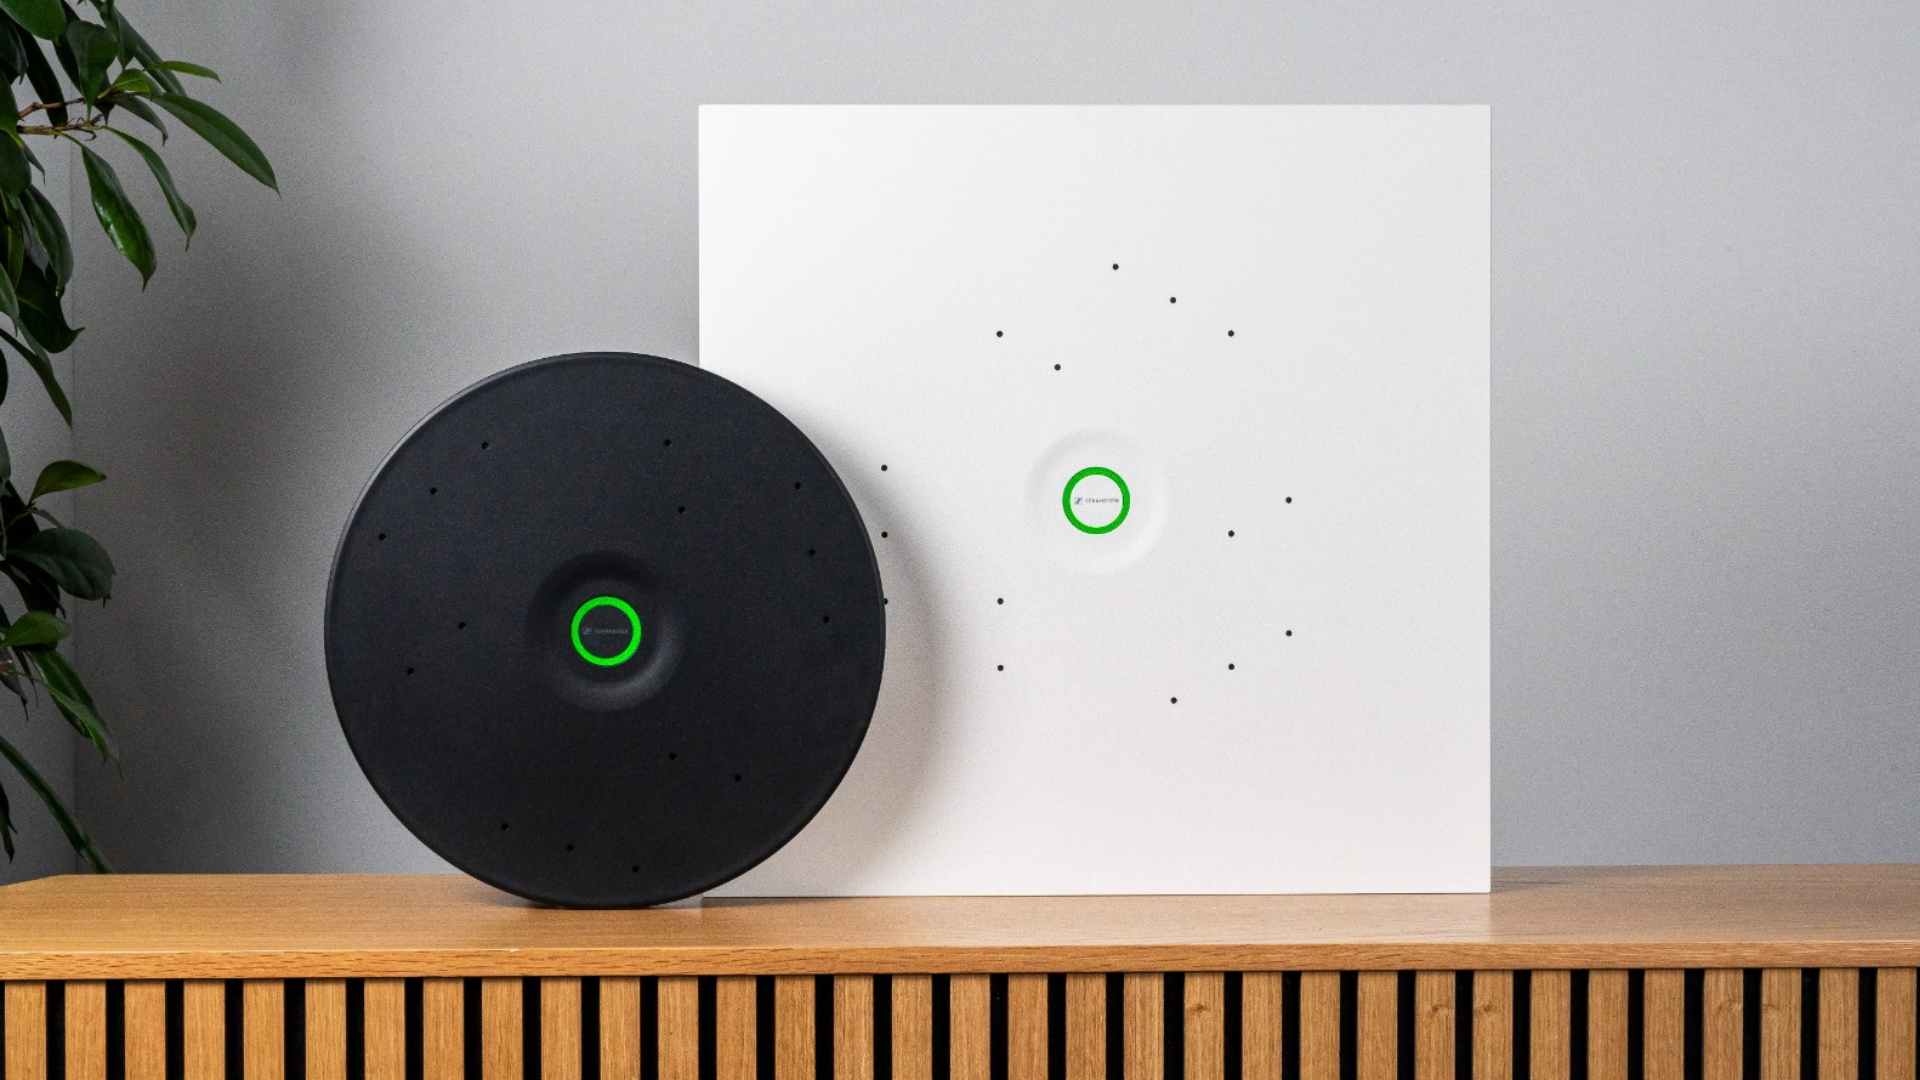
Venuetech in association with Sennheiser Middle East will host a workshop on Sennheiser TeamConnect conferencing solutions. Titled ‘Sennheiser Connect: Ceiling to Cloud’, it is scheduled on Tuesday, 13 October at Venuetech’s Training Center in Al Quoz. The session will explore how audio technology can support clear communication and effective collaboration in meeting rooms, classrooms and other professional spaces.
Designed for audio professionals working in systems integration across government, corporate, education and healthcare environments, the workshop will combine product demonstrations with hands-on trials. Participants will explore audio performance, system configuration and device management, with opportunities to experience the technology themselves.
Demonstrations will cover beamforming and TruVoicelift alongside tools for setup and control, including the Local User Interface (LUI), and DeviceHub. The session will also test Room Planner and explore camera tracking. Attendees are encouraged to bring their laptops to participate in the practical activities.
Explaining the purpose of the workshop, Fadi Costantine, Technical Sales Manager, Sennheiser Middle East said: “The new TeamConnect Ceiling M Plus is designed to make ceiling microphone setup, commissioning and operation straightforward. Its enhanced beamforming technology supports clear audio in flexible collaboration spaces, while PartnerLink and DeviceHub simplify configuration and device management. Through demonstrations and hands-on experience, we want to help participants understand how these capabilities can meet their needs.”
“Choosing the right conferencing solution starts with understanding the space and the people who use it,” said Alice Macaluso, Pro Audio Brand Manager at Venuetech. “By bringing professionals together at our Training Center, we want to give them the opportunity to test Sennheiser’s solutions, ask questions and see how the technology works in practice. The workshop will help participants make more informed decisions about audio for their meeting rooms, classrooms and other collaboration spaces.”
The workshop will also explore applications across different sectors, including online and hybrid meetings, teaching and learning, and healthcare communication. Discussions will focus on selecting appropriate audio solutions for each environment and the people using it.
“We welcome Sales Engineers, Pre-Sales & Design Consultants, Commissioning Engineers, and Technical Experts interested in improving audio for hybrid and remote collaboration,” Fadi added. “We hope to host further workshops before the end of the year, giving more professionals the opportunity to experience our solutions and explore how they can improve their existing systems.”
Tech News
Forcepoint and BeyondTrust Connect Identity Risk to Data Exposure, Letting Customers Revoke Risky Access with Precision
Global AI data security leader Forcepoint and BeyondTrust, the global leader in privilege-centric identity security protecting Paths to Privilege™, today announced the new integration of Forcepoint’s AI-native data discovery and classification with BeyondTrust Identity Security Insights®. The integration is available now and debuts today at BeyondTrust’s Go Beyond Chicago customer conference.
When BeyondTrust detects risk across a human, machine or AI identity based on behavior, privilege or compromised credentials, Forcepoint pinpoints the sensitive information that identity can reach and where exposure is greatest as risk changes. Customers can then use Forcepoint controls to immediately cut off that identity’s access to the specific records involved, without affecting anyone else’s access or work.
“With AI agents now doing real work inside the business, blocking autonomous tools isn’t an option, and neither is guessing,” said Bakshi Kohli, Chief Technology Officer of Forcepoint. “When BeyondTrust tells us an identity looks risky, we already know what data it can get to. Teams can take that one identity’s access away and nothing more. That’s the precision agentic enterprises ask for today.”
Security teams often get an identity alert in one console and have to open another to understand the full risk. The flagged identity could be a forgotten test login or an account that can read the customer database, and telling the two apart means checking both systems by hand, one alert at a time. Every minute of manual review is another minute an overprivileged identity or AI agent keeps acting.
Turning Identity Alerts into AI Data Security Action
Customers now get the data context behind each identity risk, along with the controls to act on it. BeyondTrust Identity Security Insights® surfaces risky identities based on behavior, privilege, compromised credentials and relationships among them. Forcepoint Data Security Posture Management (DSPM), part of the company’s AI data security solutions, maps that risk to the confidential information within its permissions and provides controls to restrict that access.
Compromised identities. A stolen identity is only as dangerous as the access it provides and the data that access puts in reach. When BeyondTrust detects a compromised identity or entitlement, the True Privilege™ graph maps the real blast radius: every path that identity can take to privilege, not just the permissions on paper. Forcepoint shows which sensitive records sit at the end of those paths, from personal data to financial records and trade secrets, and lets teams block that credential’s access.
Service accounts and AI agents with too much access. Machine and AI identities outnumber human users 144-to-1, according to 2026 research from the Cloud Security Alliance, and many carry permissions that haven’t been reviewed since they were granted. If BeyondTrust detects risky behavior or excessive privilege associated with a service account or AI agent, teams can use Forcepoint to revoke its access to the sensitive data at risk in one step. The account keeps doing the rest of its job.
Too many alerts, too little context. Instead of cross-checking two consoles, customers work from one Forcepoint dashboard that ranks each risky identity by the value of accessible data and shows why that identity was deemed risky. With a clear line of sight from identity and privilege risk to sensitive data, teams investigate faster, focus on critical vulnerabilities and remove or restrict access with targeted precision.
“The strongest technology alliances bring together complementary capabilities to solve problems neither side should have to solve in isolation,” said David Manks, Vice President of Global Strategic Alliances at BeyondTrust. “Forcepoint’s understanding of sensitive data and BeyondTrust’s identity and privilege intelligence provide two critical dimensions of risk. Bringing them together helps customers see where risky access creates meaningful exposure and take precise action to protect what matters.”

20 YEARS OF MEMORIES, DUBAI. AND WE’RE JUST GETTING STARTED. MAJESTIC HOTELS OFFERS EXCLUSIVE 20% ANNIVERSARY PROMO

Al Jaddaf Rotana Appoints Hekmat Amer as Complex Director of Sales & Marketing

GHA DISCOVERY launches global giveaway with D$50,000 in prizes and Lifetime Titanium Memberships


-
 Trending12 months ago
OPPO A6 Pro 5G Review: Reliable Daily Driver
-

 Tech News2 years ago
Denodo Bolsters Executive Team by Hiring Christophe Culine as its Chief Revenue Officer
-
 VAR1 year ago
Microsoft Launches New Surface Copilot+ PCs for Business
-
 Automotive2 years ago
AGMC Launches the RIDDARA RD6 High Performance Fully Electric 4×4 Pickup
-
Tech Interviews3 years ago
Navigating the Cybersecurity Landscape in Hybrid Work Environments
-

 Hospitality2 years ago
Gulfood 2025 30th Edition Kicks Off Today, Setting New Benchmarks in F&B Growth and Innovation
-

 Tech News1 year ago
Nothing Launches flagship Nothing Phone (3) and Headphone (1) in theme with the Iconic Museum of the Future in Dubai
-
 VAR2 years ago
Samsung Galaxy Z Fold6 vs Google Pixel 9 Pro Fold: Clash Of The Folding Phenoms