 Have a question? +971 56 404 0503

Tech Features
In the Crosshairs of APT Groups: A Feline Eight-Step Kill Chain

By Alexander Badaev, Information security threat researcher, Positive Technologies Expert Security Center and Yana Avezova, Senior Research Analyst, Positive Technologies
In cybersecurity, “vulnerability” typically evokes concern. One actively searches for it and patches it up to build robust defenses against potential attacks. Picture a carefully orchestrated robbery, where a group of skilled criminals thoroughly examines a building’s structure, spots vulnerabilities, and crafts a step-by-step plan to breach security and steal valuables. This analogy perfectly describes the modus operandi of cybercriminals, with the “kill chain” acting as their detailed blueprint.
In a recent study, analysts from Positive Technologies gathered information on 16 hacker groups attacking the Middle East analyzing their techniques and tactics. It is worth noting that most of the threats in Middle Eastern countries come from groups believed to be linked to Iran—groups such as APT35/Charming Kitten or APT34/Helix Kitten. Let’s see how APT groups operate, how they initiate attacks, and how they develop them toward their intended targets.
Step 1: The Genesis of Intrusion (Attack preparation)
It all begins with meticulous planning and reconnaissance. APT groups leave no stone unturned in their quest for vulnerable targets. They compile lists of public systems with known vulnerabilities and gather employee information. For instance, groups like APT35 aka Charming Kitten known for targeting mainly Saudi Arabia and Israel, gather information about employees of target organizations, including mobile phone numbers, which they leverage for nefarious purposes like sending malicious links disguised as legitimate messages. After reconnaissance, they prepare tools for attacks, such as registering fake domains and creating email or social media accounts for spear phishing. For example, APT35 registers accounts on LinkedIn and other social networks to contact victims, persuading them through messages and voice calls to open malicious links.
Step 2: The Initial Access: Gaining a Foothold
Once armed with intelligence, cybercriminals proceed to gain initial access to their target’s network. Phishing campaigns, often masquerading as legitimate emails, serve as the primary means of infiltration. An example is the Desert Falcons group, observed spreading their malware through pornographic phishing. Notably, some groups go beyond traditional email phishing, utilizing social networks and messaging platforms to lure unsuspecting victims, as seen with APT35, Bahamut, Dark Caracal, and OilRig. Moreover, techniques like the watering hole method, where attackers compromise trusted websites frequented by their targets, further highlight the sophistication of these operations. Additionally, attackers exploit vulnerabilities in resources accessible on the internet to gain access to internal infrastructure. For example, APT35 and Moses Staff exploited ProxyShell vulnerabilities on Microsoft Exchange servers.
Step 3: Establishing Persistence: The Art of Concealment
Having breached the perimeter, APT groups strive to establish a foothold within the victim’s infrastructure, ensuring prolonged access and control. This involves deploying techniques such as task scheduling, as seen in the campaign against the UAE government by the OilRig group, which created a scheduled task triggering malicious software every five minutes. Additionally, many malicious actors set up malware autostart, like the Bahamut group creating LNK files in the startup folder or Dark Caracal’s Bandook trojan. Some APT groups, such as APT33, Mustang Panda, and Stealth Falcon, establish themselves in victim infrastructures by creating subscriptions to WMI events for event-triggered execution. Furthermore, attackers exploit vulnerabilities in server applications to install malicious components like web shells, which provide a backdoor for remote access and data exfiltration.
Step 4: Unraveling the Network: Internal Reconnaissance
After breaking in, APT groups don’t just sit there. They explore the system like a thief casing a house to find valuables and escape routes. This digital reconnaissance involves several steps. First, they perform an inventory check, identifying the computer’s operating system, installed programs, and updates, like figuring out a house’s security measures. For instance, APT35 might use a simple command to see if the computer is a powerful 64-bit system, capable of handling more complex tasks. Second, they map the network layout, akin to identifying valuable items and escape routes. APT groups might use basic tools like “ipconfig” and “arp” (like Mustang Panda) to see how devices are connected and communicate. They also search for user accounts and activity levels, understanding who lives in the house (figuratively) and their routines. Malicious tools, like the Caterpillar web shell used by Volatile Cedar, can list all usernames on the system. Examining running programs is another tactic, like checking for security guards. Built-in commands like “tasklist” (used by APT15 and OilRig) can reveal a list of programs currently running.
Finally, APT groups might deploy programs that hunt for secrets hidden within files and folders, like searching for hidden safes or documents. The MuddyWater group, for example, used malware that specifically checked for directories or files containing keywords related to antivirus software. By gathering this comprehensive intel, APT groups can craft targeted attacks, steal sensitive data like financial records or personal information, or exploit vulnerabilities in the system to cause even more damage.
Step 5: Harvesting Credentials: Unlocking the Vault
Access to privileged credentials is the holy grail for cyber attackers, granting them unrestricted access to critical systems and data. One common tactic is “credential dumping,” where tools like Mimikatz (used by APT15, APT33, and others) snatch passwords directly from a system’s memory, similar to stealing a key left under a doormat. Keyloggers, used by APT35 and Bahamut for example, acts like a hidden camera, silently recording keystrokes to capture usernames and passwords as victims type them in.
These stolen credentials grant access to even more sensitive areas. APT groups also exploit weaknesses in how passwords are stored. For instance, some target the Windows Credential Manager (like stealing a notepad with written down passwords). Brute-force attacks, trying millions of combinations, can crack weak passwords. Even encrypted passwords can be vulnerable if attackers have specialized tools. By employing these tactics, APT groups bypass initial security and access sensitive information or critical systems.
Step 6: Data Extraction: The Quest for Valuable Assets
Once inside, APT groups aren’t shy about snooping around. They leverage stolen credentials to capture screenshots, record audio and video (like hidden cameras and microphones), or directly steal sensitive files and databases. For instance, the Dark Caracal group employed Bandook malware, which can capture video from webcams and audio from microphones. This stolen data becomes their loot.
To ensure a smooth getaway, APT groups often employ encryption and archiving techniques. Imagine them hiding their stolen treasure chests—the Mustang Panda group, for example, encrypted files with RC4 and compressed them with password protection before shipping them out. This makes it difficult for defenders to identify suspicious activity amongst regular network traffic.
Step 7: Communication Channels: Establishing Control
APT groups rely on hidden communication channels with command-and-control (C2) servers to control infected machines and exfiltrate data. They employ various tactics to blend in with regular network traffic. This includes using common protocols (like IRC or DNS requests disguised as legitimate web traffic) and encrypting communication for further stealth.
However, some groups take it a step further. For instance, OilRig used compromised email servers to send control messages hidden within emails and then deleted them, making their C2 channel nearly invisible. These innovative techniques make it difficult for security measures to detect malicious activity, highlighting the importance of staying informed about evolving APT tactics.
Step 8: Covering Tracks: Erasing Digital Footprints
As the operation ends, APT groups meticulously cover their tracks to evade detection and prolong their presence in the compromised environment. Techniques like file obfuscation, masquerading, and indicator removal are employed to erase digital footprints and thwart forensic investigations. For example, the Bahamut group used icons mimicking Microsoft Office files to disguise malware, and the OilRig group used .doc file extensions to make malware appear as office documents. The Moses Staff group named their StrifeWater malware calc.exe to make it look like a legitimate calculator program.
To further bypass defenses, attackers often proxy the execution of malicious commands using files signed with trusted digital certificates. The APT35 group used the rundll32.exe file to execute the MiniDump function from the comsvcs.dll system library when dumping the LSASS process memory. Meanwhile, the Dark Caracal group employed a Microsoft Compiled HTML Help file to download and execute malicious files. Many APT groups also remove signs of their activity by clearing event logs and network connection histories, and changing timestamps. For instance, APT35 deleted mailbox export requests from compromised Microsoft Exchange servers. This meticulous cleaning makes it much more difficult for cybersecurity professionals to conduct post-incident investigations, as attackers often remove their arsenal of software from compromised devices after achieving their goals.
Conclusion: A Call to Vigilance
In a nutshell, the threat landscape in the Middle East is fraught with peril, as APT groups continue to refine their tactics and techniques to evade detection and wreak havoc on unsuspecting organizations. By understanding the anatomy of cyber intrusions and remaining vigilant against emerging threats, organizations can bolster their defenses and mitigate the risks posed by these sophisticated adversaries. Together, let us remain steadfast in our commitment to safeguarding the digital frontier against cyber threats.
by Professor Hind Zantout, Programme Director, MSc Data Science, School of Mathematical and Computer Sciences, Heriot-Watt University Dubai
Women today have jobs across all sectors of the economy, and they are increasingly achieving breakthroughs as entrepreneurs, and progressing to running successful businesses in the UAE, the wider region and globally. The GEM 2025/2026 Women’s Entrepreneurship Report indicates that they represent 45% of founders of startups worldwide. Whilst this figure is promising, women still face obstacles and challenges down the line, as they face challenges in scaling their businesses. But the overall picture remains bright, from creative chocolate concepts, to beauty products to retail and cybersecurity, there are many stories of achievement and success to tell about women entrepreneurs.
The dominant theme that has been disrupting established organisations and providing opportunities for small organisations and start-ups for over 25 years has been computer and communication technology and software systems that deliver the needed functionality. The firstborn in that generation was the Internet, dramatically changing how and where buying and selling can happen, and e-commerce helped women, especially in developing countries, sell their goods.
Today this is further simplified, bypassing the need for a dedicated website that can be replaced by a much cheaper social media presence, hence the term social commerce. Traditional AI has been around for a very long time, but in that generation, it matured into a reliable technology capable of leveraging huge amounts of data. One example is using customer data to predict when an aeroplane engine is about to fail, so it can be serviced before the failure occurs, reducing the cost of time and money for maintenance. Models can also predict customer churn, for example in a telecom subscription environment, so companies can take action to prevent it. The Internet itself evolved into a huge and valuable source of information which then got exploited using large language models to deliver generative artificial intelligence (AI) again causing further disruption but opportunities as well.
Technology advances also facilitated innovations that impacted the monetary system for payments, with fintech and cryptocurrencies. So, the scene is one of increased complexity, evolving opportunities and challenges that need to be addressed. Looking at students enrolled in STEM programs for the region, female students have had a healthy participation for many years now, especially in computer science programs. Courses there often include data science and artificial intelligence, so when the next generation of entrepreneurs is considered that have a university degree, there is no shortage of women with strong relevant skills which are essential for an entrepreneur to appreciate the capabilities of technology but also the pitfalls.
For many businesses, the customer experience is an essential part of the business model and ensuring a positive one is critical. Up until recently, human agents, often supported by computer systems, were typically in charge of ensuring customer satisfaction that leads to customer loyalty. With recent technological advances such as generative AI, chatbots have seen a dramatic transformation in their ability, and they can now hold almost human-like conversations with the customer, but these still remain restricted to limited scenarios. Their implementation in customer-facing processes is not completely risk free and could lead to a frustrated customer who cannot have a query responded to or their problem resolved. An expanding landscape of technologies now features AI agents and the promise of offering the needed additional capability. And with such an accelerated pace of change, with the potential to continually proliferate and transform many business processes, it is essential that business leaders not only to have an understanding of what can be delivered, but also the risks that need to be mitigated.
Traditional customer relationship management puts the emphasis on tracking the customer lifecycle from marketing to sales through to customer service. But in an ecosystem offering a diversity of channels that a customer can engage with, it is essential to manage the whole customer experience (CX), tracking and measuring all interactions, not just the purchase of a product or service. For example, virtual fitting rooms are built on augmented reality / virtual reality platforms and can be one channel in retail, where the customer can superimpose the image of a piece of clothing over an image of themselves before making the purchase decision. A customer can also see how a sofa they are considering would appear in their living room. Such a personalised shopping experience can be valuable, as studies show a reduction in returns, around 25% – 40%. There is, however, a real danger that hyper-personalisation, where every interaction is logged, analysed and exploited, will lead to the customer feeling under surveillance.
For example, using a customer’s browsing history to make recommendations and offers will spook many, with the realisation that every online click was tracked. This sets off the so-called creep factor and customers then abruptly switch away from that product or service. A fine balance needs to be struck to bridge the personalisation-privacy paradox, not just to keep customers loyal, but also to avoid litigation. In the US, Neutrogena and Charlotte Tilbury faced separate class actions that were settled with a payout. The allegations were that the tools used processed user data that may include biometric data.
And any deployment of AI will have to give careful consideration to the risk of bias in the algorithms. As a result of using biased training data, some groups may be over-represented while other groups may be under-represented, leading to unfair treatment of customers. The impact can be wide-ranging, from missed revenue to developing flawed marketing strategies, to customers losing trust in a product or service.
There is something almost ironic here. A company that helped persuade the world AI could reduce dependence on human judgment now faces one of its biggest uncertainties because of one human being.

By: Srijith KN, Technology Integrator
On November 12, Nvidia announced that Jensen Huang had resigned as CEO and director, with CFO Colette Kress assuming the role on an interim basis. His departure followed reports involving personal relationships and possible national security concerns. Allegations of foreign intelligence connections remain unproven. In a statement on November 8, Nvidia’s board said it had no reason to believe company secrets or national security were compromised and had initiated an independent investigation.
But the bigger story is what happens to the AI empire he built.
At a recent infrastructure conference in Croatia, an Nvidia executive jokingly introduced himself as the cheaper alternative to “my boss Jensen,” adding that he only needed the leather jacket. A funny remark, but also revealing. Huang had become more than a CEO. He was the personality behind Nvidia’s extraordinary rise.
Five issues now deserve attention.
Governance. Huang led Nvidia for 33 years as strategist, dealmaker and chief evangelist. Investors understood the value of Nvidia’s technology. What remains uncertain is how much of that value depended on the vision, relationships and influence of one individual. The question now is whether Nvidia has built the institutional strength to carry that legacy forward.
Strategy. Huang’s ambition extended far beyond GPUs. His five-layer AI framework, encompassing energy, chips, infrastructure, models and applications, envisioned an entire computing economy. The opportunity was never simply about selling processors. It was about shaping the foundations upon which the next generation of technology would operate. That vision now needs leadership capable of carrying it forward.
AI sovereignty. Perhaps Huang’s most consequential message was directed at governments. According to the Nvidia executive in Croatia, Huang routinely asks presidents and prime ministers whether their countries want to become AI “takers” or AI “makers.”
Every nation will consume AI. But those developing their own infrastructure, models and capabilities could exercise greater control over their digital futures. The executive described Huang’s support for open architectures, deployable under national laws and data requirements, as making this a geopolitical conversation, not merely a technology discussion.
Geopolitics. Huang advocated maintaining access to the Chinese market for advanced chips. His departure removes an influential voice from that debate, amid continued scrutiny of chip exports.
Economics. Nvidia’s investments in AI companies that also purchase its computing infrastructure have added another dimension to the debate over AI economics. The real question is whether the revenues generated across this ecosystem can ultimately justify the extraordinary capital flowing into it.
None of this means Nvidia’s technology advantage has disappeared. Its engineering talent, software ecosystem and customer relationships remain formidable. The board has also expressed confidence that its leadership team can continue executing the company’s technology roadmap without interruption.
But perhaps the AI industry is entering a different chapter, where governance matters more than charisma and profitability matters more than promises.
For enterprises, the lesson is simple. Never build an AI strategy around one vendor, one chip or one personality.
Technology is only as strong as the judgment guiding it.
The real test now is whether Nvidia can demonstrate that its future is bigger than the man who built it.
BY SRIJITH KN & SUBRATO BASU

As AI spending rises and experimentation gives way to accountability, the real challenge for business leaders is no longer access to technology, but proving value, controlling cost and redesigning how organisations work.
Every year, the technology industry promises a breakthrough that will change everything. New models arrive, computing capacity expands and investment reaches new highs. Then, somewhere between the product demonstration and the quarterly earnings call, someone asks the question that matters most:
What did all of this actually improve?
That question came into sharper focus in 2026.
Artificial intelligence moved deeper into everyday business. Companies deployed assistants, experimented with agents and embedded AI across customer service, software development, compliance, finance and operations.
Yet adoption turned out to be the easy part.
Installing an AI assistant is relatively straightforward. Redesigning an organisation around it is not.
Fragmented systems, poor-quality data, unclear ownership, weak governance and sceptical employees do not disappear because a company has purchased another software licence.
Businesses do not need another year of impressive demonstrations. They need to know whether AI is helping them make better decisions, serve customers more effectively and run their operations more reliably.
That shift is turning AI from primarily a technology question into a management one.
From experimentation to accountability
The adoption numbers appear impressive.
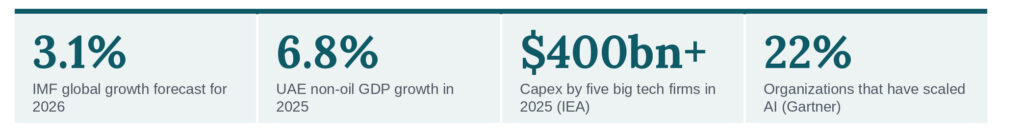
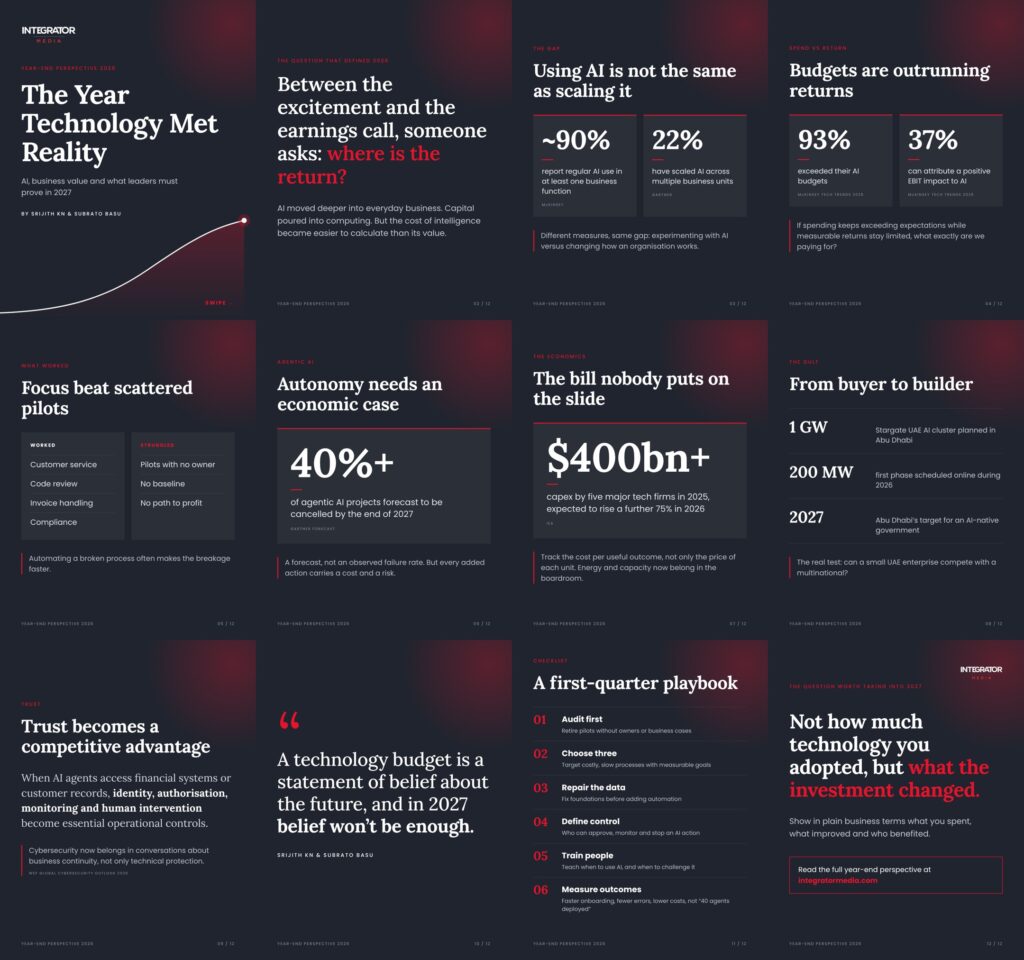
McKinsey found that nearly nine in ten survey respondents reported regular organisational use of AI in at least one business function. Gartner, using a different measure, found that only 22% of organisations had successfully scaled AI across multiple business units or adopted an AI-first approach.
The methodologies are different, but together they point to an important distinction: using AI is not the same as changing how a business operates.
The economics reinforce that concern.
In McKinsey’s Technology Trends Outlook 2026, one survey found that 93% of respondents had exceeded their AI budgets. Another found that only 37% of companies could attribute a positive EBIT impact to their AI programmes.
Those numbers create an uncomfortable boardroom question.
If spending continues to exceed expectations while measurable returns remain limited, what exactly are organisations paying for?
The clearest returns are likely to emerge where companies begin with a defined business problem: reducing customer-service resolution time, accelerating code review, simplifying invoice handling or strengthening compliance.
What becomes harder to justify is the proliferation of pilots with no accountable owner, no performance baseline and no clear route to economic value.
Automating a broken process can simply make the breakage happen faster.
Agentic AI raises the stakes
Agentic AI made this management challenge more significant in 2026.
Traditional generative AI largely responded to requests. Agents can increasingly perform multistep activities, interact with systems and execute actions.
That creates more opportunity, but it also introduces more cost, operational risk and responsibility.
Gartner has forecast that more than 40% of agentic AI projects will be cancelled by the end of 2027 because of escalating costs, unclear business value and inadequate risk controls.
It is a forecast rather than an observed failure rate, but the warning matters.
Giving software more autonomy only increases the need for organisations to define who owns the outcome, who monitors the process and who can intervene when something goes wrong.
The question for leaders is therefore becoming less about what an AI agent can do and more about what the organisation should allow it to do.
The economics nobody puts on the slide
AI is also forcing companies to think differently about technology costs.
The International Energy Agency reported that capital expenditure by five major technology companies exceeded $400 billion in 2025 and was expected to rise by another 75% in 2026.
The physical foundations of AI require enormous amounts of computing infrastructure, electricity, cooling, networking, land, semiconductors and highly specialised talent.
An individual AI task may become cheaper while the total technology bill continues to grow simply because usage expands.
That is not necessarily a problem if the additional activity creates measurable value.
But somebody needs to be able to explain what the extra expenditure produced.
Did it generate more revenue?
Did customers receive better service?
Did employees become more productive?
Did the organisation reduce risk?
Technology and finance leaders increasingly need to measure the cost per useful outcome, rather than concentrating only on the price of individual models, tokens or software licences.
Energy, computing capacity and infrastructure resilience now belong in the same boardroom conversation as digital transformation.
AI also creates a wider economic question
There is another issue that sits beyond corporate productivity.
A business may be able to reduce certain labour requirements through automation, but an economy still depends on people earning, consuming, creating businesses and paying taxes.
If productivity gains do not translate into new industries, new forms of employment or greater economic opportunity, the benefits become harder to sustain.
Reskilling cannot therefore be treated simply as a corporate social-responsibility programme.
It increasingly belongs at the centre of technology strategy.
The real measure of intelligent technology should not be how many jobs it eliminates or how many tasks it completes. It should be whether it creates durable value for enterprises while expanding economic opportunity around them.
The Gulf moves from technology buyer to builder
This is particularly relevant in the Gulf.
For years, the region was often described primarily as a major buyer of global technology. That description increasingly feels incomplete.
Across the UAE, Saudi Arabia and the wider Gulf, governments and businesses are investing in AI infrastructure, cloud capacity, digital government, data centres and technology ecosystems.
Stargate UAE, the planned one-gigawatt AI infrastructure cluster in Abu Dhabi, illustrates the scale of that ambition. Its first 200 megawatts were scheduled to come online during 2026.
Abu Dhabi’s ambition to build an AI-native government by 2027 and Dubai’s support for digital entrepreneurship point in the same direction.
But infrastructure alone does not create prosperity.
The more important question is whether that infrastructure lowers the cost of innovation and makes advanced technology accessible to the companies that drive the region’s everyday economy.
Can a UAE SME use AI to compete more effectively with a multinational?
Can a local healthcare provider deploy specialised intelligence without building an enormous internal technology operation?
Can a logistics company use automation to improve reliability rather than simply add another layer of software?
The Gulf has invested heavily in technological ambition. The next chapter will be about making that ambition useful.
That means moving from importing technology to developing capabilities, intellectual property, businesses and talent around it.
Innovation moves into the physical world
The technology conversation is also becoming broader than generative AI.
Physical AI is bringing intelligence into robotics, logistics, manufacturing, healthcare and mobility.
Digital twins, edge computing and intelligent energy systems are connecting digital decisions to physical operations. Smaller, specialised AI models may also offer better economics and governance than enormous general-purpose systems for narrowly defined industry tasks.
Quantum computing continues to advance, although business leaders should remain cautious about claims of immediate universal commercial impact.
The more urgent issue for many organisations is post-quantum cybersecurity.
Confidential information protected today could potentially become vulnerable as computing capabilities evolve, meaning organisations handling long-lived sensitive data need to begin thinking about cryptographic resilience well before large-scale quantum computing arrives.
Across these technologies, the competitive advantage is unlikely to come from collecting the greatest number of tools.
It will come from integrating the right technologies into an operation that works.
Trust becomes part of the business model
As AI systems gain access to more sensitive information and perform more consequential activities, cybersecurity becomes inseparable from business strategy.
The World Economic Forum’s Global Cybersecurity Outlook 2026 described an environment shaped by AI-enabled threats, geopolitical fragmentation and uneven cyber resilience.
AI agents interacting with financial systems, customer information or operational infrastructure raise the importance of identity controls, authorisation, monitoring and human intervention.
Cybersecurity can therefore no longer be treated simply as the responsibility of the security department.
It is increasingly about business continuity, reputation and customer trust.
The companies that can demonstrate that intelligent systems are secure, explainable and accountable may find that trust becomes a genuine competitive advantage.
2027: the numbers will have to add up
If 2026 was the year organisations experimented with how far AI could go, 2027 is likely to bring much tougher questions about whether those investments make economic sense.
A good demonstration will matter less than what a company can responsibly allow a system to do.
Agents will begin taking responsibility for defined activities, but each will require boundaries, monitoring and a human being who ultimately owns the consequences.
Boardroom conversations should shift from:
- How many AI tools have we deployed?
- to:
- What does this process cost now?
- How much faster is it?
- Has the error rate fallen?
- Are customers noticing the difference?
That scrutiny will extend beneath the software layer.
Energy availability, sovereign computing capacity, regulatory requirements and infrastructure resilience will increasingly influence where companies choose to invest.
The same scrutiny will reach the workforce.
Employees will need technical fluency, but they will also need business judgement: the ability to understand exceptions, question automated recommendations and take responsibility when systems get something wrong.
Access to another AI model will not be the defining advantage.
An organisation that operates better — at a cost that survives examination — will be.
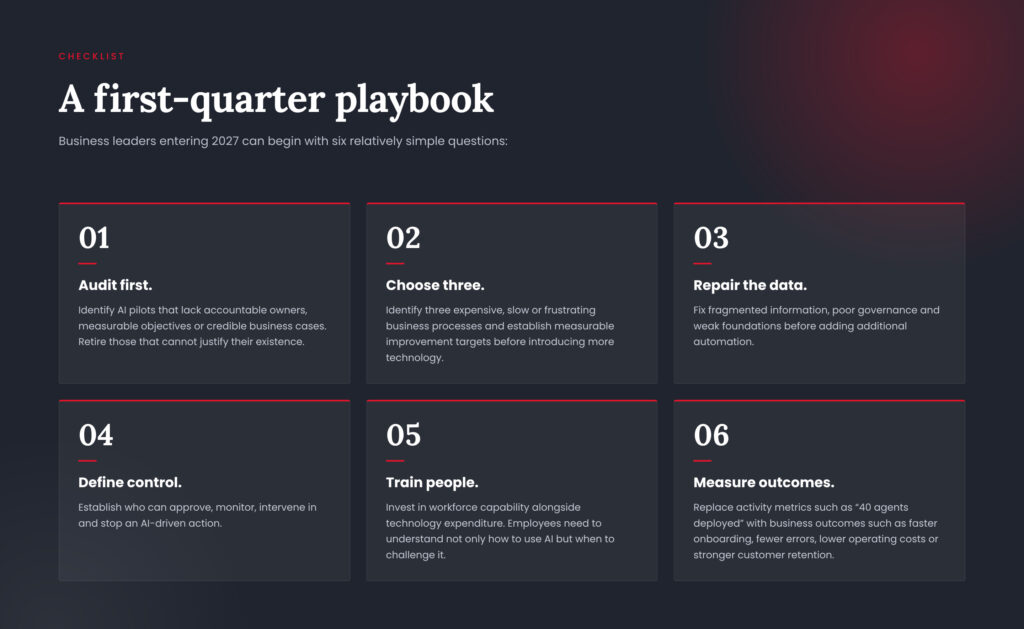
The question worth taking into 2027
As 2026 closes, business leaders should temporarily set aside the question of how much technology their organisations have adopted.
Instead, ask what the investment actually changed.
Did serving a customer become simpler?
Did an expensive process become more efficient without becoming less reliable?
Did employees gain the ability to spend more time on valuable work?
Can the improvement be seen in the numbers?
A technology budget is ultimately a statement of belief about the future.
In 2027, belief will not be enough.
AI adoption alone will no longer be impressive. The organisations that stand out will be those that can explain, in plain business terms, what they spent, what improved and who benefited.
And that may be the clearest indication yet that AI is becoming less of a technology problem — and much more of a management one.
Subrato Basu is an author, adviser and speaker on AI strategy and technology cost management. With nearly three decades of experience advising C-suite leaders, he helps organisations across North America, Asia Pacific and the Middle East turn technology investment into measurable business value.
Srijith KN is Senior Editor at Integrator Media, who is hands-on in covering enterprise technology, artificial intelligence, cybersecurity and the digital economy across the Middle East.
Bijou Patisserie Unveils a New Afternoon Tea Inspired by Travel and Precious Discovery
Time to Switch Off: Ways to Spend the Eid Al Etihad Break
Things to Do During the Eid Al Etihad Long Weekend in Dubai

OPPO A6 Pro 5G Review: Reliable Daily Driver

Denodo Bolsters Executive Team by Hiring Christophe Culine as its Chief Revenue Officer

Microsoft Launches New Surface Copilot+ PCs for Business

2026 in Review: Is AI Becoming More of a Management Problem Than a Technology Problem?

Inside XPENG Brand Night: AI Mobility Lands Centre Stage in Dubai

Chinese Cars Are Reshaping the GCC Market, but Resale Value Could Be the Next Battleground
-
 Trending1 year ago
OPPO A6 Pro 5G Review: Reliable Daily Driver
-
 Tech News2 years ago
Denodo Bolsters Executive Team by Hiring Christophe Culine as its Chief Revenue Officer
-
VAR2 years ago
Microsoft Launches New Surface Copilot+ PCs for Business
-
 Automotive2 years ago
AGMC Launches the RIDDARA RD6 High Performance Fully Electric 4×4 Pickup
-
 VAR11 months ago
Huawei Nova 14 Pro Review: Where Camera Excellence Meets Ecosystem Evolution
-
Tech Interviews3 years ago
Navigating the Cybersecurity Landscape in Hybrid Work Environments
-

 Hospitality2 years ago
Gulfood 2025 30th Edition Kicks Off Today, Setting New Benchmarks in F&B Growth and Innovation
-
News4 years ago
BenQ ZOWIE : First TN 360Hz DyAc+ Gaming Monitor