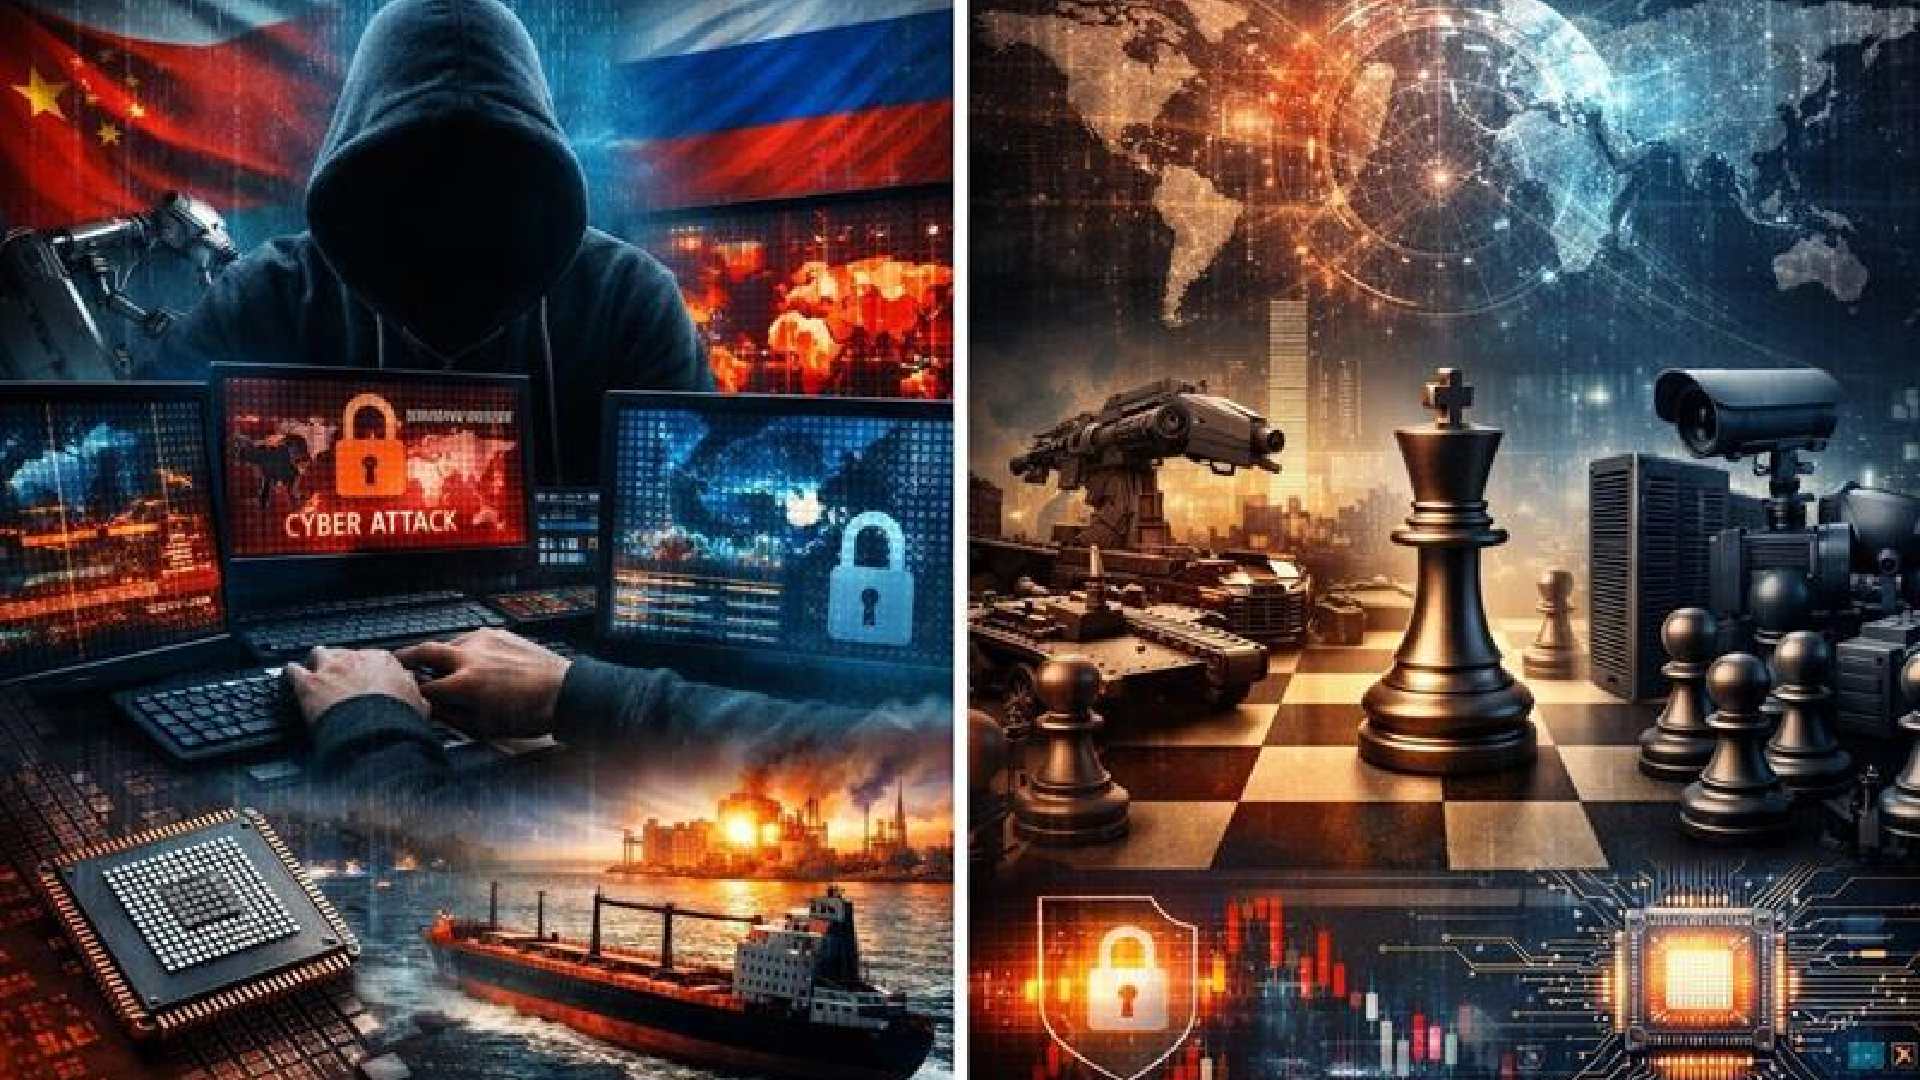
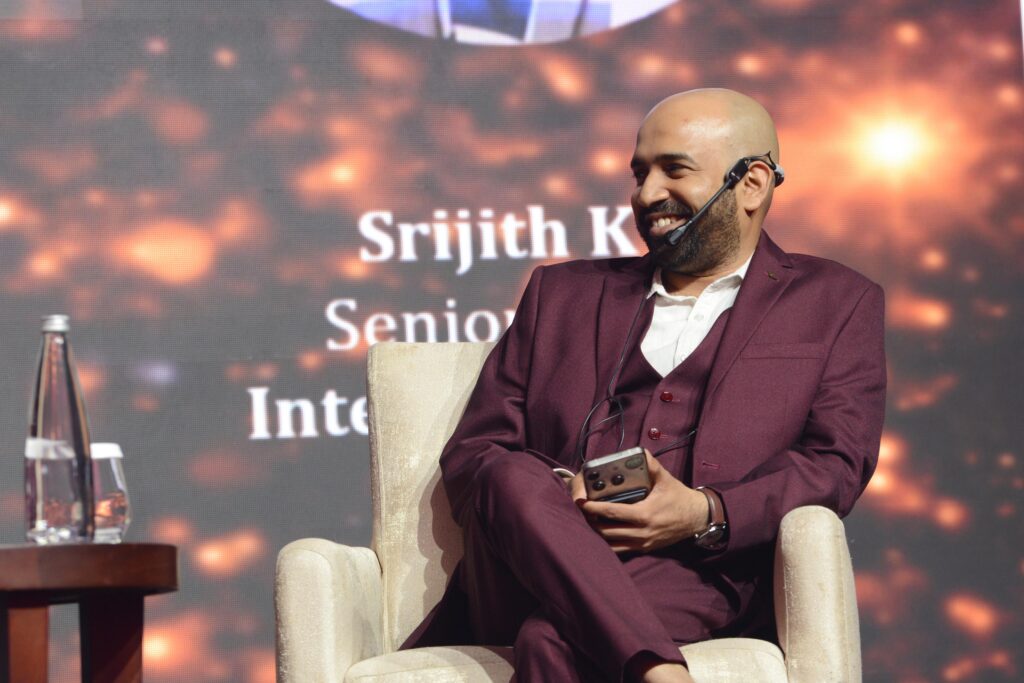
When did you last see geopolitical risk appear as a named line item in your technology governance framework?” This question — posed by Subrato Basu to technology leaders across industries and geographies, and echoed in the conversations Srijith KN has tracked across the CXO community — increasingly divides its audience into two groups. The gap between them is widening, and it reveals a deeper shift: geopolitics is no longer external to technology strategy. It is now one of its defining forces.
The first group — still the majority — treats geopolitical risk as someone else’s problem. It belongs, they assume, to risk officers, government affairs teams, or the audit committee. Technology is their domain; geopolitics is noise in the background. The second group has understood something that the first has not: the boundary between geopolitical risk and technology risk no longer meaningfully exists.
This article is written for both. For the first group, it is a wake-up call — offered in the hope that it arrives before an incident makes the argument more forcibly. For the second, it is an attempt to sharpen a framework and ground it in the operational realities that boards and CXOs are navigating right now. The central argument is this: geopolitical volatility has become a direct, structural input into enterprise technology strategy. Organizations that govern for it with the rigor applied to financial or regulatory risk will be measurably more resilient, more competitive, and more trusted than those that do not.
“Geopolitical volatility is no longer background noise for technology leaders. It is a direct input variable into technology strategy, and the boards that do not govern for it are operating with a critical blind spot.“
The Assumption That Built Our Governance Frameworks Is Broken
For most of the past two decades, a workable assumption underpinned how organisations sourced, deployed, and governed technology: that the global technology ecosystem was broadly open, commercially-driven, and largely apolitical. Hardware vendors competed on specification. Cloud providers competed on price and performance. Procurement teams evaluated suppliers on technical merit. Geopolitical considerations were, at most, a due diligence footnote.
That assumption has been systematically dismantled. The deliberate weaponisation of technology — through trade restrictions, regulatory controls extended beyond national borders, state-sponsored cyber operations, and the calculated use of supply chain access as an instrument of strategic leverage — has fundamentally altered the risk calculus for any enterprise that depends on globally sourced technology infrastructure. What was once a commercially neutral procurement decision is now, in many cases, a geopolitical exposure.
This is not a temporary disruption that will normalise once a particular set of tensions eases. It reflects a durable structural shift in how major powers compete, and in how that competition is increasingly waged through, and against, the technology layer of the global economy. For enterprises operating in markets defined by proximity to active geopolitical fault lines — whether those fault lines are geographic, commercial, or digital — the consequences are not theoretical. They are already reaching enterprise cloud contracts, hardware procurement pipelines, and security operations. From our respective vantage points — practitioner and editorial — the pattern is unambiguous.
“What was once a commercially neutral procurement decision is now, in many cases, a geopolitical exposure. Governance frameworks designed for a different era are systematically unfit for this one.“
Five Fault Lines Running Through the Enterprise Technology Stack
When we map the pathways through which geopolitical volatility translates into technology operational risk, five pressure points emerge with consistency across sectors and geographies. We offer them not as a comprehensive risk register — every organisation’s exposure profile will differ by market, sector, and architecture — but as a diagnostic lens for board and CXO discussion.
a) The Cloud Compliance Trap
The hyperscalers that power the majority of enterprise digital infrastructure operate under regulatory frameworks whose reach extends well beyond their home jurisdictions. Technology access controls and compliance obligations do not stop at national borders. Enterprises with commercial relationships, supply chain connections, or infrastructure footprints that intersect with restricted or conflict-adjacent jurisdictions can find themselves subject to service reviews, contract amendments, or capability restrictions — sometimes with limited notice, and often as a downstream consequence of their vendor’s own compliance posture rather than anything the enterprise has done directly.
The trap is that this exposure is rarely visible until it activates. It can emerge through indirect supply chain adjacency, shared infrastructure configurations, or compliance flags several steps removed from the enterprise’s own operations. CIOs who have mapped their cloud footprint against potential regulatory jurisdiction risk — proactively, not reactively — hold a material governance advantage. Understanding which workloads reside on infrastructure subject to extended regulatory reach is not optional hygiene. It is foundational governance.
b) The Cyber Threat Multiplier
A consistent and well-documented pattern has been established across multiple cycles of geopolitical escalation, recorded in threat intelligence reports published by recognised international cybersecurity research organisations and government security agencies: periods of elevated inter-state tension correlate with increased state-linked cyber activity targeting financial institutions, critical infrastructure, and government-adjacent enterprises in proximate markets. This is not the authors’ independent assertion. It is an observable, documented, and reproducible pattern in the publicly available record.
The structural implication for technology leaders is clear: the cyber threat environment in markets proximate to active geopolitical fault lines is durably more elevated than in geopolitically stable ones, and that elevation intensifies when political temperature rises. The attack surface has expanded materially through the convergence of information and operational technology, the proliferation of AI-integrated workflows, and the broad adoption of connected devices. CISOs who construct their security posture reactively, in response to incidents rather than in anticipation of structural threat conditions, have fundamentally misread the governance mandate their environment demands.
c) The Supply Chain Blind Spot
Most enterprises maintain reasonable visibility into their software supply chains. Very few have equivalent clarity on the geopolitical exposure embedded in their hardware supply chains. Semiconductors, networking equipment, and industrial technology components originate from supply chains subject to trade restrictions and regulatory controls that can translate, under escalatory conditions, into sudden procurement constraints, extended lead times, or mandatory certification requirements creating material operational bottlenecks.
The organizations most exposed are those in active digital transformation or major infrastructure refresh cycles that have never stress-tested their procurement pipeline against a scenario in which specific hardware categories become unexpectedly constrained. The board-level question is not whether this will happen. It is whether, if it did, the organization would have ninety days of operational runway or ninety hours.
d)The Vendor Dependency Risk
Multi-year enterprise software commitments — ERP platforms, data infrastructure, security tooling, AI platforms — are made on the assumption of uninterrupted service from vendors operating in predictable regulatory environments. The regulatory obligations carried by enterprise software vendors headquartered across major technology jurisdictions can, under specific and not implausible circumstances, translate into licence amendments, capability restrictions, or service reviews with limited contractual notice. This risk is amplified, and actively expanding, for software incorporating AI capabilities as those capabilities attract increasing regulatory attention across multiple jurisdictions simultaneously.
Boards approving these investments are, in our view, frequently not receiving the full picture of vendor jurisdiction exposure. Requiring legal and technology leadership to jointly assess this exposure before committing to multi-year agreements is not procedural excess. In the current environment, it is a core fiduciary responsibility.
e) The Talent Dimension
The talent dimension of geopolitical risk is consistently the least visible and the most underestimated. Technology-intensive organisations in dynamic markets draw on internationally mobile specialist talent pools. Sustained geopolitical instability affects those pools in ways that are difficult to predict and slow to reverse: senior professionals reconsider relocation decisions, acquisition pipelines for specialist roles — particularly cybersecurity engineering, AI architecture, and regulatory compliance — tighten, and workforce continuity in critical functions comes under pressure at precisely the moment when those functions matter most.
Resilience against this risk requires proactive investment in local talent pipelines, structured knowledge transfer protocols for critical technology functions, and a workforce continuity discipline that treats geopolitical scenarios as first-class planning variables — not as footnotes in the HR risk register.
“The technologies most exposed to geopolitical disruption are simultaneously the most powerful instruments available to build resilience against it.“
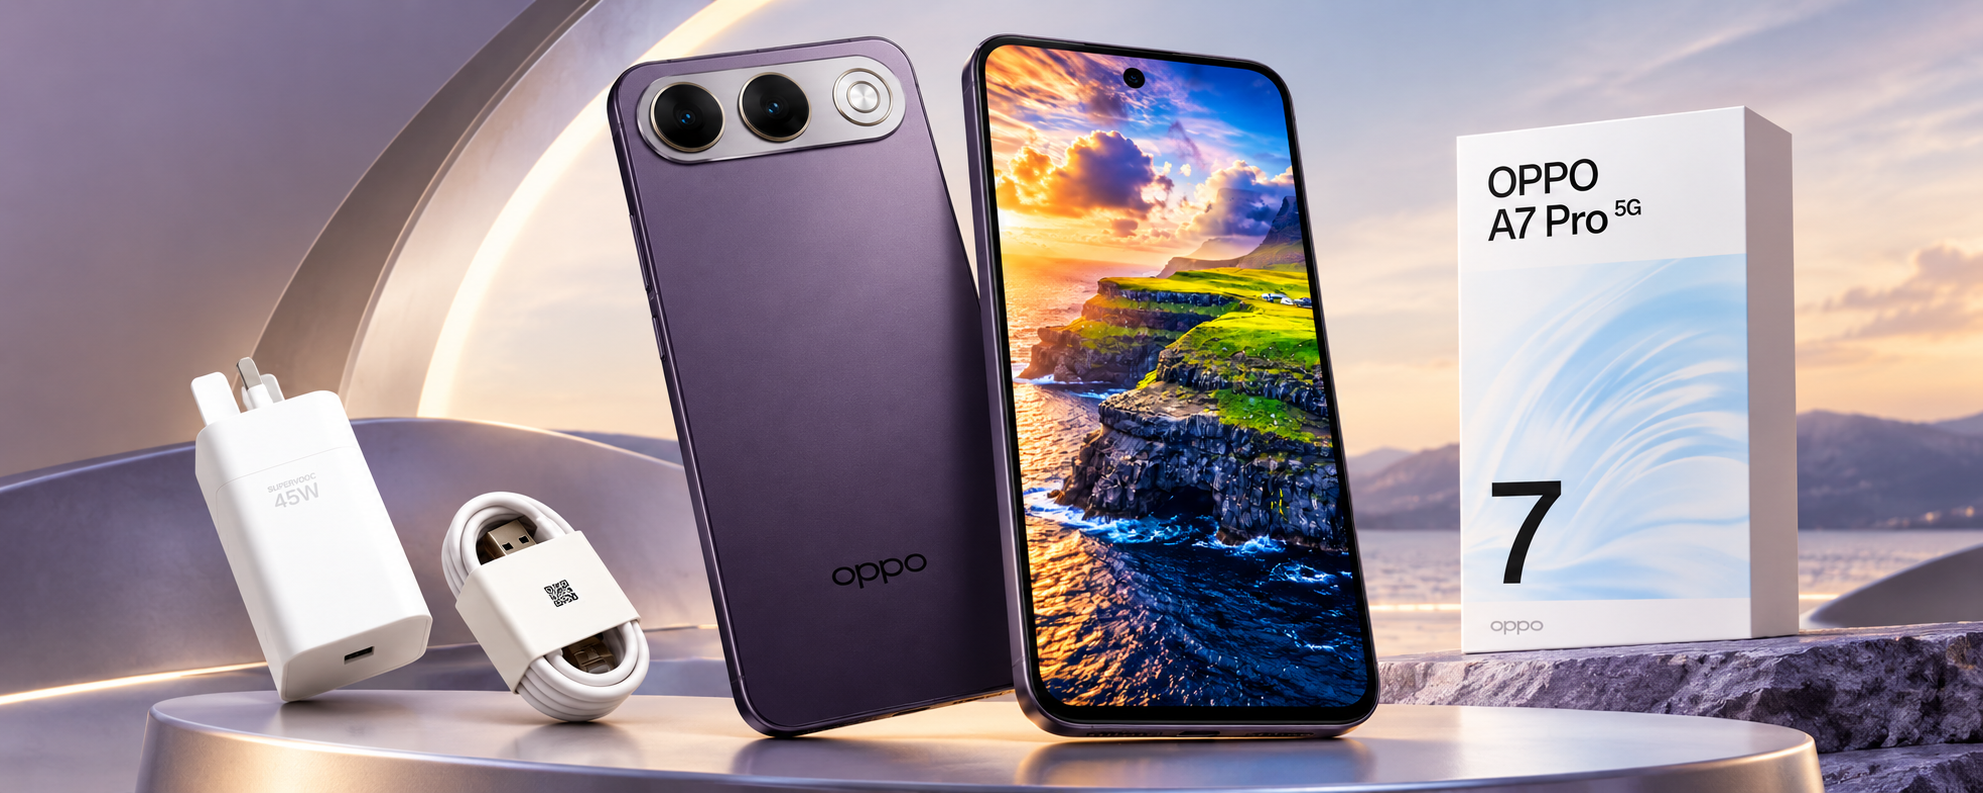
OPPO A7 Pro 5G puts longevity at the centre of the smartphone experience!
With an 8,000mAh battery, dual 50MP cameras, IP69K protection and a five-year smoothness promise, OPPO’s latest A Series smartphone makes a strong case for devices designed around longer-term ownership.
Smartphone launches have traditionally revolved around faster processors, increasingly sophisticated cameras and, more recently, AI. With the A7 Pro 5G, OPPO is putting another consideration firmly into the conversation: how well a smartphone can hold up over time.
At the centre of that proposition is an enormous 8,000mAh battery. Large-capacity batteries are becoming increasingly common, but what is interesting about the A7 Pro 5G is how little the battery dictates the physical character of the phone.
Despite the capacity, the device does not immediately look or feel like a rugged smartphone. The Shine Titanium review unit has an understated finish, while the alternative Surfing Blue introduces a more distinctive Dynamic 3D Wave Texture.
That relatively conventional appearance hides some serious durability credentials.
Built for longer ownership
The A7 Pro 5G carries IP69K dust and water resistance alongside military-grade shock resistance. Rainstorm Touch is designed to keep the display responsive even when used in heavy rain.
The longevity argument extends to the battery itself. OPPO says it can retain more than 80% of its rated capacity after 2,000 complete charging cycles, underpinning the company’s six-year battery durability proposition.
This matters because battery degradation remains one of the most noticeable compromises as smartphones age. Increasing capacity solves part of that equation; maintaining useful capacity several years into ownership potentially solves another.
Reverse wired charging also allows the A7 Pro 5G to supply power to another connected device, adding some practical value to that substantial battery reserve.
Selfies get the 50MP treatment
OPPO has also placed considerable emphasis on the front-facing camera.
The 50MP Ultra-Wide AI Zoom Selfie Camera offers a 100-degree field of view and can automatically move between 1x and 0.6x framing when additional people enter the shot.
It is a useful approach for group photographs, travel and increasingly video-led social content, where a wider front camera can make considerably more sense than simply increasing resolution. Ultra-steady video has also been included to improve handheld recording.
At the rear is another 50MP camera, using a larger 1/2-inch sensor that OPPO says captures 70% more light than its predecessor.
AI Portrait Glow, AI Popout and AI Remix Collage bring the increasingly familiar layer of computational editing into the camera experience, allowing users to manipulate images without moving immediately to third-party applications.
Five years of smoothness?
Underneath, the A7 Pro 5G is powered by the MediaTek Dimensity 6360 MAX, accompanied by OPPO’s NetworkBoost Chip S1 and AI LinkBoost 4.0.
A 4,300mm² Glacier VC Vapor Chamber handles cooling, while software-based resource and memory management is designed to maintain responsiveness as workloads increase.
Perhaps more interesting than outright performance figures is OPPO’s 5-Year Smoothness Protection. The company says the device has passed its five-year smoothness testing, reflecting a wider attempt to position performance around consistency rather than simply launch-day speed.
Naturally, five-year performance cannot be established during a conventional review period, but the emphasis itself is notable. Smartphone replacement cycles are lengthening, making sustained performance, battery health and software optimisation increasingly relevant purchasing considerations.
AMOLED keeps the experience contemporary
The front houses a 6.57-inch FHD+ AMOLED display with a 120Hz refresh rate, up to 1,400 nits of brightness and a 92.8% screen-to-body ratio.
The combination provides the fluid scrolling and vibrant presentation expected from a contemporary AMOLED smartphone, while complementing a device otherwise heavily focused on practical considerations.
Warranty coverage also extends across the GCC, Pakistan, India and Bangladesh, potentially useful for users who regularly travel between these markets.
The 8,000mAh battery will inevitably attract most of the initial attention, but the A7 Pro 5G becomes more interesting when viewed as a complete package. OPPO is combining battery capacity with physical durability, thermal management, connectivity enhancements and longer-term performance optimisation. At the same time, it has avoided turning the device into something that visually resembles a specialist rugged phone.
BY: SRIJITH KN
A different definition of smartphone performance that may ultimately be the A7 Pro 5G’s more relevant proposition. Rather than asking how much faster a smartphone can become every year, OPPO is increasingly asking another question: how much longer can it remain useful?
Nearly every enterprise believes its AI agents are properly scoped. Only a third have actually made sure of it.
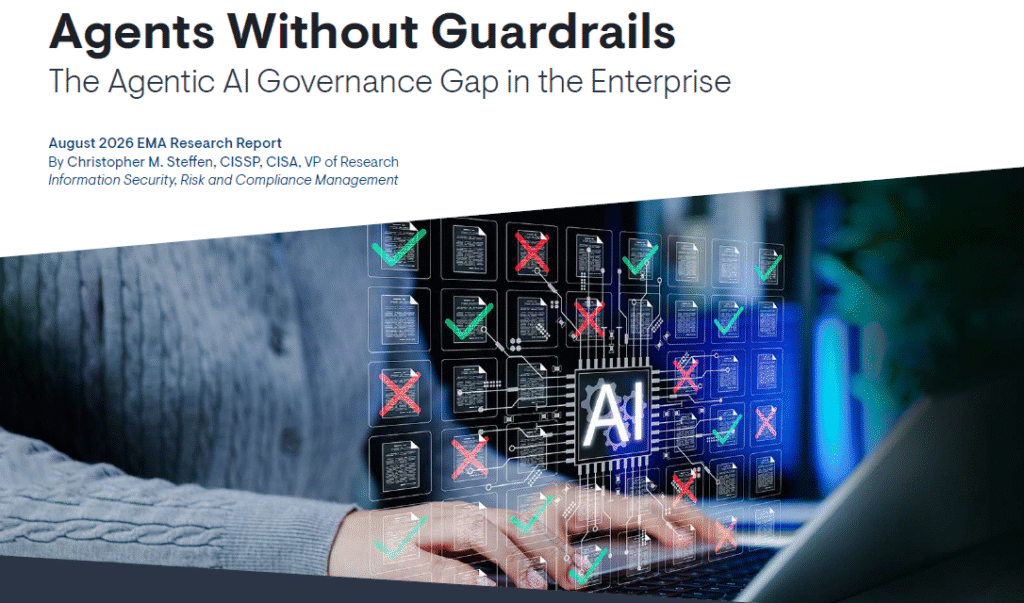
Today, new research from Cequence Security, the leader in application, API, and agentic AI protection, and Enterprise Management Associates (EMA) found that 94% of enterprise IT and security leaders are confident their AI agents do not have more access than they need, yet only 33% actually provision agents with least-privilege access. The remaining two-thirds run on broad standing permissions that are reviewed periodically, rarely reviewed, or never reviewed at all.
That gap between confidence and practice is already showing up in production, not a theoretical risk, but as incidents enterprises are living with right now. Among the organizations surveyed:
65% have experienced an AI agent take an action outside its intended scope, including 29% with measurable business impact, including data exposure, financial loss, operational disruption, or reputational damage. Another 36% caught a near-miss before it caused damage.
Only 32% can detect and contain an out-of-scope agent action within minutes through automated means; 55% need hours and manual steps to respond.
In approximately 4% of organizations surveyed, the first sign of trouble came from a customer or outside partner, not an internal system.
The findings point to one clear story. Governance has not kept pace with the speed of agentic AI deployment, and that gap is showing up at every stage of the agent lifecycle, from how agents are provisioned, to how their actions are authorized, to how they are decommissioned once a pilot ends. Other key findings from the report include:
Enterprises Have Moved Past the Pilot Stage
The scale of deployment makes the gap more urgent. 46% of organizations report they are already scaling agentic AI across multiple departments and production workflows, and 79% are running generative and agentic AI simultaneously. Further, more than 92% report an increase in AI and bot-driven traffic targeting customer-facing applications and APIs.
Authorization is Checked at the Wrong Time, Or Not At All
That governance gap extends to how access is enforced in the moment an agent acts. Only 34% of organizations evaluate an AI agent’s authorization at the moment it attempts a specific action. The majority rely on periodic policy reviews or standing permissions set once at provisioning and never revisited, meaning an agent’s access can quietly outlive the task it was originally granted for, and keep working long after anyone signed off on it.
Abandoned Pilots Are Leaving Live Credentials Behind
Additionally, there’s an increasing risk in how enterprises manage agents that don’t make it to production. 31% of agentic AI pilots have been paused indefinitely, discontinued, or abandoned. Many were real deployments with real system access and credentials that were never cleaned up. Every abandoned pilot with live credentials is exposure nobody is actively watching.
External Connectivity Carries the Same Risk
14% of organizations allow AI agents to connect to outside tools and data sources via the Model Context Protocol (MCP) without restriction. Among the majority who do limit those connections to an approved list, fewer than half, just 49%, have a dedicated team actively maintaining and auditing that list on a regular basis.
Christopher M. Steffen, CISSP, CISA, VP of Research at EMA, said: “This research shows enterprises have moved well past experimentation with agentic AI right into production, and governance has not kept pace with that shift. The gap isn’t a lack of awareness; most organizations have policies in place and express real confidence in them. The gap is between what’s written down and what’s enforced when an agent takes an action nobody approved. That disconnect shows up most clearly in how organizations authorize agent actions and monitor them once they’re live, and it’s the reason incidents are happening at a rate the industry hasn’t fully reckoned with.”
Shreyans Mehta, Co-founder and CTO at Cequence, said: “The number that jumped out to me is the 92% being confident in their governance frameworks. Confidence like that is a trap; it’s exactly why organizations stop looking for problems, stop investing in monitoring, and let authorization checks lapse until an incident forces the conversation. This is the exact blind spot Cequence is built to close, giving security teams real-time visibility into what AI agents are actually doing and enforcing authorization at the moment an agent acts, not after the fact.”
Dhruva will adopt the Ryan brand across the UAE and Saudi Arabia by the end of 2026, uniting the practice with Ryan’s global identity and international platform.
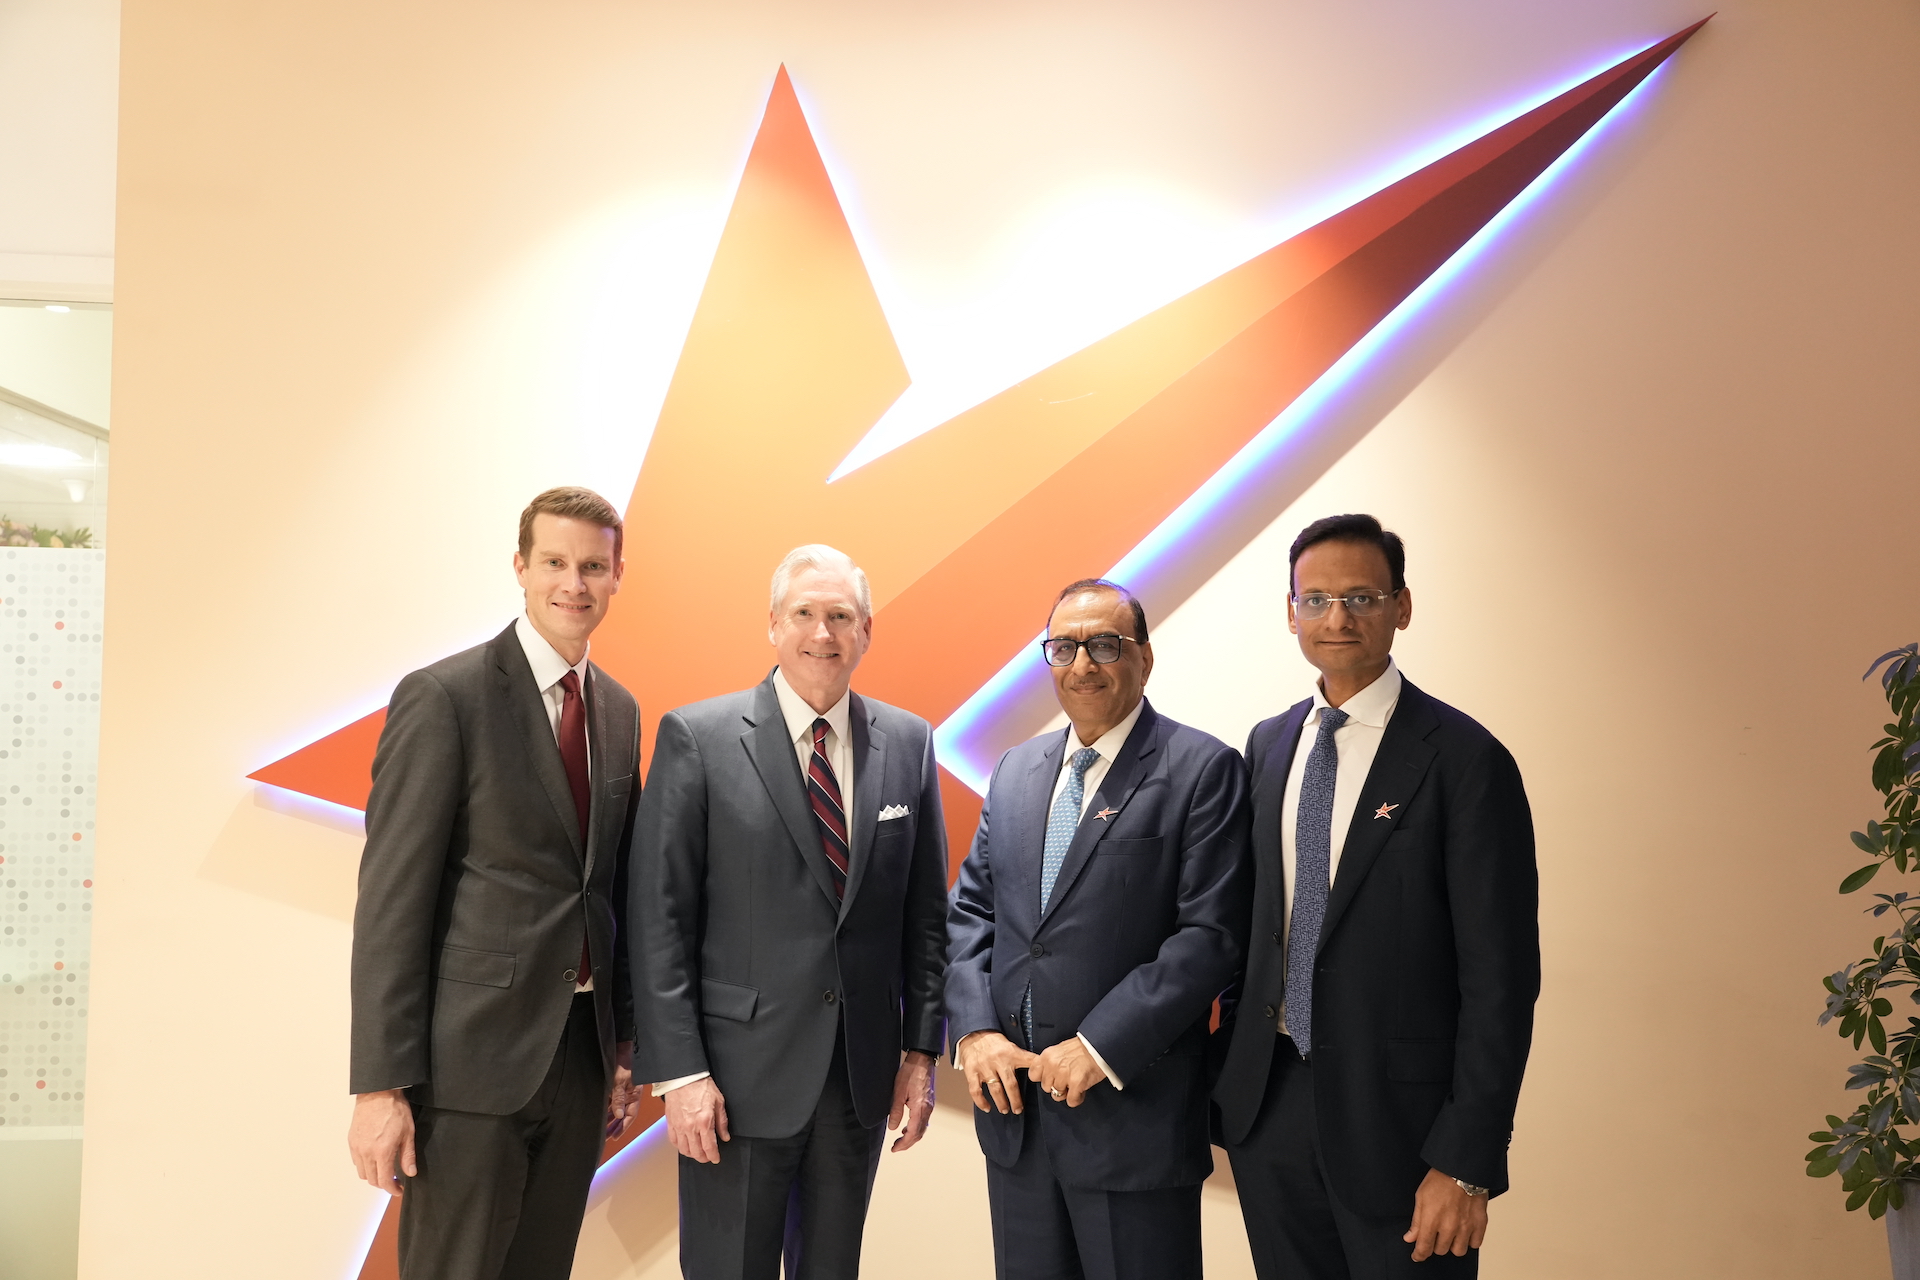
Dhruva, a leading tax consultancy firm in the Middle East, and Ryan, a leading global tax services and software provider, today announced that Dhruva will transition to the Ryan brand across the United Arab Emirates (UAE) and the Kingdom of Saudi Arabia. The rebranding will be completed by the end of 2026, bringing the practice under Ryan’s global identity and reinforcing its position as part of the world’s leading global-scale specialist in business tax.
The transition marks the next phase of the strategic joint venture announced in 2025 and reflects the continued integration of Dhruva’s regional capabilities with Ryan’s global platform, technology, and international resources. Clients across the Middle East will continue to benefit from the same trusted advisory teams, enhanced by access to Ryan’s worldwide expertise and service capabilities.
“The Middle East has been a strategic growth market for us for many years, and we have built a strong advisory practice founded on deep client relationships, technical excellence, and local market understanding,” said Dinesh Kanabar, Founder, Chairman, and CEO, Dhruva Advisors and Vice Chairman, Ryan.
“The transition to the Ryan brand marks a significant milestone in our journey and reflects the strength of our partnership. By combining our regional expertise with Ryan’s global scale, technology, and international capabilities, we are creating an even stronger platform to support clients across the region as they navigate an increasingly dynamic and evolving tax landscape.”
“The Middle East is one of the most important growth markets for tax advisory services globally, and we are investing in the region with a long-term view,” said Tom Shave, President of Ryan’s European and Asia-Pacific Operations. “Uniting under the Ryan brand strengthens how we serve clients across the UAE, Saudi Arabia, and Europe—bringing seamless access to our global expertise, technology, and international resources through one trusted platform. This transition marks an important milestone in our integration and reinforces our commitment to the region’s future.”
Ryan will continue to invest in its Middle East operations, expanding its team, capabilities, and regional presence across key markets, including Dubai, Abu Dhabi, and Riyadh. The practice provides comprehensive tax advisory services spanning corporate tax, value-added tax (VAT) and indirect tax, transfer pricing, mergers and acquisitions (M&A) tax structuring, research and development (R&D), and cross-border compliance.
“The response from our clients over the past year has been the clearest validation of this partnership,” said Nimish Goel, Leader, Middle East, Dhruva, a Ryan Affiliate. “From the outset, our teams have been integrating Ryan’s global capabilities in technology, specialized expertise, and best practices into the work we already lead in the region. Adopting the Ryan brand is the natural next step. It is the same people and the same trusted relationships, now carrying the name of the largest Firm in the world dedicated exclusively to business taxes.”
The rebranding will be implemented in phases during the second half of 2026, with signage, visual identity, and digital properties transitioning to the Ryan brand across the region.
 Have a question? +971 56 404 0503










 Trending11 months ago

 Tech News2 years ago

 Automotive2 years ago

 Tech News1 year ago