 Have a question? +971 56 404 0503

Tech Interviews
High-Performing Cybersecurity Mesh Platform to Protect All Enterprise Assets

Fortinet develops and sells cybersecurity solutions, such as physical firewalls, antivirus software, intrusion prevention systems, and endpoint security components. The Integrator engages Alain Penel, Regional Vice President – Middle East at Fortinet to discuss the company’s capacities to help enterprises against cyberattacks.
Speak about Fortinet’s capacities to offer comprehensive protection for enterprises in times of rising cyber attacks
To fight today’s evolving threats, organizations should look into a security platform based on a cybersecurity mesh architecture with security solutions that are designed to work together. A cybersecurity mesh architecture integrates security controls into, and across, widely distributed networks and assets. Defenders will need to plan now by leveraging the power of AI and machine learning (ML) to speed threat prevention, detection, and response. Advanced endpoint technologies like endpoint detection and response (EDR) can help to identify malicious threats based on behavior. Also, zero-trust network access (ZTNA) will be critical for secure application access to extend protections to mobile workers and learners, while Secure SD-WAN is important to protect evolving WAN edges.

Alain Penel, Regional Vice President – ME at Fortinet
Together with the Fortinet Security Fabric, organizations can benefit from an integrated security platform that secures all assets on-premises, in the data center, and in the cloud or at the edge.
What advice do you give to enterprises to secure their network and reduce vulnerabilities?
Today’s threat environment is constantly changing, and from distributed denial-of-service (DDoS) attacks to ransomware, the frequency, volume, and sophistication of cyberattacks show no signs of slowing down. Every organization, from small businesses to the largest enterprises and service providers, in every industry, requires network security to protect critical assets and infrastructure from a rapidly expanding attack surface.
Organizations need to develop a Security-driven Networking strategy that tightly integrates an organization’s network infrastructure and security architecture, enabling the network to scale and change without compromising security operations. This next-generation approach is essential for effectively defending today’s highly dynamic environments – not only by providing consistent enforcement across today’s highly flexible perimeters but by also weaving security deep into the network itself.
SMEs face large-scale cyber threats than large enterprises. How can they defend their physical and cloud networks? What are the solutions Fortinet offers to them in order to protect their digital ecosystem?
SMEs struggle to implement strong, holistic security across their business for a variety of reasons and too often rely on piecemeal security cobbled together with multiple vendors’ point products that do not operate cohesively. Ultimately, this results in inflated costs and stagnating growth, as investing in technology that would help the business be more productive is delayed by security. Cybersecurity for SMEs must therefore be simple, cost-effective, and easy to deploy.
Fortinet’s small and mid-size business security solutions deliver a path to complete protection. Clear ROI is delivered without sacrificing security with tight integration, automation, and visibility across the entire cybersecurity footprint to improve effectiveness, reduce cycles, and scale as the company grows. Cloud-based, centralized management simplifies ongoing operations with business-driven rules and policies so businesses can quickly consume new technology while keeping the business safe from attack.
Give insights into the partner collaboration Fortinet has made globally in the last two years
Fortinet is committed to helping partners be able to meet new and changing customer demands created by the work-from-anywhere models through Fortinet’s Engage Partner Program and enablement tools for partners.
As an example, last year Fortinet introduced new Specializations focused on high growth areas with additions, including “zero trust” access, operational technology, and security operations. Specializations help partners further distinguish their expertise among current and potential customers as trusted partners who have the knowledge, services, and technologies to fulfill customer business needs.
Elaborate on Fortinet’s business strategies in the Middle East?
In the region, we see strong interest in secure SD-WAN, cloud, and OT areas. By transforming their WAN architectures with SD-WAN, organizations can leverage such functions as dynamic path selection, optimized application delivery, and accelerated cloud on-ramp to deliver business-critical applications to the WAN edge – even for the most bandwidth-hungry applications – all while delivering instant ROI benefits. A secure SD-WAN solution goes further as it also includes a full stack of integrated, enterprise-class security features, and centralized management so it can be seamlessly incorporated into the larger corporate security framework. In 2021, we saw many attacks on critical infrastructure. Attacks against OT systems and critical infrastructure can have dire consequences for the lives and safety of both workers and consumers. OT organizations need to deploy cohesive solutions across their converging IT and OT networks. A platform approach is essential for OT organizations since their security considerations must extend beyond the on-premises system. Now they also must cover the operating system, the network infrastructure, and take the increased dependence on enabled Internet of Things (IoT) and Industrial Internet of Things (IIoT) devices into account as well. Cybercriminals certainly aren’t going to let up in 2022. As digital innovation accelerates, organizations are increasingly reliant on secure cloud solutions and infrastructures. Fortinet Adaptive Cloud Security Solutions provide the necessary visibility and control across cloud infrastructures, enabling secure applications and connectivity from the data center to the cloud.
How do you react to the increasing competition in the security solutions market?
Competing in today’s highly dynamic digital marketplace requires tools built around security-driven Networking principles that are designed to adapt to constantly changing requirements. We tightly integrate security with networking and connectivity solutions to ensure that even the most dynamic environments and edges are always protected. By weaving security and networking together, security no longer functions as an overlay.
Enterprises need more than siloed solutions in today’s complex environment. This is why the Fortinet Security Fabric is the answer to their security challenges: it ensures that solutions deployed anywhere, regardless of their form factor or the network they run on, can see each other, share threat intelligence, and coordinate a unified response to threats. It supports our unique security-driven networking approach that blends security, networking, and connectivity into a unified solution. Our advances in AI-based security technology are woven into the Security Fabric, helping ensure that organizations can receive essential, actionable threat intelligence, identify, and investigate unusual behavior, and coordinate a unified response across the entire distributed network to neutralize threats in seconds.







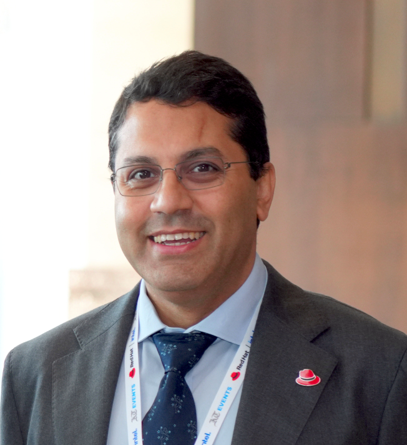
Exclusive interview with Anirban Mukherjee, Director of Solutions Architecture, Red Hat
Digital sovereignty is increasingly moving beyond data residency. What does genuine operational control look like for organisations that need to retain control over their data, applications and infrastructure?
Data residency answers where information sits. Operational control answers who can run, inspect, recover, and change the stack when it matters.
In practice, that means organisations can choose where workloads run – on premises, sovereign cloud, or public cloud – without rewriting applications every time. It means they can audit the software supply chain, keep recovery paths under their own governance, and decide which models, tools, and partners sit in their AI and application environments.
For many MENA enterprises and public-sector bodies, the test is simple: can you keep serving citizens and customers if a single vendor, region, or connectivity path is constrained? Open hybrid platforms give you that room to manoeuvre because the control plane and the open source components stay portable.
As organisations continue to rely on hyperscalers, where do you see the strongest case for combining public cloud with sovereign cloud and on-premises environments?
Hyperscalers remain excellent for elasticity, global reach, and certain managed services. The strongest case for a mixed model is when data sensitivity, latency, or regulatory expectations vary across the same organisation.
We routinely see customer data, AI inference close to the data, and regulated workloads stay in sovereign or on-premises environments, while less sensitive or bursty workloads use public cloud. The point is not to reject public cloud. It is to stop treating it as the only place innovation can happen.
An open hybrid cloud approach lets MENA organisations keep one consistent platform experience across those footprints, so teams are not rebuilding skills and tooling for every environment.
Could the growing AI infrastructure requirement actually increase technology concentration, and what can organisations do to avoid creating a new form of dependency around AI platforms?
Yes, the growing AI infrastructure requirements can actually increase technology concentration, – if every AI workload is tied to one model provider, one accelerator vendor, or one proprietary stack, concentration risk simply moves up a layer.
Organisations reduce that risk by treating AI like the rest of enterprise IT: multiple models for multiple jobs, open tooling where possible, and a platform that can run across hardware and clouds. Smaller, purpose-built open models are often a better fit for specific enterprise tasks than relying on one giant external model for everything.
In the Middle East, where national AI strategies are accelerating investment, the winners will be the ones who can innovate quickly without locking the next decade of infrastructure decisions into a single vendor path.
Open hybrid cloud is often positioned as a way to balance control with access to innovation. What does a mature open hybrid cloud strategy look like in practice?
Maturity looks like consistency. Same platform, same security and policy controls, same developer experience – whether the workload sits in a national data centre, a partner sovereign cloud, or a hyperscaler.
It also looks like deliberate placement: you put each application and AI workload where it creates the best outcome for cost, performance, and governance, and you can move it when those conditions change.
For solution architects in this region, the practical question is: can the customer ship new services without creating a parallel stack every time? If the answer is yes, the hybrid strategy is working.
Vendor dependency is difficult to eliminate entirely. How should organisations assess concentration risk and maintain credible alternatives without creating unnecessary complexity?
You will always have dependencies. The goal is to make them conscious and reversible.
Assess concentration by asking: what breaks if this vendor changes pricing, exits a market, or restricts a capability? Which workloads have no second path? Where does your data or model IP become hard to extract?
Credible alternatives do not mean running five of everything. They mean open standards, portable workloads, and a clear exit or dual-run plan for the few systems that truly matter. Complexity comes from unmanaged sprawl. Discipline comes from a shared platform and clear ownership of what must stay portable.
Red Hat’s role is to help customers keep that optionality – from infrastructure through to AI – so strategic independence is designed in, not bolted on after a crisis.
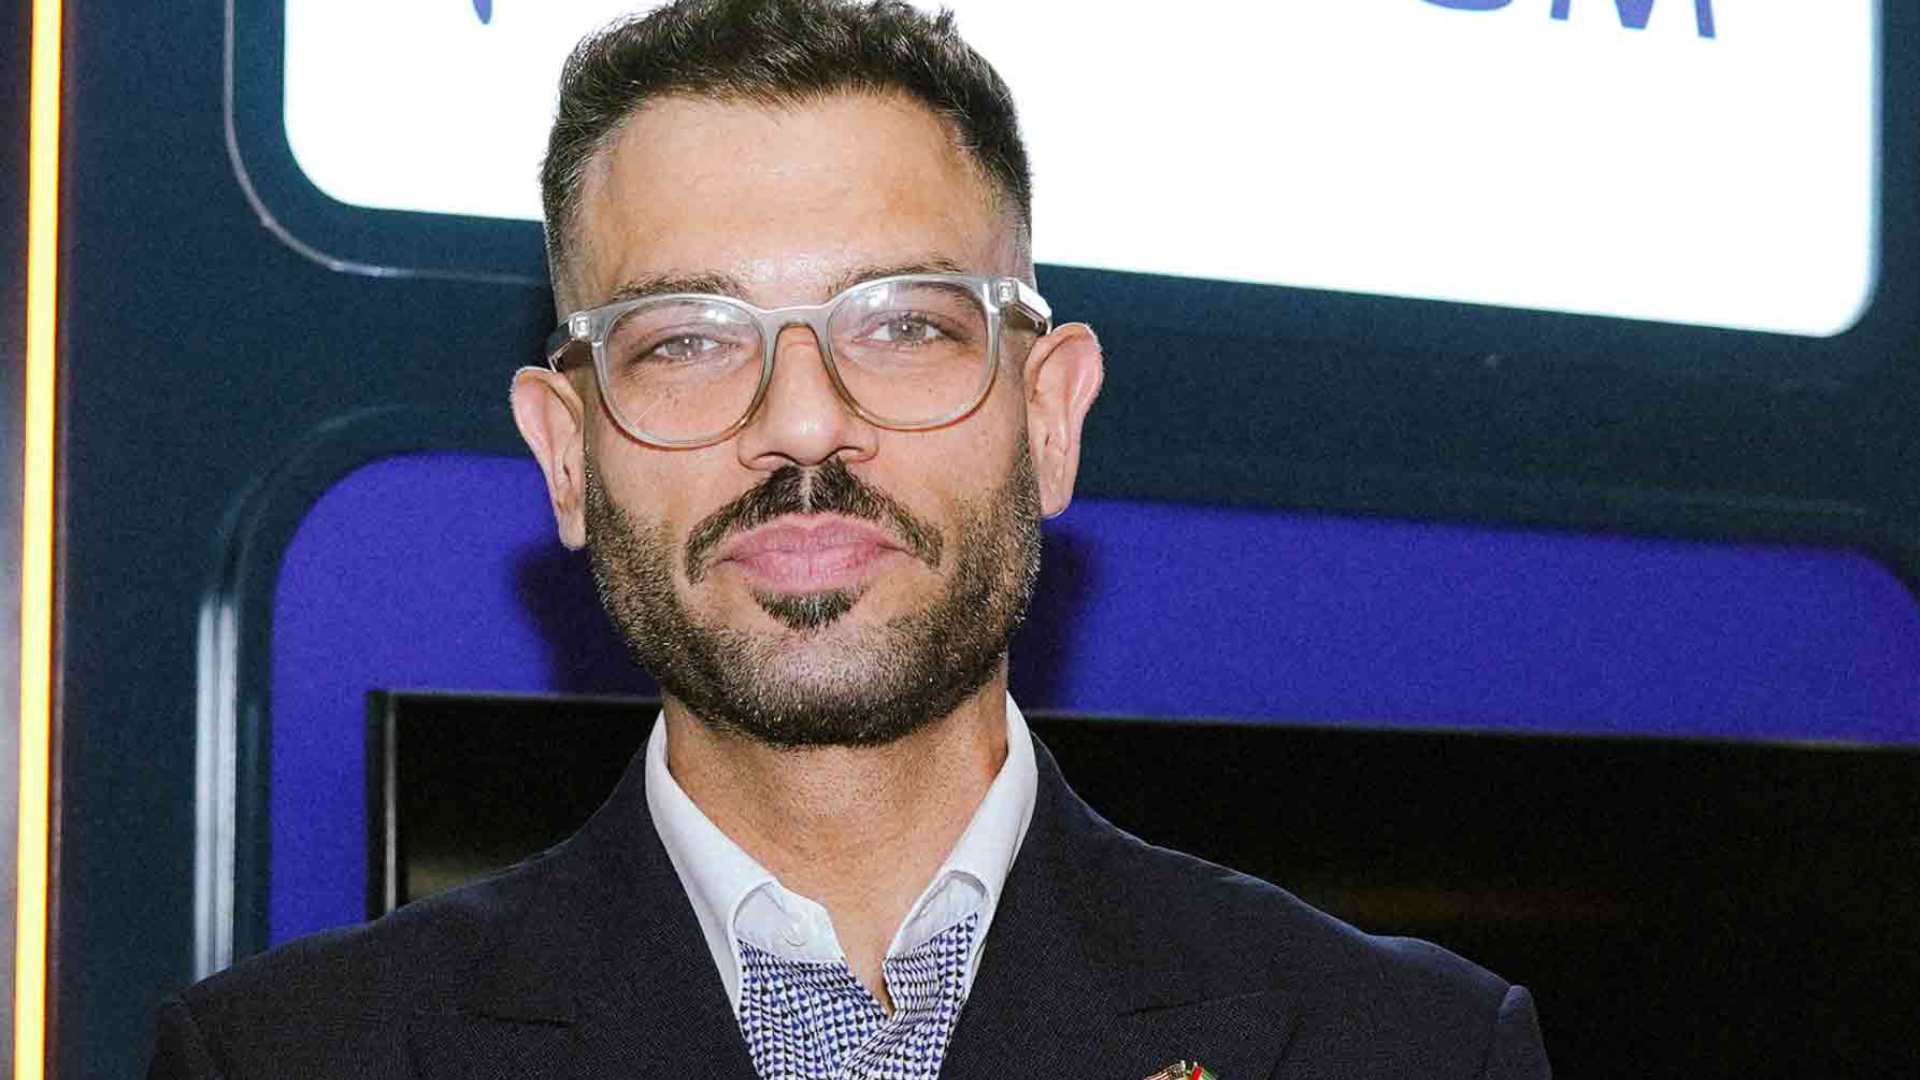
Exclusive interview with Shadi Hatoum, Regional Director MEA at Tealium
The UAE is moving quickly from AI experimentation to deployment. What do you think will determine which organizations actually turn adoption into measurable business value?
The organizations that create measurable value will be those that connect AI to a clearly defined business decision, then give it the right data and operating model to support that decision.
The UAE has already built significant momentum. Boston Consulting Group found that 42% of UAE organizations qualify as AI Leaders, while 37% have reached the scaling stage of AI maturity. The next test is whether that maturity translates into sustained outcomes.
Deploying a model is not the same as changing how a business operates. AI needs trusted, consented, and real-time context around customer identity, behavior, intent, and journey stage. It also needs clear ownership, measurable objectives, and teams that understand how to use the output.
From my perspective, data readiness and organizational adoption will be the two biggest differentiators. The organizations that can put reliable context in front of AI at the moment of decision, and embed the resulting insight into daily workflows, will be best positioned to turn adoption into measurable value.
How much of the current gap between AI ambition and AI impact comes down to fragmented or outdated customer data?
A significant part of the gap comes down to data readiness, although technology alone is not the whole answer. Most organizations do not lack data. Their challenge is that the data is fragmented, difficult to interpret, or unavailable when a decision needs to be made.
Historical data provides useful depth, but AI also needs data in motion. It needs to understand what a customer is doing now, what has changed, what the customer has consented to, and whether the signal belongs to the correct individual or account.
Tealium’s Future of Customer Data research found that 88% of organizations consider real-time data important to achieving business objectives. That is important because an AI system working from yesterday’s profile may produce a technically valid recommendation that is no longer relevant.
The real opportunity is to create a trusted context layer that connects identity, behavior, consent, and intent, then makes that context available to models and decisioning systems while the customer interaction is still taking place.
Does agentic AI create a new governance problem for enterprises, particularly when agents are acting on customer data without constant human intervention?
Agentic AI does not make the principles of governance entirely new, but it raises the stakes and increases the speed at which controls need to operate. When an AI agent can move from recommendation to action, governance can no longer be treated only as a periodic policy or review exercise. It needs to operate within the data flow and decision process itself.
Enterprises need clear controls over which data an agent can access, the purpose for which it can use that data, how identity and consent are verified, which actions it is authorized to take, and when a person must review or approve the outcome.
The key question is not only whether an agent can access a piece of customer data. It is whether the agent should use that data for this customer, for this purpose, at this moment.
That requires trusted data, current consent, auditability, defined action limits, and clear escalation paths. As autonomy increases, accountability needs to become more precise, not less.
Which sectors in the Middle East do you think are furthest ahead in using real-time customer data and AI together effectively?
From my experience across the region, telecommunications and travel, hospitality, and tourism are among the most active and promising sectors because they generate frequent customer signals and have a clear need to respond in the moment.
In a recent discussion with the Chief Commercial Officer of a major telecom operator in the region, we talked about growth as filling a bucket while also stopping the leaks. Acquisition fills the top, but poor service, irrelevant engagement, and unresolved friction allow value to escape through churn. Sustainable growth requires both attracting new customers and protecting the loyal customer base already in the bucket.
This is where AI-supported decisioning can create real value. Trusted, consented, real-time behavioral data can help an operator recognize changes in usage, service issues, digital engagement, and signs of churn. The next best action may be to resolve a problem, recommend a more suitable plan, position a bespoke package at the right time, or avoid making an offer when the customer first needs support.
The objective is not to push more offers. It is to improve relevance and timing. That can support retention, strengthen loyalty, and create opportunities to grow average revenue per user, or ARPU, by responding to what the customer needs in that moment.
Travel, hospitality, and tourism have a similarly strong opportunity. The customer journey moves from inspiration and research to booking, arrival, the in-destination experience, and loyalty. Each stage creates different needs. A traveler facing disruption needs assistance, while a guest already at a destination may value a timely, personalized experience or service.
These sectors show why hyper-personalization at scale depends on trusted, consented behavioral data in motion. The value comes from giving AI initiatives the current context they need to choose the next best action for that specific moment.
At AI Everything Abu Dhabi 2026, what are the biggest changes you are seeing in the conversations enterprises are having compared with a year or two ago?
The biggest change is that enterprises are no longer asking whether they should adopt AI. They are asking how to move it into production, connect it to measurable outcomes, and govern it at scale.
A year or two ago, many conversations centered on experimentation and individual use cases. Today, the questions are more operational. Leaders want to understand how AI will work with their existing data, how agents will receive current customer context, how decisions will be controlled, and how value will be measured beyond a successful pilot.
I am also hearing much more emphasis on adoption. Organizations recognize that a model does not create value by itself. Teams need clear use cases, practical training, shared measures of success, and confidence in the data behind the recommendation.
The conversation has therefore moved from AI capability to AI readiness. That includes the quality of the data foundation, the governance around it, the ability to make decisions in real time, and the people and processes required to turn those decisions into action. For me, that is a sign that the market is becoming more mature and more focused on sustainable business impact.
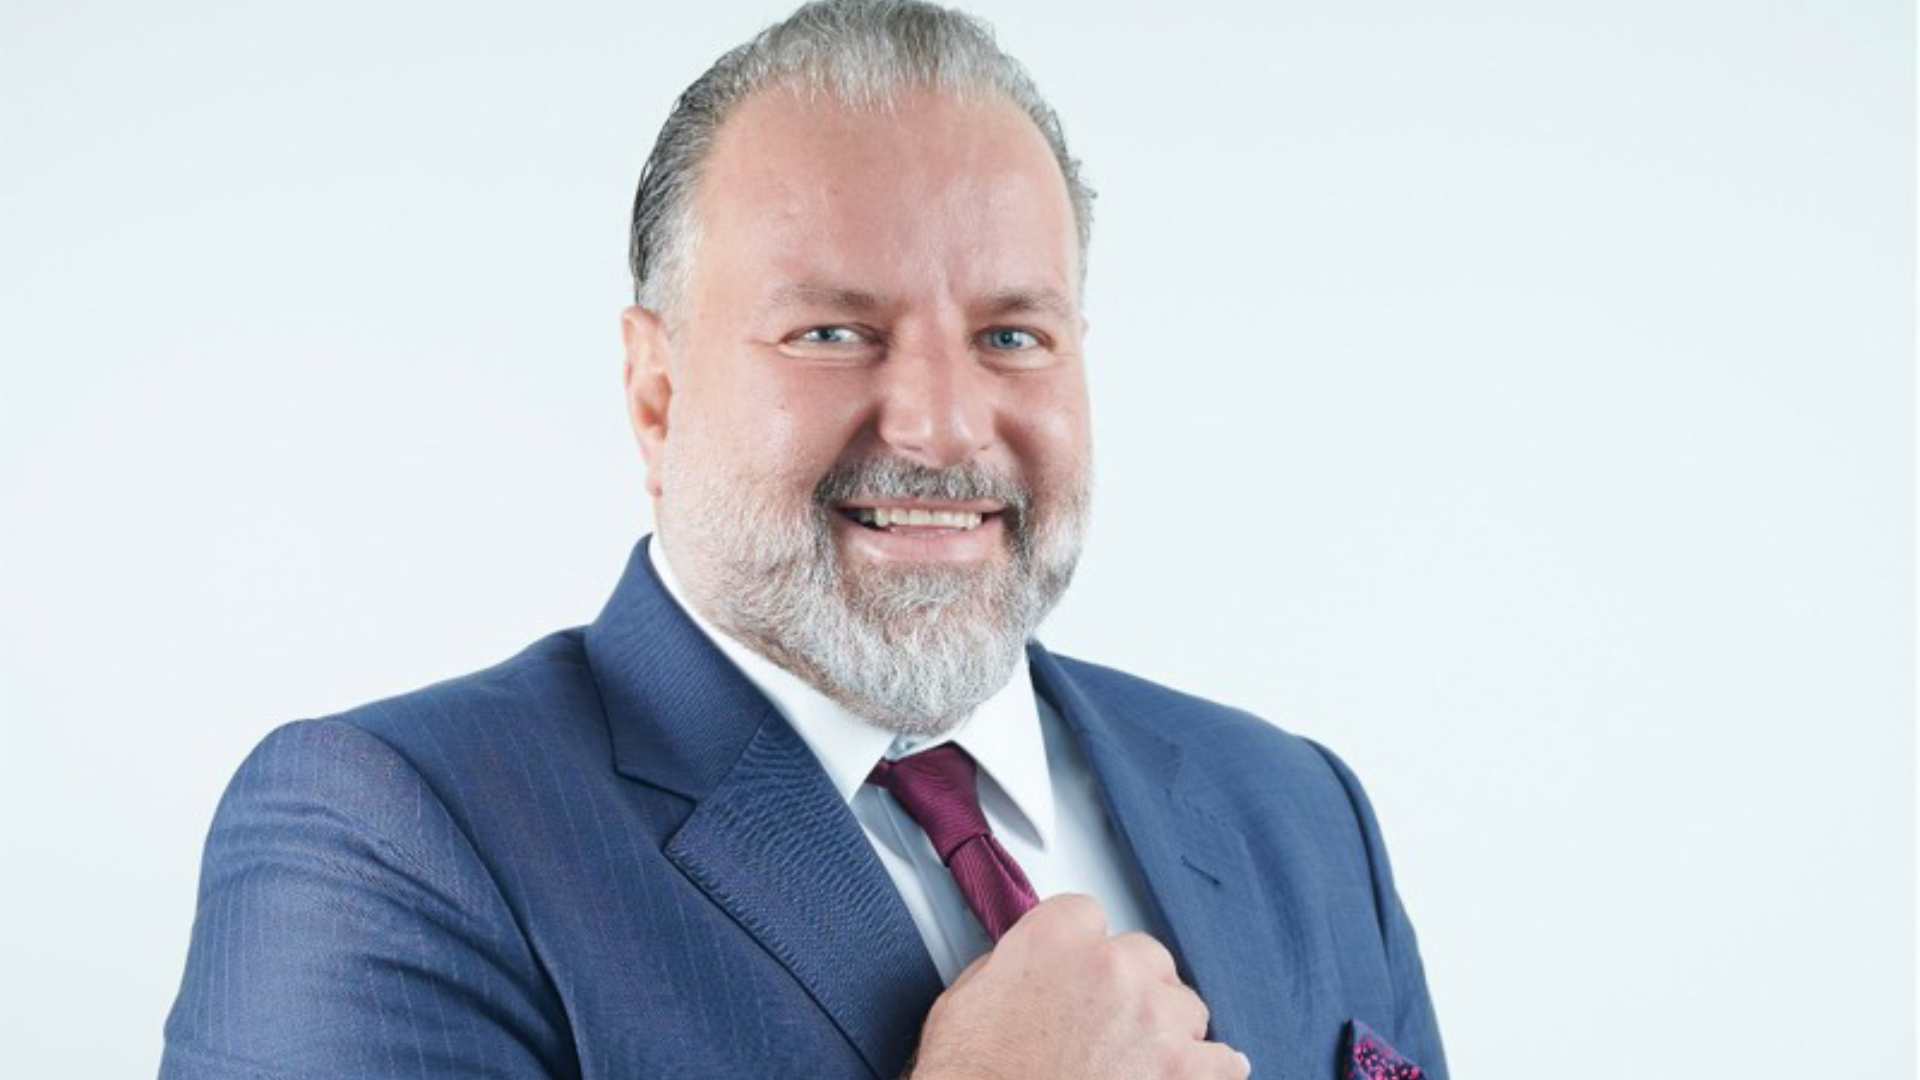
Exclsuive interview with Fady Richmany, Corporate Vice President and General Manager, Emerging Markets at Commvault
Integrated Media is at GISEC Global Dubai 2026 with Fady Richmany, Corporate Vice President and General Manager, Emerging Markets at Commvault
How is AI changing the attack surface for organizations in the region?
AI is crucial for digital transformation, so we are not debating the importance of AI. I think the UAE is one of the most advanced countries when it comes to adopting technology. The Dubai Government has also announced plans to use agentic AI extensively in the coming years
However, AI comes with a significant amount of data and introduces new types of identities. We are no longer dealing only with human identities but are increasingly dealing with robotic and AI-agent identities that can access data and systems. This creates additional complexity and consequences from an identity and security perspective.
At the same time, AI-powered attacks are another major concern. In the past, a hacker typically needed to be highly technical. Today, with AI, launching sophisticated attacks can become much simpler.
So, AI is important, but it needs to be utilized properly and governed effectively. There needs to be a balance when organizations and large enterprises adopt these technologies.
Why are threat actors increasingly targeting backup and recovery environments?
Backup and recovery are the last line of defence.
When a company is compromised, one of the first things it needs to do is access its backups to recover its data and operations. Hackers understand this. If they want their attacks to be effective, they also need to target the backup environment.
This is where companies like ours, along with many others in the industry, play an important role in making sure that backups remain clean, protected, and safe so organizations can recover when an incident occurs.
How does identity management need to evolve as AI agents and autonomous workloads multiply?
Agentic AI is putting additional pressure on IT because it is creating many robotic identities.
We have also seen attacks where AI has been used with little or no human intervention. This creates an additional security burden, which means these identities need to be properly protected.
Our approach focuses on the recovery side. Organizations need to use the appropriate security technologies available in the market to protect their environments and ensure that the right identities have access to the right resources.
But we also need to address what happens when an identity is compromised. How do you recover the environment? How do you recover the identity infrastructure? That is becoming a very important topic.
What does Cloud Unity offer beyond separate point solutions?
Cloud Unity brings together identity, security, and operational resilience. We combine people and processes and work closely with many of the leading security technology partners in the market.
We integrate information from different technologies and provide identity resiliency to help protect organizations from both sides of the problem.
We also have something called ResOps, or Resiliency Operations. It is a methodology for how organizations should operate. We believe organizations need to educate their people, keep them aware, and make sure everyone understands their role during a crisis. They also need to modernize their processes.
All of this comes together to make sure the environment remains resilient and productive. And this is not a one-time exercise but has been continuously tested – time and again.
How does ResOps help organizations move from reactive security to a more measurable and proactive approach?
In the olden days, we used what we called backup drills. This is particularly common in banking and government, where people would come together every quarter and check whether the backup was working.
But that approach is no longer enough.
Recovering data is not simply about recovering the information. During a cyberattack, you need to recover clean data and ensure that the environment you are restoring is safe. That means organizations need continuous testing. You have to align people, processes, and technology and make testing an ongoing activity.
When a compromise happens, everyone needs to know their role – Who has access? What are the steps that need to be followed? Who is responsible for each action? The ultimate objective is to be able to recover a clean copy of the data and get the organization back into operation as quickly and safely as possible.
What will the new Center of Excellence in Abu Dhabi focus on, and how will it support the UAE’s digital transformation goals?
One of our strategies is to align closely with local authorities, and work together with them. We work very closely with the UAE Cyber Security Council and have developed this initiative together with them.
The purpose of the Center of Excellence is to bring innovation to the region. It will be a center for innovation, with R&D and technology development taking place in the region. It will also be a center for developing local talent. We are partnering with universities and aim to train young Emiratis in areas such as cyber resilience and cyber defense. It will also be a center for awareness.
I would quote what Dr. Mohamed Al Kuwaiti said- the responsibility for cyber defense does not rely on one technology, one individual, or one government. It requires the entire community to work together to fight cyber threats. That is the purpose of the center. It is to bring all these elements together, support the cybersecurity community, and give back to the region. We want to create awareness, talent, and innovation.

IKEA Turned Last-Minute Hosting into a 90-Second Guest-Ready Tidy-Up Challenge
Building Digital Sovereignty Through Operational Control
A Coffee and Macaroon Affair Acacia Lounge


-
 Trending12 months ago
OPPO A6 Pro 5G Review: Reliable Daily Driver
-

 Tech News2 years ago
Denodo Bolsters Executive Team by Hiring Christophe Culine as its Chief Revenue Officer
-
 VAR1 year ago
Microsoft Launches New Surface Copilot+ PCs for Business
-
 Automotive2 years ago
AGMC Launches the RIDDARA RD6 High Performance Fully Electric 4×4 Pickup
-
Tech Interviews3 years ago
Navigating the Cybersecurity Landscape in Hybrid Work Environments
-

 Hospitality2 years ago
Gulfood 2025 30th Edition Kicks Off Today, Setting New Benchmarks in F&B Growth and Innovation
-

 Tech News1 year ago
Nothing Launches flagship Nothing Phone (3) and Headphone (1) in theme with the Iconic Museum of the Future in Dubai
-
 VAR2 years ago
Samsung Galaxy Z Fold6 vs Google Pixel 9 Pro Fold: Clash Of The Folding Phenoms