 Have a question? +971 56 404 0503

Tech Features
The Urgent Relevance of Cybersecurity for Organizations: Three Key Messages


By Iris Lorscheid, Professor for Digital Business & Data Science at University of Europe for Applied Sciences, Campus Hamburg
In an increasingly digital world, the importance of cybersecurity for organizations cannot be overstated. As we navigate through 2024, cyber threats are evolving at an alarming rate, and the need for robust security measures has never been more pressing.
This article aims to highlight the critical relevance of cybersecurity for organizations and present three essential messages that every organization should heed to protect their assets and maintain trust.
Message 1: Cybersecurity is a Non-Negotiable Priority
In today’s landscape, where data breaches and cyber attacks are becoming routine headlines, treating cybersecurity as an optional or secondary concern is a recipe for disaster. Every organization, regardless of its size or industry, must recognize that cybersecurity is a fundamental aspect of its operations. Here’s why:
Cyber attacks can lead to substantial financial losses. The costs associated with data breaches, including regulatory fines, legal fees, and the expense of mitigating the damage, can cripple an organization. For instance, in 2024, Dell faced a breach affecting 49 million customers, which not only dented their reputation but also resulted in significant financial repercussions.
When an organization suffers a data breach, the immediate fallout often includes a loss of customer trust. Customers expect their personal information to be safeguarded, and any compromise can lead to a loss of confidence that is difficult to rebuild. This erosion of trust can have long-lasting effects on customer loyalty and brand reputation.
Cyber attacks can disrupt business operations, leading to downtime and loss of productivity. Ensuring robust cybersecurity measures can help prevent such scenarios and maintain smooth operations.
Actionable Steps
To make cybersecurity a priority, organizations should:
- Allocate adequate resources and budget for cybersecurity initiatives.
- Implement comprehensive security policies and procedures.
- Regularly assess and update security measures to address evolving threats.
Message 2: Human Element is Key to Cybersecurity
While advanced technologies and sophisticated security systems are crucial, the human element remains a critical factor in cybersecurity. Human error is often cited as a leading cause of data breaches, making it essential to focus on training and awareness. Here’s why the human element matters:
Cybercriminals frequently use social engineering techniques to manipulate individuals into divulging sensitive information. Phishing emails, for example, are designed to trick recipients into clicking malicious links or providing confidential data. AI will play a key role in pishing attacks in the near future. Training employees to recognize and respond to these threats is vital.
Not all threats come from outside the organization. Insider threats, whether intentional or accidental, can be just as damaging. The Data Breach Investigation Report already identified in 2021 that 22% of cyber security threats are caused by internal actions. Employees with access to sensitive information can inadvertently or maliciously compromise security.
Employees may unknowingly fall victim to phishing attacks. AI algorithms can analyze vast amounts of data to identify vulnerabilities and create targeted attacks that are harder to detect by employees and defend against.
Encouraging good cyber hygiene practices among employees can significantly enhance an organization’s security posture.
Actionable Steps
To leverage the human element effectively, organizations should:
- Conduct regular cybersecurity training and awareness programs.
- Foster a culture of security awareness where employees feel responsible for protecting the organization.
Message 3: Proactive Measure are Essential for Cyber Resilience
In the face of ever-evolving cyber threats, a reactive approach to cybersecurity is insufficient. AI can automate the process of launching cyber attacks, enabling attackers to execute a higher volume of attacks with greater precision. This automation reduces the time and effort required to conduct attacks, increasing the scale and frequency of cyber threats. AI-powered botnets can automatically scan for and exploit vulnerabilities across thousands of systems simultaneously, overwhelming traditional security defenses.
Continuous monitoring of network activity allows organizations to detect unusual behavior and potential threats in real-time. Advanced security information and event management systems can provide valuable insights and enable quick response to incidents. AI-empowered security systems can defend AI-empowered attacks.
Overall, AI continues to be a double-edged sword in the realm of cybersecurity. While AI enhances security measures through advanced threat detection and response capabilities, it also empowers cybercriminals to launch sophisticated attacks. AI-driven attacks can adapt and learn from defensive mechanisms, making them more challenging to combat. Organizations must leverage AI to strengthen their defenses while staying vigilant against AI-powered threats.
Conducting regular security audits and vulnerability assessments helps identify and address weaknesses before they can be exploited. This proactive approach ensures that security measures are always up to date and effective against current threats.
Here is why being proactive is crucial:
Having a robust incident response plan in place is essential for minimizing the impact of a cyber attack. This plan should outline clear procedures for identifying, containing, and recovering from incidents. Regularly testing and updating the plan ensures readiness when an attack occurs.
Cybersecurity is not just an individual organization’s concern. Collaboration with industry peers, government agencies, and cybersecurity experts can provide valuable threat intelligence and enhance overall security. Sharing knowledge and resources can help organizations stay ahead of emerging threats.
Actionable Steps
To build cyber resilience, organizations should:
- Invest in continuous monitoring and advanced threat detection systems.
- Conduct regular security audits and vulnerability assessments.
- Develop and regularly update a comprehensive incident response plan.
- Collaborate with external partners for threat intelligence and best practices.
Conclusion
As we progress through 2024, the relevance of cybersecurity for organizations is more apparent than ever. By treating cybersecurity as a non-negotiable priority, recognizing the critical role of the human element, and adopting proactive measures, organizations can protect themselves against the growing tide of cyber threats. These three key messages—prioritizing cybersecurity, leveraging the human element, and being proactive—are essential for maintaining security, trust, and resilience in today’s digital landscape. It is imperative that organizations of all sizes and industries take these messages to heart and implement robust cybersecurity strategies to safeguard their future.
BY SRIJITH KN & SUBRATO BASU

As AI spending rises and experimentation gives way to accountability, the real challenge for business leaders is no longer access to technology, but proving value, controlling cost and redesigning how organisations work.
Every year, the technology industry promises a breakthrough that will change everything. New models arrive, computing capacity expands and investment reaches new highs. Then, somewhere between the product demonstration and the quarterly earnings call, someone asks the question that matters most:
What did all of this actually improve?
That question came into sharper focus in 2026.
Artificial intelligence moved deeper into everyday business. Companies deployed assistants, experimented with agents and embedded AI across customer service, software development, compliance, finance and operations.
Yet adoption turned out to be the easy part.
Installing an AI assistant is relatively straightforward. Redesigning an organisation around it is not.
Fragmented systems, poor-quality data, unclear ownership, weak governance and sceptical employees do not disappear because a company has purchased another software licence.
Businesses do not need another year of impressive demonstrations. They need to know whether AI is helping them make better decisions, serve customers more effectively and run their operations more reliably.
That shift is turning AI from primarily a technology question into a management one.
From experimentation to accountability
The adoption numbers appear impressive.
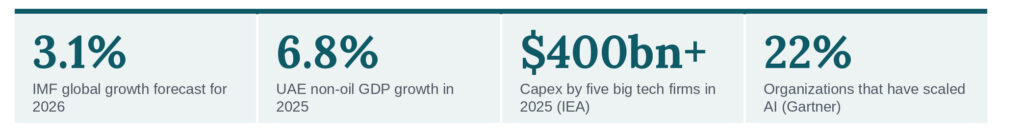
McKinsey found that nearly nine in ten survey respondents reported regular organisational use of AI in at least one business function. Gartner, using a different measure, found that only 22% of organisations had successfully scaled AI across multiple business units or adopted an AI-first approach.
The methodologies are different, but together they point to an important distinction: using AI is not the same as changing how a business operates.
The economics reinforce that concern.
In McKinsey’s Technology Trends Outlook 2026, one survey found that 93% of respondents had exceeded their AI budgets. Another found that only 37% of companies could attribute a positive EBIT impact to their AI programmes.
Those numbers create an uncomfortable boardroom question.
If spending continues to exceed expectations while measurable returns remain limited, what exactly are organisations paying for?
The clearest returns are likely to emerge where companies begin with a defined business problem: reducing customer-service resolution time, accelerating code review, simplifying invoice handling or strengthening compliance.
What becomes harder to justify is the proliferation of pilots with no accountable owner, no performance baseline and no clear route to economic value.
Automating a broken process can simply make the breakage happen faster.
Agentic AI raises the stakes
Agentic AI made this management challenge more significant in 2026.
Traditional generative AI largely responded to requests. Agents can increasingly perform multistep activities, interact with systems and execute actions.
That creates more opportunity, but it also introduces more cost, operational risk and responsibility.
Gartner has forecast that more than 40% of agentic AI projects will be cancelled by the end of 2027 because of escalating costs, unclear business value and inadequate risk controls.
It is a forecast rather than an observed failure rate, but the warning matters.
Giving software more autonomy only increases the need for organisations to define who owns the outcome, who monitors the process and who can intervene when something goes wrong.
The question for leaders is therefore becoming less about what an AI agent can do and more about what the organisation should allow it to do.
The economics nobody puts on the slide
AI is also forcing companies to think differently about technology costs.
The International Energy Agency reported that capital expenditure by five major technology companies exceeded $400 billion in 2025 and was expected to rise by another 75% in 2026.
The physical foundations of AI require enormous amounts of computing infrastructure, electricity, cooling, networking, land, semiconductors and highly specialised talent.
An individual AI task may become cheaper while the total technology bill continues to grow simply because usage expands.
That is not necessarily a problem if the additional activity creates measurable value.
But somebody needs to be able to explain what the extra expenditure produced.
Did it generate more revenue?
Did customers receive better service?
Did employees become more productive?
Did the organisation reduce risk?
Technology and finance leaders increasingly need to measure the cost per useful outcome, rather than concentrating only on the price of individual models, tokens or software licences.
Energy, computing capacity and infrastructure resilience now belong in the same boardroom conversation as digital transformation.
AI also creates a wider economic question
There is another issue that sits beyond corporate productivity.
A business may be able to reduce certain labour requirements through automation, but an economy still depends on people earning, consuming, creating businesses and paying taxes.
If productivity gains do not translate into new industries, new forms of employment or greater economic opportunity, the benefits become harder to sustain.
Reskilling cannot therefore be treated simply as a corporate social-responsibility programme.
It increasingly belongs at the centre of technology strategy.
The real measure of intelligent technology should not be how many jobs it eliminates or how many tasks it completes. It should be whether it creates durable value for enterprises while expanding economic opportunity around them.
The Gulf moves from technology buyer to builder
This is particularly relevant in the Gulf.
For years, the region was often described primarily as a major buyer of global technology. That description increasingly feels incomplete.
Across the UAE, Saudi Arabia and the wider Gulf, governments and businesses are investing in AI infrastructure, cloud capacity, digital government, data centres and technology ecosystems.
Stargate UAE, the planned one-gigawatt AI infrastructure cluster in Abu Dhabi, illustrates the scale of that ambition. Its first 200 megawatts were scheduled to come online during 2026.
Abu Dhabi’s ambition to build an AI-native government by 2027 and Dubai’s support for digital entrepreneurship point in the same direction.
But infrastructure alone does not create prosperity.
The more important question is whether that infrastructure lowers the cost of innovation and makes advanced technology accessible to the companies that drive the region’s everyday economy.
Can a UAE SME use AI to compete more effectively with a multinational?
Can a local healthcare provider deploy specialised intelligence without building an enormous internal technology operation?
Can a logistics company use automation to improve reliability rather than simply add another layer of software?
The Gulf has invested heavily in technological ambition. The next chapter will be about making that ambition useful.
That means moving from importing technology to developing capabilities, intellectual property, businesses and talent around it.
Innovation moves into the physical world
The technology conversation is also becoming broader than generative AI.
Physical AI is bringing intelligence into robotics, logistics, manufacturing, healthcare and mobility.
Digital twins, edge computing and intelligent energy systems are connecting digital decisions to physical operations. Smaller, specialised AI models may also offer better economics and governance than enormous general-purpose systems for narrowly defined industry tasks.
Quantum computing continues to advance, although business leaders should remain cautious about claims of immediate universal commercial impact.
The more urgent issue for many organisations is post-quantum cybersecurity.
Confidential information protected today could potentially become vulnerable as computing capabilities evolve, meaning organisations handling long-lived sensitive data need to begin thinking about cryptographic resilience well before large-scale quantum computing arrives.
Across these technologies, the competitive advantage is unlikely to come from collecting the greatest number of tools.
It will come from integrating the right technologies into an operation that works.
Trust becomes part of the business model
As AI systems gain access to more sensitive information and perform more consequential activities, cybersecurity becomes inseparable from business strategy.
The World Economic Forum’s Global Cybersecurity Outlook 2026 described an environment shaped by AI-enabled threats, geopolitical fragmentation and uneven cyber resilience.
AI agents interacting with financial systems, customer information or operational infrastructure raise the importance of identity controls, authorisation, monitoring and human intervention.
Cybersecurity can therefore no longer be treated simply as the responsibility of the security department.
It is increasingly about business continuity, reputation and customer trust.
The companies that can demonstrate that intelligent systems are secure, explainable and accountable may find that trust becomes a genuine competitive advantage.
2027: the numbers will have to add up
If 2026 was the year organisations experimented with how far AI could go, 2027 is likely to bring much tougher questions about whether those investments make economic sense.
A good demonstration will matter less than what a company can responsibly allow a system to do.
Agents will begin taking responsibility for defined activities, but each will require boundaries, monitoring and a human being who ultimately owns the consequences.
Boardroom conversations should shift from:
- How many AI tools have we deployed?
- to:
- What does this process cost now?
- How much faster is it?
- Has the error rate fallen?
- Are customers noticing the difference?
That scrutiny will extend beneath the software layer.
Energy availability, sovereign computing capacity, regulatory requirements and infrastructure resilience will increasingly influence where companies choose to invest.
The same scrutiny will reach the workforce.
Employees will need technical fluency, but they will also need business judgement: the ability to understand exceptions, question automated recommendations and take responsibility when systems get something wrong.
Access to another AI model will not be the defining advantage.
An organisation that operates better — at a cost that survives examination — will be.
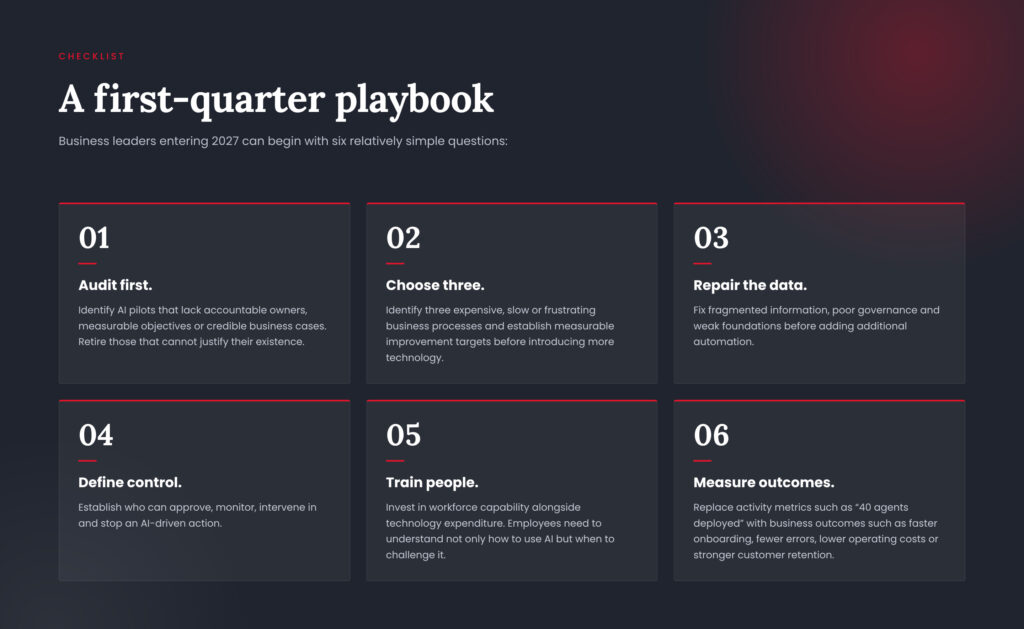
The question worth taking into 2027
As 2026 closes, business leaders should temporarily set aside the question of how much technology their organisations have adopted.
Instead, ask what the investment actually changed.
Did serving a customer become simpler?
Did an expensive process become more efficient without becoming less reliable?
Did employees gain the ability to spend more time on valuable work?
Can the improvement be seen in the numbers?
A technology budget is ultimately a statement of belief about the future.
In 2027, belief will not be enough.
AI adoption alone will no longer be impressive. The organisations that stand out will be those that can explain, in plain business terms, what they spent, what improved and who benefited.
And that may be the clearest indication yet that AI is becoming less of a technology problem — and much more of a management one.
Subrato Basu is an author, adviser and speaker on AI strategy and technology cost management. With nearly three decades of experience advising C-suite leaders, he helps organisations across North America, Asia Pacific and the Middle East turn technology investment into measurable business value.
Srijith KN is Senior Editor at Integrator Media, who is hands-on in covering enterprise technology, artificial intelligence, cybersecurity and the digital economy across the Middle East.
By Sourav Guha Roy, Practice Head – Cyber Academy, CPX
Prevention remains essential to cybersecurity, but it is no longer enough on its own. As AI-enabled threats become increasingly complex, convincing and harder to detect, a new question is gaining prominence in boardrooms across the region: if an attack succeeds, how quickly can the business recover? How effectively can teams recognize a threat, leaders make critical decisions under pressure and coordinate a response before disruption escalates?
For business leaders, the focus is shifting from simply keeping attackers out to containing damage, restoring critical services and maintaining business continuity. Building this capability requires more than technology safeguards. It means preparing people, establishing clear processes and ensuring teams can act decisively under pressure.
Recovery readiness: From prevention to preparation
Cyber readiness is often measured by what an organization puts in place before an incident: clear responsibilities, tested response plans and technology that supports detection and decision-making. But when an attack succeeds, the real measure of preparedness is how effectively are the people able to use these capabilities to limit disruption and restore critical services.
Cyber resilience extends beyond the initial response. It is an organization’s ability to adapt to disruption, maintain essential functions and recover while managing the wider impact on customers, employees and business performance. The speed and effectiveness of that recovery depend on more than the tools available. People must interpret alerts, assess business impact and make decisions that enable the organization to move forward.
This distinction has important implications for leadership. Preventing every incident may not be realistic, but organizations can prepare for the moments when prevention fails. The priority is to ensure that response plans work in practice, responsibilities are understood and teams can make coordinated decisions under pressure.
Three connected pillars of cyber readiness
A human-centric approach does not reduce the importance of technology. Instead, it aligns three interdependent pillars: people, process and technology.
- People provide context, judgment and ethical oversight. They need the confidence to pause when an instruction appears unusual, verify a request through a trusted channel and report concerns without delay. In an environment shaped by AI-generated impersonation, these behaviors are increasingly important.
- Process turns individual awareness into a coordinated response. Clear escalation routes, decision authority and defined ways of working help employees and specialist teams understand what happens after a concern is raised. Processes should also clarify the responsible use of AI, including which tools are approved, what information may be shared and how AI-related risks should be reported.
- Technology protects systems and supports human decisions by detecting suspicious activity, controlling access and monitoring how AI and organizational data are used. Yet an alert is only an indication that something requires attention. Without context, ownership and action, it does not create readiness or guarantee a timely recovery.
Consider a finance employee who receives an urgent payment instruction that appears to come from a familiar executive. Technology may flag unusual activity, process determines how the request is verified and escalated, and people apply judgment and involve the right decision-makers.
From the frontline to the boardroom
Cyber readiness should reflect the decisions expected of each role. Employees must recognize and report warning signs. Specialists must assess the impact, coordinate the response and restore operations securely. Leaders must make informed decisions when facts are incomplete, balancing security, continuity and accountability.
Readiness depends on the handoffs between these groups: employees need clear reporting routes, specialists need the authority and information to act, and leaders need timely insight into business impact.
Build capability through a continuous cycle
Human-centric readiness is not achieved through a one-time awareness campaign. A practical model is to Assess, Train and Simulate continuously.
Do employees verify unusual requests? Can specialist teams build a shared view of impact? Do leaders know when to intervene? Can critical services be restored within acceptable timeframes? The findings should feed back into the next assessment and improvement cycle.
Conclusion: Make recovery a business priority
No organization can guarantee that every cyberattack will be prevented. But every organization can decide how prepared it will be when one occurs. That means moving beyond prevention metrics to test how effectively teams contain incidents, protect critical services and restore operations.
The most important shift is to stop treating people as the weakest link and start preparing them as an active part of the defense. This does not mean turning every employee into a cybersecurity expert. It means ensuring that each person knows what to recognize, how to respond and when to escalate.
The strongest organizations will not be those that eliminate every human error. They will be those that give people the judgment, processes and support to prevent a single mistake from becoming a business crisis.
For boards and executive teams, the call to action is clear: ask not only how likely an attack is, but how long the business could operate under disruption. Cyber resilience is ultimately measured not by the absence of incidents, but by the ability to withstand them and recover. The organizations best positioned for the future will be those that make recovery readiness a business priority before the next attack begins.
Exclusive interview with Diego Parra, Managing Partner, Megarme
How are oil and gas companies in the GCC changing the way they inspect and maintain their equipment and infrastructure?
We see a stronger emphasis on equipment condition and the consequences of failure when operators plan inspection. Scheduled inspections remain important, alongside operating history, service conditions and the role each asset plays in the operation.
Two similar pieces of equipment may need different inspection plans because their service conditions, exposure or importance to the operation are different. A critical process line, for example, may require a different approach from a low-consequence utility line. The inspection method, coverage and timing should reflect those differences while meeting the applicable requirements.
Inspection history and equipment monitoring can help maintenance teams identify changes early enough to investigate and plan work. This is particularly useful offshore or where access depends on a shutdown, because arranging people, equipment and materials can take time.
At Megarme, we support this approach by providing condition information from the locations included in the inspection scope. Our findings help the operator and its engineering team decide what needs attention, what requires further assessment and what can be included in a planned maintenance campaign. We aim to make the findings clear enough to support those decisions.
What are the biggest challenges companies face when inspecting and maintaining offshore and onshore facilities, and how does Megarme help address them?
A practical challenge is obtaining a reliable assessment while working within the facility’s operating constraints. Access, process safety and inspection quality have to be planned together. The easiest location to reach may not be the one most likely to deteriorate.
Offshore, marine corrosion and possible fatigue at connections subject to repeated loading need attention. Weather windows, restricted deck space and transport arrangements also affect the work. Under-deck steelwork, derricks and flare structures can be demanding, particularly when inspection must be coordinated with lifting or other activities nearby.
Onshore, congested pipe racks, hot surfaces and operating process systems can restrict access. Isolation requirements and shutdown schedules often determine when work is possible. Entry into tanks or vessels introduces additional atmospheric and rescue considerations.
We help by planning the access and technical work together. An under-deck survey may require surface preparation, thickness measurements and weld examination before the engineering team can assess the findings and approve repairs. Identifying these dependencies early helps the operator prepare the work.
Our reports need to make inspection coverage and limitations clear. Work during operation is considered only where the process conditions, risk assessment, permits and required isolations allow it.
How does rope access help Megarme carry out inspection and maintenance work in hard-to-reach areas safely and efficiently?
Rope access allows us to position a qualified technician directly at the work location, including beneath a jetty, beside an elevated pipe support or at a derrick connection. For localised inspection and repair, it can reduce the access structures, material handling and space required.
We are an IRATA Operator and Trainer member. The normal rope access arrangement uses two independently anchored lines: a working line and a safety line. An IRATA Level 3 supervisor oversees the rope access safety arrangements, including equipment checks, rope protection, communication and a rescue plan suited to the location. Team size must support both the task and a potential rescue.
Our technicians also need the qualifications and authorisations for the work being performed. Rope access competence is separate from competence in NDT, welding or coating inspection. An ultrasonic examination carried out on ropes must meet the applicable inspection requirements, including calibration, surface preparation, probe positioning and coverage.
We select the access method around the task, duration, equipment loads and rescue requirements. Depending on the work, that may involve rope access alone or a combination of access arrangements. The practical benefit is being able to reach the required locations with a method suited to the inspection or repair.
How does Megarme use non-destructive testing (NDT) to identify corrosion, cracks and other damage before they become serious problems?
We use NDT to assess remaining wall thickness and look for indications of cracking or other damage. We select the method to suit the material, expected deterioration and inspection requirements.
For pipework corrosion, ultrasonic measurements establish wall thickness at the inspected locations. If we find an unusually low reading, we verify it, promptly raise any critical concern and extend the examination as required to establish the extent of the thinning. Corrosion mapping can provide more detailed coverage where localised attack is suspected. The lowest measured thickness and size of the affected area matter, because an average can conceal a severely thinned location.
Magnetic particle testing can reveal surface and near-surface discontinuities in ferromagnetic materials, such as carbon steel. Penetrant testing can reveal discontinuities open to the surface in suitable nonporous materials. Ultrasonic testing, including phased array, and radiography can be used to examine welds for internal discontinuities. Selection depends on the expected damage, component geometry and applicable requirements; each method has limitations.
We record the component, examination location, coverage, measurements and relevant images or scan data. The findings support the responsible engineer’s decision on further assessment, monitoring or repair. Repaired welds are re-examined as required by the applicable procedure and acceptance criteria. Qualified personnel, suitable procedures and prompt reporting are essential to making the results useful.
How do extreme heat, humidity and salt exposure in the Gulf affect industrial equipment, and what can companies do to protect their assets?
In the UAE and Saudi Arabia, asset protection has to reflect the location. Offshore and coastal facilities face salt exposure and periods of high humidity alongside heat. Further inland, heat and dust become more prominent considerations. The protection system must suit both the local exposure and the equipment’s operating conditions.
We pay particular attention to pipe supports, bolted connections, undersides of structures and insulated pipework. Corrosion can develop in a small, critical area while the wider structure appears acceptable. Moisture entering through damaged insulation cladding can remain against the steel, making targeted inspection and repairs to water-entry points important.
Coating performance depends on preparation and application. Salt, dust and other contamination must be controlled to the specified cleanliness limits, with the required surface preparation and coating thickness verified. Steel temperatures in summer can exceed a product’s application limits. Cooler hours still require checks for humidity and condensation. Some specifications require the steel to remain at least 3°C above the dew point, alongside the product’s other temperature and humidity limits.
Our inspection, surface preparation, coating and repair work can help address deterioration and its causes. Metal loss needs assessment and, where required, an approved repair before protection is reinstated. Leaving a water trap or damaged insulation seal in place can expose the asset to the same problem again.
How does Megarme help oil and gas operators extend the life of their assets while maintaining safety standards?
We support asset life extension by gathering inspection evidence and carrying out approved maintenance or repairs. The starting point is understanding the condition of the equipment, the extent of any damage and its significance for continued operation.
For pipework, thickness measurements and corrosion mapping provide information for assessing metal loss. Our access capability helps reach components that would otherwise be difficult to examine or replace. The inspection scope needs to reflect the expected damage and provide the information required for the engineering assessment.
Our maintenance and repair scope can include surface preparation, coating, work on columns and piping, structural welding and composite repairs, where appropriate to the assessed condition and approved scope. Composite repairs require an engineered design approved for the specific damage and service conditions, controlled installation and the required inspection and verification. Completed work needs the specified quality records before acceptance.
Life extension also requires a plan beyond the immediate intervention. The operator needs to know what should be monitored, when further inspection is required and which operating limits apply. We contribute inspection data and execution capability. The responsible operator and engineering authority determine fitness for continued service and approve any extension of operating life.
What steps does Megarme take to protect workers when carrying out inspection and maintenance work in challenging environments?
We plan our work around a task risk assessment, competent supervision, personnel fit for the assigned work and the facility’s permit requirements. The controls must be confirmed at the worksite, and any change in scope or conditions requires reassessment.
At operating facilities, this includes verified energy isolation, atmospheric testing and monitoring as required, and controls for hazards such as hydrogen sulphide or flammable atmospheres. We seek to avoid confined-space entry where a suitable alternative exists. Where entry is necessary, the arrangements must address unsafe oxygen levels and other identified hazards, with suitable ventilation, communication and a rescue plan specific to that space.
At height, we consider the people below as well as the technicians. Tools need suitable retention and checked attachment points, with exclusion zones appropriate to the task. Heavy equipment requires its own handling and securing arrangements. Accounting for tools when work is complete helps prevent a later dropped-object hazard.
Our heat management arrangements need to reflect the site conditions, workload and protective clothing. The assessment guides acclimatisation, work and rest arrangements, hydration and access to shaded or cooled recovery areas.
We expect personnel to stop work when conditions are unsafe. Supervisors must respond to fatigue, changing weather and any condition that compromises the controls or rescue arrangements.
How are new technologies changing the way oil and gas companies inspect equipment and plan maintenance?
Technology can improve inspection coverage and the speed at which information reaches maintenance teams. Across the industry, drones can support visual surveys, robots can carry sensors across suitable surfaces, and permanent monitoring can identify changes between periodic inspections. Their suitability depends on the asset and the information required.
Encoded ultrasonic scanning is a practical example. It links measurements to their positions, allowing wall loss to be mapped and compared with later examinations when the scan locations and measurement conditions are comparable. Digital records can connect those results with the asset reference, earlier findings and repair history.
We assess a technology by the information it provides and the decision it supports. A visual image may identify an area for closer examination. Confirming wall loss or characterising a defect requires a method suited to that task. AI tools can assist with screening where their performance has been validated for the intended use, with qualified personnel reviewing the results.
Our priority is to select methods that suit the component and expected damage, and to produce clear, traceable records. We use inspection findings to plan any further examination and support the engineering assessment and approval of required repairs.
How can companies reduce maintenance costs and downtime without compromising safety or equipment reliability?
Better preparation and fewer repeat interventions can help control maintenance costs and downtime. The cost of a task includes access, mobilisation, materials, permits, isolation, production disruption and verification. These need to be considered together when comparing ways to execute the work.
Before a shutdown, available inspection findings should be used to define repair scopes, prepare materials and spare parts, agree procedures and secure the necessary personnel. Operations, engineering and maintenance teams need to resolve dependencies early. Discovering that a repair needs additional materials or approval after equipment has been shut down can put the programme under pressure.
We help by coordinating compatible activities within an access campaign. Elevated steelwork, for example, may need condition assessment, NDT, a dropped-object survey and authorised coating repairs. When safely sequenced, these activities can share access arrangements and reduce repeat mobilisation. Required approvals and inspection hold points still apply.
Prompt decisions on findings and investigation of recurring defects also help prevent delay and rework. Useful performance measures include total maintenance cost, unplanned downtime, repeat failures and closure of critical findings. Any cost-reduction plan must preserve required inspections and the maintenance and testing of safety-critical equipment.
What are the main inspection, maintenance and safety challenges you expect the GCC oil and gas industry to face over the next few years, and how is Megarme preparing for them?
We expect an important challenge to be balancing maintenance of operating assets with inspection needs during construction and commissioning. When shutdowns and project activities overlap, there can be pressure on the availability of experienced personnel and technical supervision.
Advanced NDT technicians, welding and coating inspectors, and rope access supervisors need the competence and approvals for each assignment. Our preparation includes attention to training, personnel allocation and the technical support available to site teams. Resources need to match the work being accepted.
The quality of records handed over from construction to operations is another priority. Traceable weld records, baseline thickness measurements and coating inspection results give maintenance teams a useful starting point. Consistent component identification helps later inspection results be compared with the correct earlier records.
For existing facilities, corrosion in difficult-to-access areas and beneath insulation will continue to require attention. On safety, overlapping inspection, lifting and hot work need careful coordination. Heat exposure and fatigue also need to be reflected in staffing and schedules.
We are focusing on consistent technical review, equipment readiness and clear reporting across our regional operations. Our aim is to keep the standard of execution consistent as workloads change, with appropriate supervision and follow-up on significant findings.
PEAQ Brings a New Era of Social Wellness to Dubai

2026 in Review: Is AI Becoming More of a Management Problem Than a Technology Problem?

MidChains and Standard Chartered establish strategic banking partnership

OPPO A6 Pro 5G Review: Reliable Daily Driver

Denodo Bolsters Executive Team by Hiring Christophe Culine as its Chief Revenue Officer

Microsoft Launches New Surface Copilot+ PCs for Business
2026 in Review: Is AI Becoming More of a Management Problem Than a Technology Problem?

Inside XPENG Brand Night: AI Mobility Lands Centre Stage in Dubai

Chinese Cars Are Reshaping the GCC Market, but Resale Value Could Be the Next Battleground
-
 Trending1 year ago
OPPO A6 Pro 5G Review: Reliable Daily Driver
-
 Tech News2 years ago
Denodo Bolsters Executive Team by Hiring Christophe Culine as its Chief Revenue Officer
-
VAR2 years ago
Microsoft Launches New Surface Copilot+ PCs for Business
-
 Automotive2 years ago
AGMC Launches the RIDDARA RD6 High Performance Fully Electric 4×4 Pickup
-
 VAR11 months ago
Huawei Nova 14 Pro Review: Where Camera Excellence Meets Ecosystem Evolution
-
Tech Interviews3 years ago
Navigating the Cybersecurity Landscape in Hybrid Work Environments
-

 Hospitality2 years ago
Gulfood 2025 30th Edition Kicks Off Today, Setting New Benchmarks in F&B Growth and Innovation
-

 Tech News1 year ago
Nothing Launches flagship Nothing Phone (3) and Headphone (1) in theme with the Iconic Museum of the Future in Dubai