 Have a question? +971 56 404 0503

Tech Interviews
RedHat Summit Connect 2025: A discussion with Ed Hoppitt and Adrian Pickering


Exclusive Interview with Ed Hoppitt, EMEA Director – Value Strategy, App and Cloud Platforms at Red Hat & Adrian Pickering, Regional General Manager, MENA & Enterprise Segment Lead for CEMEA at Red Hat
Having worked in global telecom and advised some of the world’s largest enterprises, how have these experiences shaped your approach to developing IT solutions?
Ed: I believe that designing and running operational IT over many years gives one a deep understanding of what truly matters to a customer, especially those partnering with Red Hat. This background enables me to connect with our customers on a level where they feel understood regarding their pain points. Today’s biggest challenge for enterprise IT is building systems that are predictable, replicable, and standardized—yet able to scale effectively.
When you look at what Red Hat offers and how we help enterprises build these solutions, our focus is rooted in leveraging the open source community. We invest in projects that we know will create tremendous value for our enterprise customers, taking those projects upstream, incorporating them into the Red Hat portfolio, and industrializing them into platforms such as OpenShift. Customers choose platforms like OpenShift because they represent best-of-breed choices, delivering stability, reliability, predictability, and scalability. With my operational IT background, I appreciate just how crucial these outcomes are for every customer I speak with.
This year’s Red Hat Summit focuses on curiosity and turning acquired knowledge into practical application. It’s about transforming acquired knowledge into practical applications. Through this, what key message are you hoping to leave with the audience this year?
Adrian: I view curiosity as the foundation for working with our customers to truly understand their vision—where they want to be 18, 24, 30, or even 36 months down the line. It’s about gaining a clear grasp of the business challenges they face or the new markets they wish to serve in the future. We then align our best capabilities to support them along that journey, keeping cost efficiency in mind. This might involve modernizing infrastructure, existing applications, or even building new applications that open doors to entirely new customer segments or solutions.
A great example of this is our work with the Dubai Health Authority, who were on stage at Summit Connect Dubai. When we engaged with them, we took the time to deeply understand the challenges they were trying to address for the citizens and then brought not only our technical products but also our expertise in project management, implementation, training, and knowledge transfer. I’m very proud of our achievements over the years, and I believe that in doing so, we add significant value for our customers.
Ed: To add another perspective, the most compelling conversations I have with customers often begin with discussions that don’t initially center on technology. They start with, “I want to imagine a world where things are different—where you can help me achieve something extraordinary.” For instance, with Red Hat OpenShift AI, we collaborated with the US Department of Veterans Affairs to build a platform that effectively reduced self-harm and suicide rates. By harnessing a platform that could analyze how people called in for assistance—assessing tone and how they described their situations—we helped the teams prioritize who needed immediate care versus who could wait a while for some support.
It’s when someone presents you with such a profound challenge that you really see the immense opportunity we have as an organization. These technology platforms do more than enable business; they help vulnerable people receive the care they need and, ultimately, save lives.
You mentioned that for Red Hat it’s relatively easy to work on new technologies because of the robust support provided by partners and customers alike. Can you elaborate on just how important those relationships are for your team?
Adrian: The point is that, while we are proud of the solutions we deliver through Red Hat, many integrated solutions require components from multiple software vendors. Our partners and integrators are essential because they bring together the various components needed to deliver, implement, and support these complex solutions. In many regions, especially where we serve multiple countries, these partners offer additional scale and reach, often accessing markets where Red Hat might not have a direct footprint. This collaboration is a critical part of why we work so closely with our partners.
Ed: Another significant benefit of having partners is that it allows Red Hat to concentrate on what we do best. We aren’t trying to solve every aspect of the IT enterprise supply chain. Instead, we work with best-of-breed partners who focus on their own areas of expertise. This means that Adrian’s teams and others in our region can focus on delivering core value to our customers. As we saw on stage, one of the Middle East’s largest banking group was very ahead of the curve in its approach to virtualisation and modernisation. These partners enable us to help customers execute at scale and with credibility. My background in operational IT tells me that although the journey is rarely smooth, having a trusted team and partners makes all the difference.
In today’s enterprise technology landscape, where hybrid and multi-cloud environments are the norm, how is Red Hat helping customers unlock the potential of open source technologies?
Ed: For me, the hybrid and multi-cloud narrative is essentially about providing customers with standardization. Some customers might say that they’re on a path toward data center consolidation, or are committed to a single hypervisor, or even a multi-cloud strategy. But once they embrace a hybrid approach, the underlying message is that they require a globally consistent management and operational platform—one that spans multiple cloud providers, private data centers, or even edge environments.
How do we achieve this consistency in an open source manner? When you’re a proprietary company, control is tight. With our strategy, we offer customers open choice—where to run their platform and which workloads to deploy on top of it. In essence, our approach empowers customers by eliminating the risks of siloed, locked-in solutions. This freedom enables businesses to continuously ask, “What should I run, and where and how should I run it?” They consider the portfolio of applications, evaluate whether low-latency edge deployment is needed—as is common for a supermarket loyalty system—or whether a core data center or public cloud deployment makes sense. The operational “how” is addressed by determining whether to run on a container platform, a virtual machine platform, or an alternative setup. Finally, the “why” ties back to ensuring the overall solution aligns with the customer’s cost and business objectives.
Ultimately, our focus is on answering one simple question for the customer: “What should I run, and where, how, and why should I run it?” This encapsulates our commitment to providing both choice and clarity in today’s complex IT environment.
Adrian: I find it quite interesting how that perspective plays out regionally. While we enable customers to run applications on our platforms, major players like Google are also part of the ecosystem. Particularly in Europe, where there is current uncertainty, many governments are questioning whether their sovereign data should reside on a cloud service originating from the U.S. Without diving too deeply into politics, this debate is prompting customers to consider alternative cloud options. For example, when running OpenShift on-premises or on a cloud provided by a specific country, it becomes easier to migrate to a new provider if necessary. This is an evolving discussion, especially in Europe, and it’s something that might expand beyond political cycles in the future.
Ed: Exactly. In Europe, the focus remains on providing choice. With open source technology, we sidestep many political concerns because of the transparency it offers. Customers can inspect the code to see that there are no hidden backdoors or data issues. Consequently, building a sovereign solution using Red Hat technology has gained significant traction. Both governments and organizations are increasingly interested in retaining full control over their data.
It seems that customers also desire a degree of freedom with their platforms; they want to ensure that no external party completely controls their systems. How does Red Hat provide this assurance of complete control?
Ed: Customers can deploy our platform in either of two ways. If they run it in their own data center, on-premises. In this case, they obtain full access—they have the code, the platform, all the necessary certificates, and they manage it themselves. In contrast, if they decide to run the platform on one of the hyperscalers, while the underlying compute infrastructure is provided by the hyperscaler, the platform—the layer where the data sits and the applications operate—remains in the open source domain. Therefore, even in these cases, customers retain the ability to influence, control, and understand what happens with their data and applications. And when it comes down to it, every country and organization will make its own decisions, but our consistent message remains: our focus is on choice. Whether a company decides to run its workloads privately, on the public cloud, or at the edge, we ensure that they have the consistent tools and platforms to do so efficiently.
Adrian: That’s exactly right. We have long maintained a commitment to enabling customers to choose the open hybrid cloud. Whether a customer opts for a sovereign cloud, a hyperscaler, or their own private cloud, our core mission is to grant them the freedom to choose and to operate in a simple, consistent, and controlled manner.
Where do you see the enterprise technology landscape heading in the next three to five years?
Ed: I believe that over the next three to five years, we will witness an increasingly consolidated effort to eliminate complexity within IT organizations. Over the last decade, IT has excelled in building silos—if anything, it’s been very effective at doing so. However, with the advent of AI, these separate silos of infrastructure and data are becoming even more problematic. When your data resides in multiple unconnected silos, it becomes extremely challenging to aggregate and leverage it for AI-based insights.
In a recent discussion with a financial services industry leader, the focus was increasingly on ensuring access to all their data, democratizing it internally, and enabling AI-driven querying. This represents a paradigm shift, as data today typically lives within isolated applications. In an AI-integrated world, breaking down these silos is critical. I foresee that one of the most significant developments in the near future—driven by AI—will be the democratization of data access across organizations.
Adrian: I concur. From a regional perspective, we might be a couple of years behind more developed markets like Europe or the U.S. For instance, we are still in the earlier stages of transitioning to the cloud. In the UAE and other regions, sovereign cloud providers are just beginning to expand their offerings. Financial institutions, aviation companies, and others are now starting to embrace the cloud more aggressively than they have in the past four or five years.
Ed: Another nuance here involves what we’re exploring with Granite and small language models. Often, to help Adrian’s customers manage support tickets, you don’t need a language model that knows Shakespeare by heart. Large language models typically contain vast amounts of data, much of which isn’t directly relevant to a given enterprise. Our focus has thus shifted to a choice: do we help organizations harness AI by asking questions of data they couldn’t access before, or do we tailor solutions with smaller language models designed to address specific enterprise challenges?
One notable example was how we applied a tailored small language model within Red Hat to support our own teams in resolving support tickets. This initiative not only saved millions of dollars but also significantly enhanced customer experience and sped up response times. Over time, while large language models have captured much of the buzz, I suspect we will see rapid adoption of small, specialized language models tailored for specific functions.






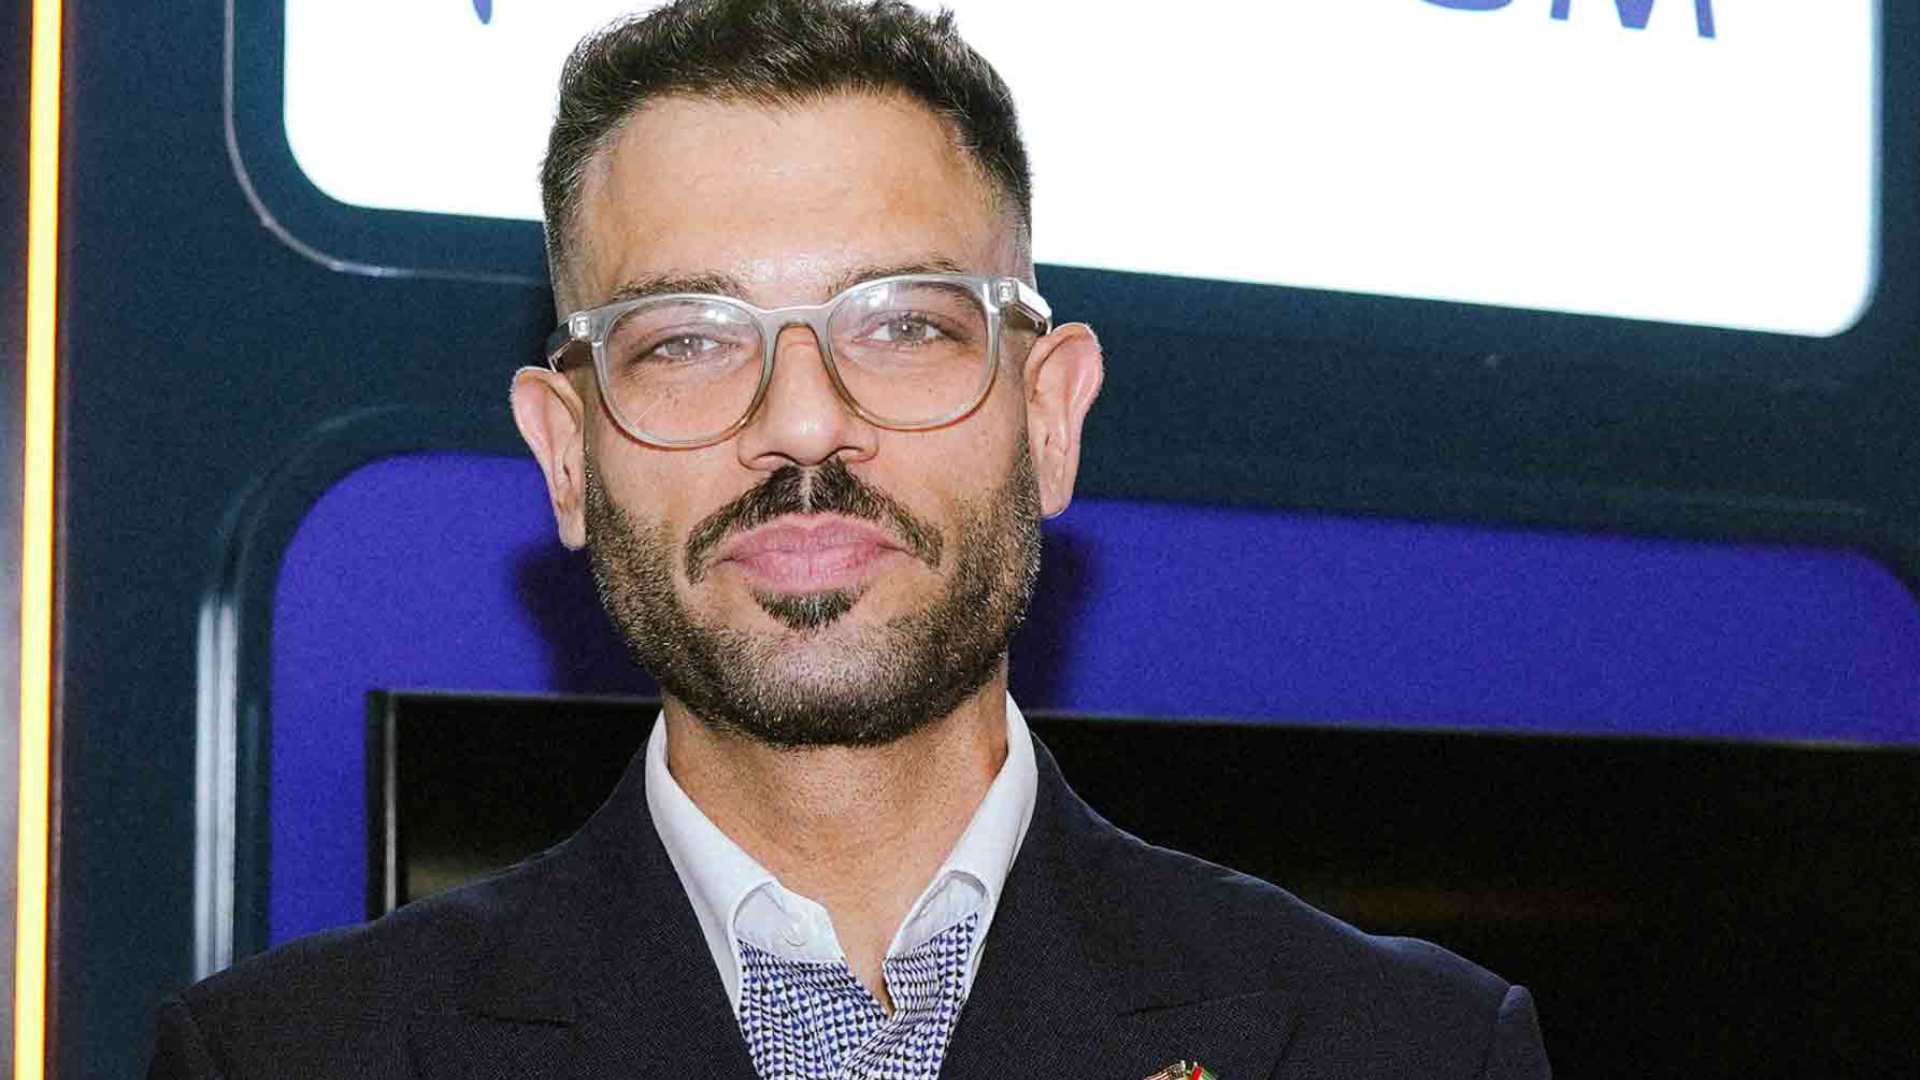
Exclusive interview with Shadi Hatoum, Regional Director MEA at Tealium
The UAE is moving quickly from AI experimentation to deployment. What do you think will determine which organizations actually turn adoption into measurable business value?
The organizations that create measurable value will be those that connect AI to a clearly defined business decision, then give it the right data and operating model to support that decision.
The UAE has already built significant momentum. Boston Consulting Group found that 42% of UAE organizations qualify as AI Leaders, while 37% have reached the scaling stage of AI maturity. The next test is whether that maturity translates into sustained outcomes.
Deploying a model is not the same as changing how a business operates. AI needs trusted, consented, and real-time context around customer identity, behavior, intent, and journey stage. It also needs clear ownership, measurable objectives, and teams that understand how to use the output.
From my perspective, data readiness and organizational adoption will be the two biggest differentiators. The organizations that can put reliable context in front of AI at the moment of decision, and embed the resulting insight into daily workflows, will be best positioned to turn adoption into measurable value.
How much of the current gap between AI ambition and AI impact comes down to fragmented or outdated customer data?
A significant part of the gap comes down to data readiness, although technology alone is not the whole answer. Most organizations do not lack data. Their challenge is that the data is fragmented, difficult to interpret, or unavailable when a decision needs to be made.
Historical data provides useful depth, but AI also needs data in motion. It needs to understand what a customer is doing now, what has changed, what the customer has consented to, and whether the signal belongs to the correct individual or account.
Tealium’s Future of Customer Data research found that 88% of organizations consider real-time data important to achieving business objectives. That is important because an AI system working from yesterday’s profile may produce a technically valid recommendation that is no longer relevant.
The real opportunity is to create a trusted context layer that connects identity, behavior, consent, and intent, then makes that context available to models and decisioning systems while the customer interaction is still taking place.
Does agentic AI create a new governance problem for enterprises, particularly when agents are acting on customer data without constant human intervention?
Agentic AI does not make the principles of governance entirely new, but it raises the stakes and increases the speed at which controls need to operate. When an AI agent can move from recommendation to action, governance can no longer be treated only as a periodic policy or review exercise. It needs to operate within the data flow and decision process itself.
Enterprises need clear controls over which data an agent can access, the purpose for which it can use that data, how identity and consent are verified, which actions it is authorized to take, and when a person must review or approve the outcome.
The key question is not only whether an agent can access a piece of customer data. It is whether the agent should use that data for this customer, for this purpose, at this moment.
That requires trusted data, current consent, auditability, defined action limits, and clear escalation paths. As autonomy increases, accountability needs to become more precise, not less.
Which sectors in the Middle East do you think are furthest ahead in using real-time customer data and AI together effectively?
From my experience across the region, telecommunications and travel, hospitality, and tourism are among the most active and promising sectors because they generate frequent customer signals and have a clear need to respond in the moment.
In a recent discussion with the Chief Commercial Officer of a major telecom operator in the region, we talked about growth as filling a bucket while also stopping the leaks. Acquisition fills the top, but poor service, irrelevant engagement, and unresolved friction allow value to escape through churn. Sustainable growth requires both attracting new customers and protecting the loyal customer base already in the bucket.
This is where AI-supported decisioning can create real value. Trusted, consented, real-time behavioral data can help an operator recognize changes in usage, service issues, digital engagement, and signs of churn. The next best action may be to resolve a problem, recommend a more suitable plan, position a bespoke package at the right time, or avoid making an offer when the customer first needs support.
The objective is not to push more offers. It is to improve relevance and timing. That can support retention, strengthen loyalty, and create opportunities to grow average revenue per user, or ARPU, by responding to what the customer needs in that moment.
Travel, hospitality, and tourism have a similarly strong opportunity. The customer journey moves from inspiration and research to booking, arrival, the in-destination experience, and loyalty. Each stage creates different needs. A traveler facing disruption needs assistance, while a guest already at a destination may value a timely, personalized experience or service.
These sectors show why hyper-personalization at scale depends on trusted, consented behavioral data in motion. The value comes from giving AI initiatives the current context they need to choose the next best action for that specific moment.
At AI Everything Abu Dhabi 2026, what are the biggest changes you are seeing in the conversations enterprises are having compared with a year or two ago?
The biggest change is that enterprises are no longer asking whether they should adopt AI. They are asking how to move it into production, connect it to measurable outcomes, and govern it at scale.
A year or two ago, many conversations centered on experimentation and individual use cases. Today, the questions are more operational. Leaders want to understand how AI will work with their existing data, how agents will receive current customer context, how decisions will be controlled, and how value will be measured beyond a successful pilot.
I am also hearing much more emphasis on adoption. Organizations recognize that a model does not create value by itself. Teams need clear use cases, practical training, shared measures of success, and confidence in the data behind the recommendation.
The conversation has therefore moved from AI capability to AI readiness. That includes the quality of the data foundation, the governance around it, the ability to make decisions in real time, and the people and processes required to turn those decisions into action. For me, that is a sign that the market is becoming more mature and more focused on sustainable business impact.
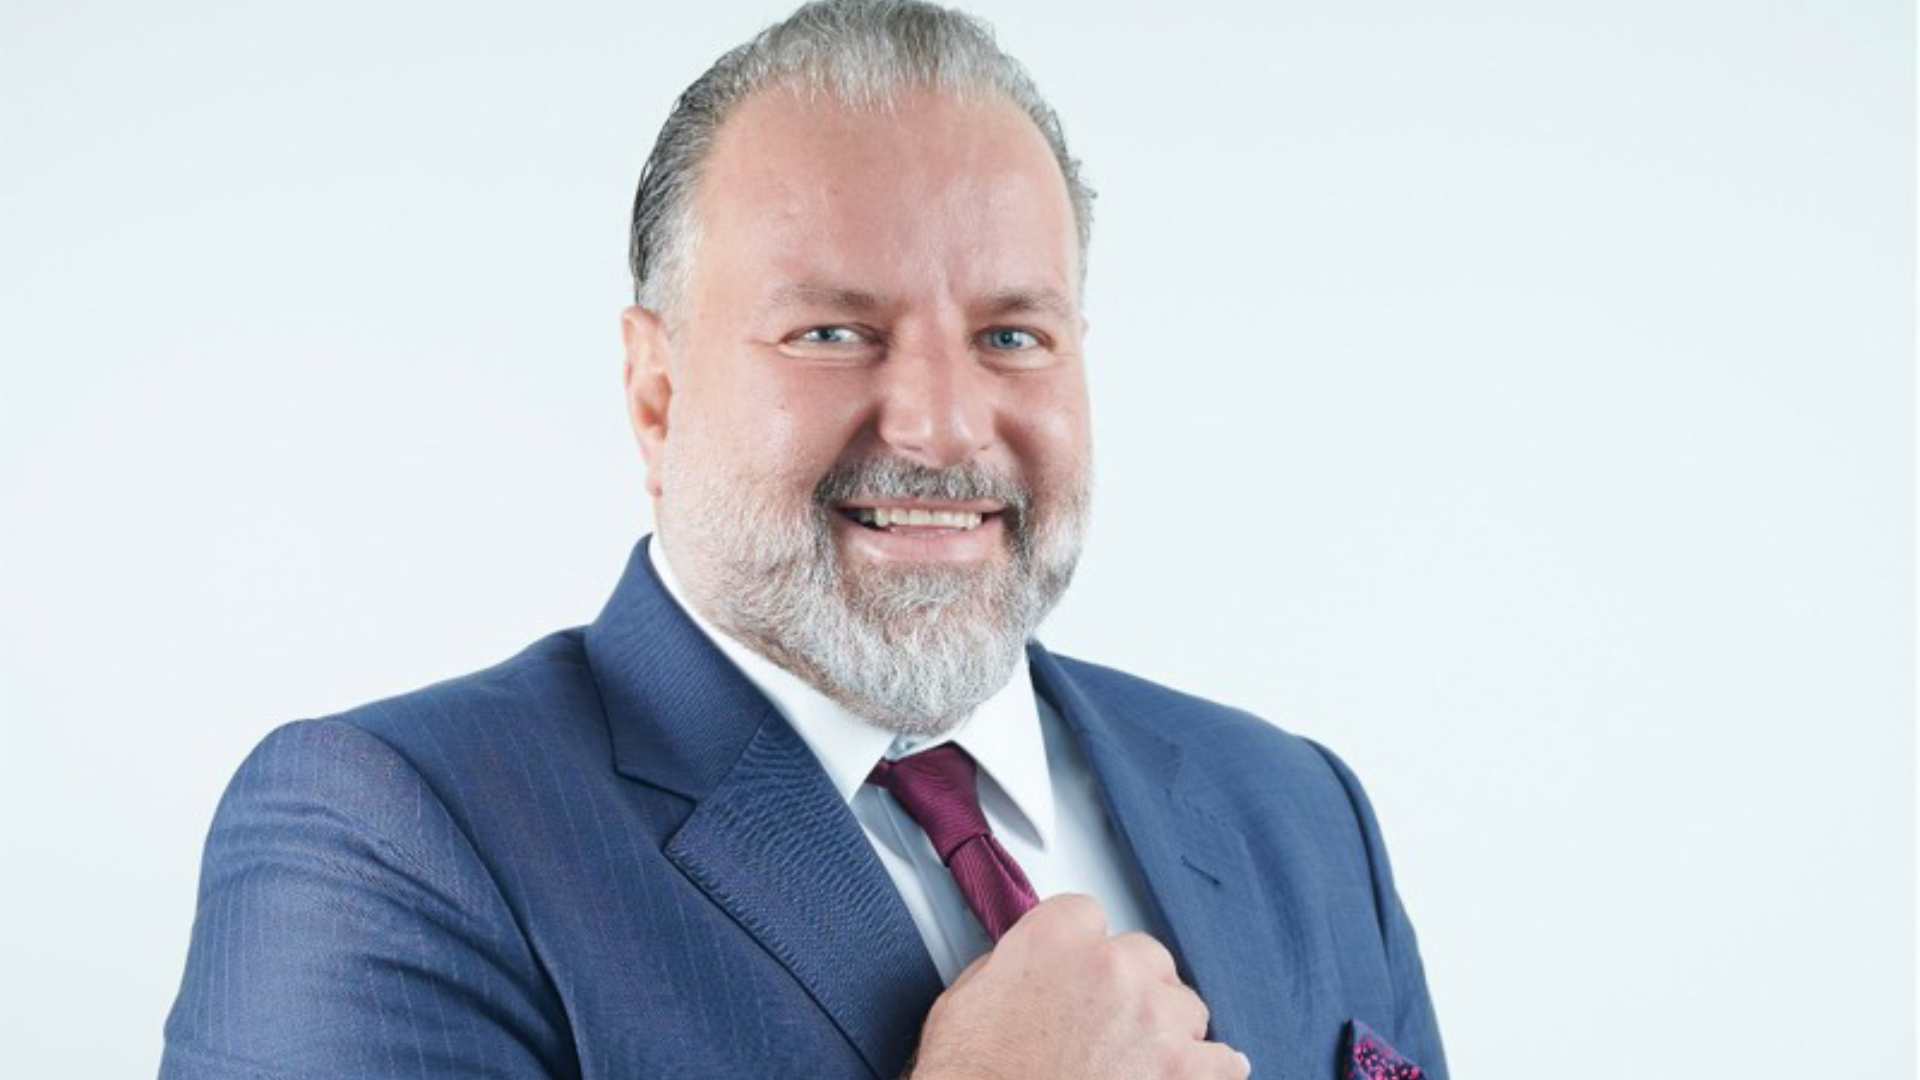
Exclsuive interview with Fady Richmany, Corporate Vice President and General Manager, Emerging Markets at Commvault
Integrated Media is at GISEC Global Dubai 2026 with Fady Richmany, Corporate Vice President and General Manager, Emerging Markets at Commvault
How is AI changing the attack surface for organizations in the region?
AI is crucial for digital transformation, so we are not debating the importance of AI. I think the UAE is one of the most advanced countries when it comes to adopting technology. The Dubai Government has also announced plans to use agentic AI extensively in the coming years
However, AI comes with a significant amount of data and introduces new types of identities. We are no longer dealing only with human identities but are increasingly dealing with robotic and AI-agent identities that can access data and systems. This creates additional complexity and consequences from an identity and security perspective.
At the same time, AI-powered attacks are another major concern. In the past, a hacker typically needed to be highly technical. Today, with AI, launching sophisticated attacks can become much simpler.
So, AI is important, but it needs to be utilized properly and governed effectively. There needs to be a balance when organizations and large enterprises adopt these technologies.
Why are threat actors increasingly targeting backup and recovery environments?
Backup and recovery are the last line of defence.
When a company is compromised, one of the first things it needs to do is access its backups to recover its data and operations. Hackers understand this. If they want their attacks to be effective, they also need to target the backup environment.
This is where companies like ours, along with many others in the industry, play an important role in making sure that backups remain clean, protected, and safe so organizations can recover when an incident occurs.
How does identity management need to evolve as AI agents and autonomous workloads multiply?
Agentic AI is putting additional pressure on IT because it is creating many robotic identities.
We have also seen attacks where AI has been used with little or no human intervention. This creates an additional security burden, which means these identities need to be properly protected.
Our approach focuses on the recovery side. Organizations need to use the appropriate security technologies available in the market to protect their environments and ensure that the right identities have access to the right resources.
But we also need to address what happens when an identity is compromised. How do you recover the environment? How do you recover the identity infrastructure? That is becoming a very important topic.
What does Cloud Unity offer beyond separate point solutions?
Cloud Unity brings together identity, security, and operational resilience. We combine people and processes and work closely with many of the leading security technology partners in the market.
We integrate information from different technologies and provide identity resiliency to help protect organizations from both sides of the problem.
We also have something called ResOps, or Resiliency Operations. It is a methodology for how organizations should operate. We believe organizations need to educate their people, keep them aware, and make sure everyone understands their role during a crisis. They also need to modernize their processes.
All of this comes together to make sure the environment remains resilient and productive. And this is not a one-time exercise but has been continuously tested – time and again.
How does ResOps help organizations move from reactive security to a more measurable and proactive approach?
In the olden days, we used what we called backup drills. This is particularly common in banking and government, where people would come together every quarter and check whether the backup was working.
But that approach is no longer enough.
Recovering data is not simply about recovering the information. During a cyberattack, you need to recover clean data and ensure that the environment you are restoring is safe. That means organizations need continuous testing. You have to align people, processes, and technology and make testing an ongoing activity.
When a compromise happens, everyone needs to know their role – Who has access? What are the steps that need to be followed? Who is responsible for each action? The ultimate objective is to be able to recover a clean copy of the data and get the organization back into operation as quickly and safely as possible.
What will the new Center of Excellence in Abu Dhabi focus on, and how will it support the UAE’s digital transformation goals?
One of our strategies is to align closely with local authorities, and work together with them. We work very closely with the UAE Cyber Security Council and have developed this initiative together with them.
The purpose of the Center of Excellence is to bring innovation to the region. It will be a center for innovation, with R&D and technology development taking place in the region. It will also be a center for developing local talent. We are partnering with universities and aim to train young Emiratis in areas such as cyber resilience and cyber defense. It will also be a center for awareness.
I would quote what Dr. Mohamed Al Kuwaiti said- the responsibility for cyber defense does not rely on one technology, one individual, or one government. It requires the entire community to work together to fight cyber threats. That is the purpose of the center. It is to bring all these elements together, support the cybersecurity community, and give back to the region. We want to create awareness, talent, and innovation.
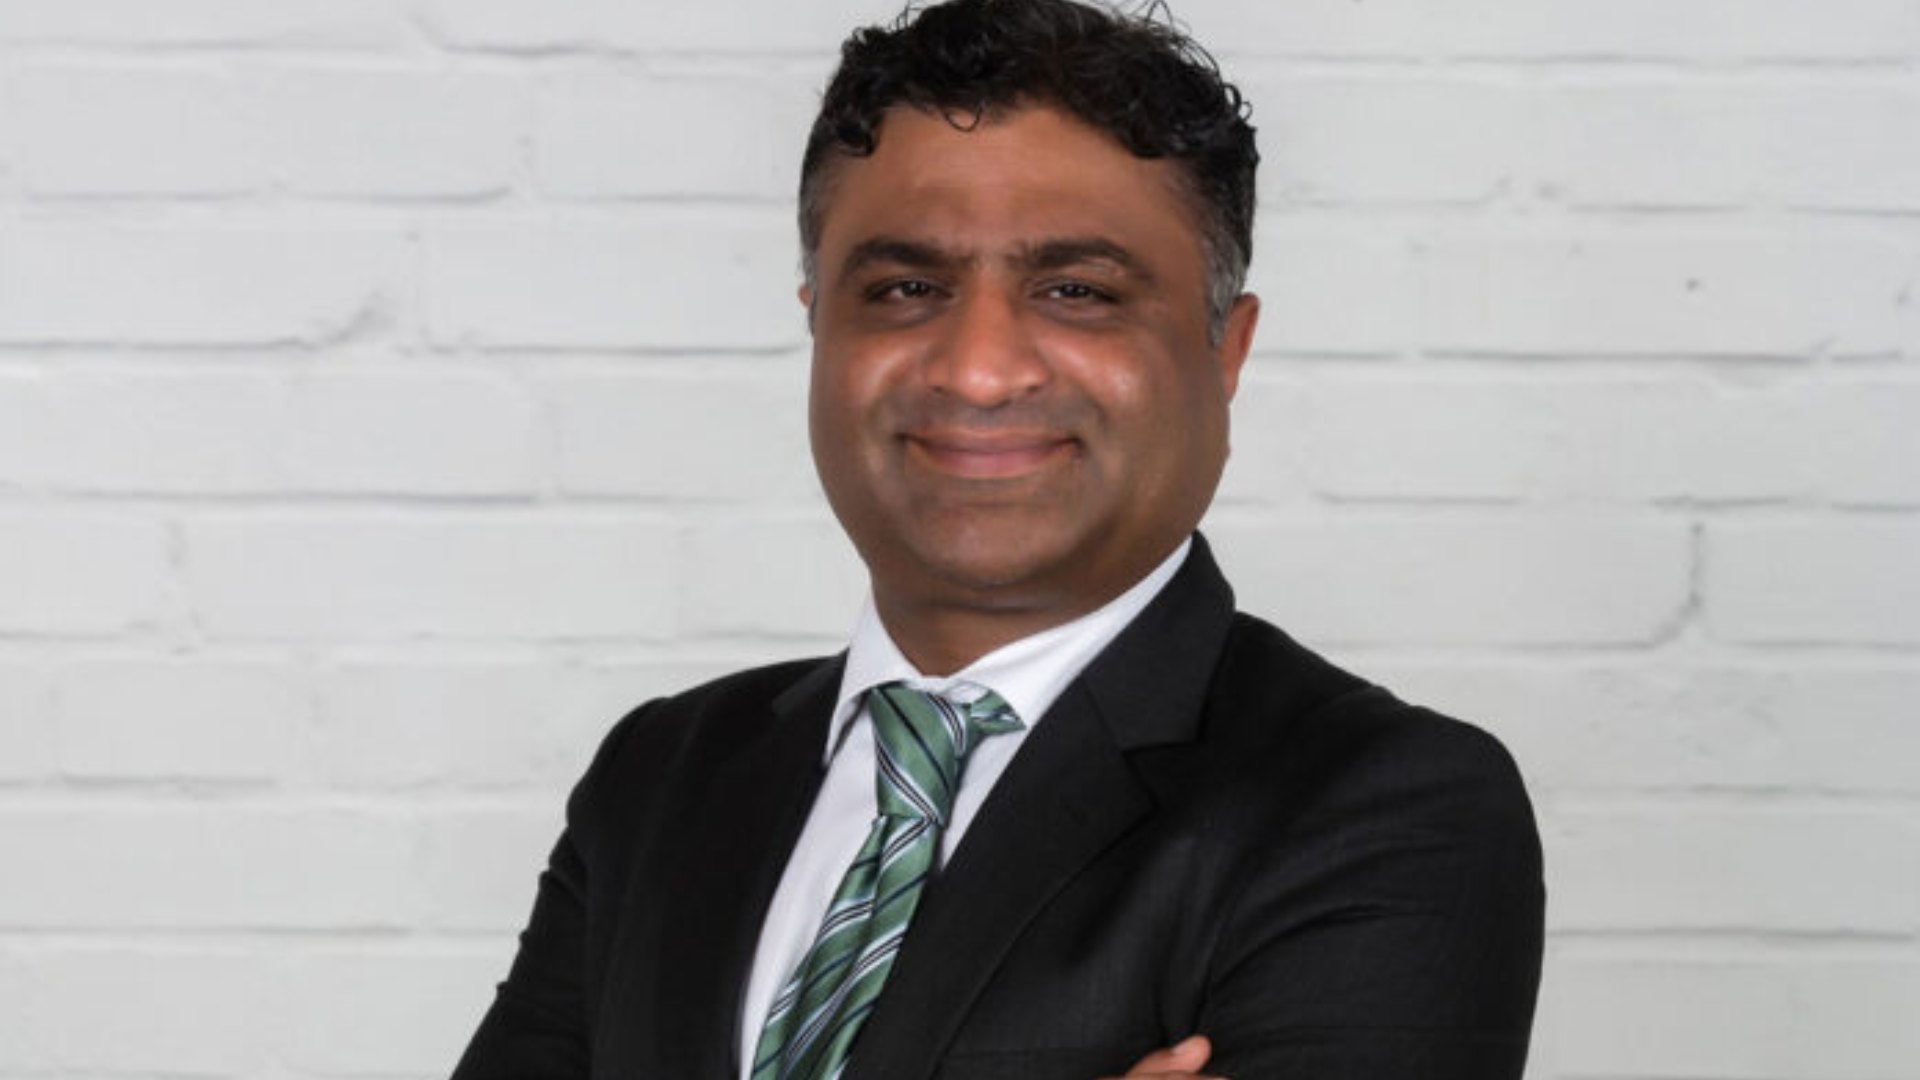
Exclusive interview with Bilal Baig, Vice President, Solutions Engineering, Trend Micro
What is Trend Micro showcasing at GISEC Global 2026, and how does it reflect the shift towards proactive, AI-powered cyber risk management?
We are highlighting our unified cybersecurity platform, Trend Vision One, which is designed as a proactive security platform.
AI has shifted how organisations, governments and agencies respond to threats. It is no longer enough to take a reactive approach. Security needs to become proactive, particularly given the speed at which AI is developing.
We are using AI in two ways. First, we are using AI internally within the platform to identify vulnerabilities. Second, we are using AI to protect our customers.
At GISEC, we are showcasing agentic SIEM, agentic SOAR, XDR capabilities and our full-stack AI security platform. We are also highlighting new developments in AI security, including how AI can help protect against vulnerabilities and zero-day attacks.
How has Trend Micro evolved in both using AI for cybersecurity and securing AI systems themselves?
AI has increased the speed at which organisations can move into production. At the same time, both defenders and attackers now have access to AI. The key question is how organisations manage that risk and how quickly they can protect customers and predict an attack before it becomes a breach.
We created Cybertron, an industry-first cybersecurity LLM, and we also work with frontier AI providers including Anthropic, OpenAI and Microsoft. We use frontier AI to consume vulnerability information, while our customers have access to our broader AI security capabilities.
We are now moving into the agentic AI era, where AI agents can make decisions on behalf of humans. These agents can access systems, emulate human behaviour and perform tasks independently.
For us, agentic AI security comes down to four key areas: visibility, observability, governance and response.
Visibility means understanding what is happening. Observability goes a step further by understanding what an action performed by an AI agent could cause. Governance determines how those agents should be controlled, while response is about deciding what action to take.
What new security and governance challenges arise as agentic AI moves from experimentation to enterprise deployment?
One of the biggest questions is whether an agentic AI system should be treated like a human identity or like software.
A software system needs updates, patches and maintenance. A human has an identity, a job and defined responsibilities. Agentic AI combines elements of both.
Organisations therefore need to give AI agents an identity, establish guardrails around what they can do and ensure that someone within the governance structure is responsible for their actions.
If an agent is given additional responsibilities, organisations need to understand how those permissions are managed and eventually removed when they are no longer required.
In an agentic AI environment, every communication and action needs to be considered within a governance framework. Organisations need to look at every interaction, understand its potential outcome and decide whether an action should be allowed to proceed or stopped.
What does the rise of autonomous or rogue AI agents mean for cybersecurity?
We are entering a world where rogue AI agents can become highly sophisticated systems. This means security cannot focus only on whether the underlying AI model is secure. Organisations also need to examine the actions those models are performing and whether those actions could create a cybersecurity problem.
The attack surface is now changing in terms of both scale and sophistication. Attackers have AI capabilities that can help them launch sophisticated attacks much faster.
This means organisations need AI on the defensive side as well. Security solutions need to match that speed and sophistication while ensuring that governance frameworks prevent malicious outcomes.
How should organisations manage the growing number of vulnerabilities identified by AI?
AI and frontier models can identify vulnerabilities that may not have been visible previously. An organisation that once had to manage 30 or 40 patches could suddenly face thousands.
It is not realistic to address every vulnerability in the same way. Organisations need to prioritise based on the risk and importance of their environment.
They need to identify which vulnerabilities are most important for their particular environment rather than simply looking at a vulnerability’s CVE score.
This is where cyber risk exposure management becomes important. Organisations need to understand the risk, the asset and the identity involved, and then decide which security gaps are most important to close.
How is the UAE’s cyber threat landscape changing as AI adoption and digital transformation accelerate?
The UAE is at the forefront of AI transformation. We are seeing multiple initiatives from the UAE Government, including AI training for government employees, government-focused AI initiatives and the introduction of AI education in schools.
There are already AI systems operating within government, so the digital transformation of AI in the UAE is moving forward rapidly.
Our focus is on helping secure that transformation. As AI systems become more interconnected and increasingly make decisions, the attack surface becomes more complicated.
A layered security approach is therefore important, from the large language model and API access through to the decision-making processes of AI agents, while monitoring for malicious activity.
What should organisations consider around security controls and data sovereignty as they expand their cloud and AI environments?
There is sometimes a misconception that moving to the cloud automatically means an organisation is secure. When cloud computing emerged, we often talked about security as a shared responsibility.
The exposure changes as organisations move from on-premises environments to the cloud and then into AI. The same threat can look very different across these environments.
Organisations need to consider where their assets and identities are located and how they will manage security across these different layers.
For highly sensitive environments, including air-gapped networks and systems involving critical data sovereignty, security may need to remain on-premises. In some national security environments, data cannot be processed outside the country.
Trend Micro has Vision One Sovereign and Private Cloud, which extends our AI cybersecurity unified platform to air-gapped and sovereign environments, with a focus on data sovereignty, localisation and air-gapped deployments.
What role does government-industry collaboration play in strengthening national cybersecurity preparedness and resilience?
Government-industry collaboration is extremely important. Working with organisations such as the Cybersecurity Council, national CERTs and government security services brings together different perspectives.
As governments move towards greater use of AI, industry can help secure that journey while governments provide the regulations and governance frameworks needed to manage these systems.
Without close collaboration, it becomes difficult to create policies that reflect what is actually happening in the private sector.
The objective should be to support innovation without overlooking cybersecurity. Technology is developing extremely quickly, particularly AI, so cybersecurity needs to be considered alongside that innovation.
Government and the private sector need to work together to make sure that while organisations remain at the forefront of technological development, they do not overlook the cybersecurity implications.

20 YEARS OF MEMORIES, DUBAI. AND WE’RE JUST GETTING STARTED. MAJESTIC HOTELS OFFERS EXCLUSIVE 20% ANNIVERSARY PROMO

Al Jaddaf Rotana Appoints Hekmat Amer as Complex Director of Sales & Marketing

GHA DISCOVERY launches global giveaway with D$50,000 in prizes and Lifetime Titanium Memberships


-
 Trending12 months ago
OPPO A6 Pro 5G Review: Reliable Daily Driver
-

 Tech News2 years ago
Denodo Bolsters Executive Team by Hiring Christophe Culine as its Chief Revenue Officer
-
 VAR1 year ago
Microsoft Launches New Surface Copilot+ PCs for Business
-
 Automotive2 years ago
AGMC Launches the RIDDARA RD6 High Performance Fully Electric 4×4 Pickup
-
Tech Interviews3 years ago
Navigating the Cybersecurity Landscape in Hybrid Work Environments
-

 Hospitality2 years ago
Gulfood 2025 30th Edition Kicks Off Today, Setting New Benchmarks in F&B Growth and Innovation
-

 Tech News1 year ago
Nothing Launches flagship Nothing Phone (3) and Headphone (1) in theme with the Iconic Museum of the Future in Dubai
-
 VAR2 years ago
Samsung Galaxy Z Fold6 vs Google Pixel 9 Pro Fold: Clash Of The Folding Phenoms