 Have a question? +971 56 404 0503

Tech News
IBM Sets the Course to Build World’s First Large-Scale, Fault-Tolerant Quantum Computer at New IBM Quantum Data Center


IBM unveiled its path to build the world’s first large-scale, fault-tolerant quantum computer, setting the stage for practical and scalable quantum computing.
Delivered by 2029, IBM Quantum Starling will be built in a new IBM Quantum Data Center in Poughkeepsie, New York and is expected to perform 20,000 times more operations than today’s quantum computers. To represent the computational state of an IBM Starling would require the memory of more than a quindecillion (10^48) of the world’s most powerful supercomputers. With Starling, users will be able to fully explore the complexity of its quantum states, which are beyond the limited properties able to be accessed by current quantum computers.
IBM, which already operates a large, global fleet of quantum computers, is releasing a new Quantum Roadmap that outlines its plans to build out a practical, fault-tolerant quantum computer.
“IBM is charting the next frontier in quantum computing,” said Arvind Krishna, Chairman and CEO, IBM. “Our expertise across mathematics, physics, and engineering is paving the way for a large-scale, fault-tolerant quantum computer — one that will solve real-world challenges and unlock immense possibilities for business.”
A large-scale, fault-tolerant quantum computer with hundreds or thousands of logical qubits could run hundreds of millions to billions of operations, which could accelerate time and cost efficiencies in fields such as drug development, materials discovery, chemistry, and optimization.
Starling will be able to access the computational power required for these problems by running 100 million quantum operations using 200 logical qubits. It will be the foundation for IBM Quantum Blue Jay, which will be capable of executing 1 billion quantum operations over 2,000 logical qubits.
A logical qubit is a unit of an error-corrected quantum computer tasked with storing one qubit’s worth of quantum information. It is made from multiple physical qubits working together to store this information and monitor each other for errors.
Like classical computers, quantum computers need to be error corrected to run large workloads without faults. To do so, clusters of physical qubits are used to create a smaller number of logical qubits with lower error rates than the underlying physical qubits. Logical qubit error rates are suppressed exponentially with the size of the cluster, enabling them to run greater numbers of operations.
Creating increasing numbers of logical qubits capable of executing quantum circuits, with as few physical qubits as possible, is critical to quantum computing at scale. Until today, a clear path to building such a fault-tolerant system without unrealistic engineering overhead has not been published.
The Path to Large-Scale Fault Tolerance
The success of executing an efficient fault-tolerant architecture is dependent on the choice of its error-correcting code, and how the system is designed and built to enable this code to scale.
Alternative and previous gold-standard, error-correcting codes present fundamental engineering challenges. To scale, they would require an unfeasible number of physical qubits to create enough logical qubits to perform complex operations – necessitating impractical amounts of infrastructure and control electronics. This renders them unlikely to be able to be implemented beyond small-scale experiments and devices.
A practical, large-scale, fault-tolerant quantum computer requires an architecture that is:
- Fault-tolerant to suppress enough errors for useful algorithms to succeed.
- Able to prepare and measure logical qubits through computation.
- Capable of applying universal instructions to these logical qubits.
- Able to decode measurements from logical qubits in real-time and can alter subsequent instructions.
- Modular to scale to hundreds or thousands of logical qubits to run more complex algorithms.
- Efficient enough to execute meaningful algorithms with realistic physical resources, such as energy and infrastructure.
Today, IBM is introducing two new technical papers that detail how it will solve the above criteria to build a large-scale, fault-tolerant architecture.
The first paper unveils how such a system will process instructions and run operations effectively with qLDPC codes. This work builds on a groundbreaking approach to error correction featured on the cover of Nature that introduced quantum low-density parity check (qLDPC) codes. This code drastically reduces the number of physical qubits needed for error correction and cuts required overhead by approximately 90 percent, compared to other leading codes. Additionally, it lays out the resources required to reliably run large-scale quantum programs to prove the efficiency of such an architecture over others.
The second paper describes how to efficiently decode the information from the physical qubits and charts a path to identify and correct errors in real-time with conventional computing resources.
From Roadmap to Reality
The new IBM Quantum Roadmap outlines the key technology milestones that will demonstrate and execute the criteria for fault tolerance. Each new processor in the roadmap addresses specific challenges to build quantum systems that are modular, scalable, and error-corrected:
- IBM Quantum Loon, expected in 2025, is designed to test architecture components for the qLDPC code, including “C-couplers” that connect qubits over longer distances within the same chip.
- IBM Quantum Kookaburra, expected in 2026, will be IBM’s first modular processor designed to store and process encoded information. It will combine quantum memory with logic operations — the basic building block for scaling fault-tolerant systems beyond a single chip.
- IBM Quantum Cockatoo, expected in 2027, will entangle two Kookaburra modules using “L-couplers.” This architecture will link quantum chips together like nodes in a larger system, avoiding the need to build impractically large chips.
Together, these advancements are being designed to culminate in Starling in 2029.






Tech News
Cloudera and Mistral Partner to Bring Specialized, Sovereign Intelligence to Enterprise Data
Cloudera, the only company bringing AI to data anywhere, and Mistral, a global frontier AI lab, today announced a landmark strategic partnership to bring secure, sovereign AI directly to enterprise data wherever it resides.
Cloudera and Mistral will combine Cloudera’s hybrid data and AI platform with Mistral’s sovereign AI models to give enterprises a secure path to build, customize, and run AI using their own private data. The collaboration will enable organizations to bring intelligence directly to their data across cloud, on-premises, edge, sovereign, and air-gapped environments—without requiring sensitive information to leave their control.
For enterprises managing the world’s largest and most sensitive data estates, this approach provides greater control, choice, and flexibility over how and where AI runs. Organizations can run inference privately, customize AI using proprietary data, and deploy AI applications within their existing security and governance boundaries, while gaining greater control over the economics of AI at scale.
“Enterprise AI is entering a new phase where organizations need more than access to powerful models, they need the freedom to unlock specialized intelligence using their data, on their terms,” said Abhas Ricky, Chief Business Officer & GM, Applied AI at Cloudera. “Together with Mistral, we are giving enterprises the ability to run AI where their data lives, customize it with their own intellectual property, and maintain control over their data, infrastructure, and economics. That combination of intelligence and control is essential to moving AI from experimentation into production.”
Bringing Intelligence to the Data
For enterprises operating in highly regulated and data-intensive industries, moving sensitive or proprietary information to external AI services can introduce regulatory, security, and operational challenges.
Cloudera and Mistral are addressing these challenges by bringing secure, sovereign AI directly to the enterprise data perimeter.
Mistral’s suite of frontier models and tools will be integrated with Cloudera’s hybrid data and AI platform, enabling customers to run their own custom AI models and applications across 30 exabytes of data. Enterprises will have the deployment flexibility across public, private, on-premises, and fully air-gapped environments, while maintaining consistent governance and control over their context.
The partnership will span Mistral’s broad portfolio of frontier AI models and tools, including reasoning, chat, coding, document intelligence, and voice, giving Cloudera customers greater choice in how they apply AI to their enterprise data.
By enabling organizations to run inference within their own environments, the collaboration also gives customers greater flexibility over the economics of AI. Enterprises can choose the deployment model and infrastructure that best fit their workloads rather than depending exclusively on public API consumption models as AI usage scales.
From Private Inference to Proprietary Intelligence
Through the integration of Mistral Forge, a system for enterprises to build frontier-grade AI models grounded in their proprietary knowledge, organizations utilizing Cloudera’s platform will be able to customize and train models against large volumes of private enterprise data within controlled environments. For enterprises with petabytes of proprietary information, this creates an opportunity to transform decades of institutional data and domain expertise into differentiated AI while maintaining ownership and sovereignty over both the data and resulting intelligence.
Developers and practitioners will also be able to securely build AI-powered experiences using private enterprise data within local environments—from conversational access to governed data to AI-assisted software development and agentic workflows—without exposing sensitive business context or intellectual property to external environments.
Cloudera and Mistral also intend to collaborate on the next generation of AI at the edge, bringing increasingly capable inference closer to where enterprise data is created. This will enable organizations to explore intelligent applications across disconnected, latency-sensitive and resource-constrained environments where relying on centralized cloud infrastructure is not practical.
“Our mission is to make frontier AI available to enterprises without requiring them to give up control over their data, infrastructure, or intellectual property,” said Kamal Brar, SVP of Partnerships and Alliances at Mistral. “Cloudera manages some of the world’s most valuable enterprise data estates, making this partnership a powerful opportunity to bring our technology directly to where that data lives. Together, we can give customers the ability to build AI that reflects their own data and expertise and deploy it securely wherever their business requires.”
Expanding Choice for Enterprise AI
The partnership also expands the Cloudera Enterprise AI Ecosystem, through which Cloudera works with leading AI models, infrastructure, application, and technology providers to give customers flexibility in how they build and deploy enterprise AI.
Mistral adds a significant new dimension to that ecosystem by enabling customers to access and customize its models and AI capabilities directly alongside their governed enterprise data. The partnership reinforces both Cloudera’s and Mistral’s commitment to an open approach to enterprise AI, giving customers choice across models, infrastructure, and deployment environments rather than locking their data or AI strategy into a single technology stack.
The joint Cloudera and Mistral solutions will be available through Cloudera’s enterprise sales team and partner ecosystem, with additional integrations and capabilities rolling out over time.
Spotlight
New Cequence & EMA Research: 94% of Enterprises Trust Their AI Agents Aren’t Over-Provisioned. Only 33% Actually Enforce It.
Nearly every enterprise believes its AI agents are properly scoped. Only a third have actually made sure of it.
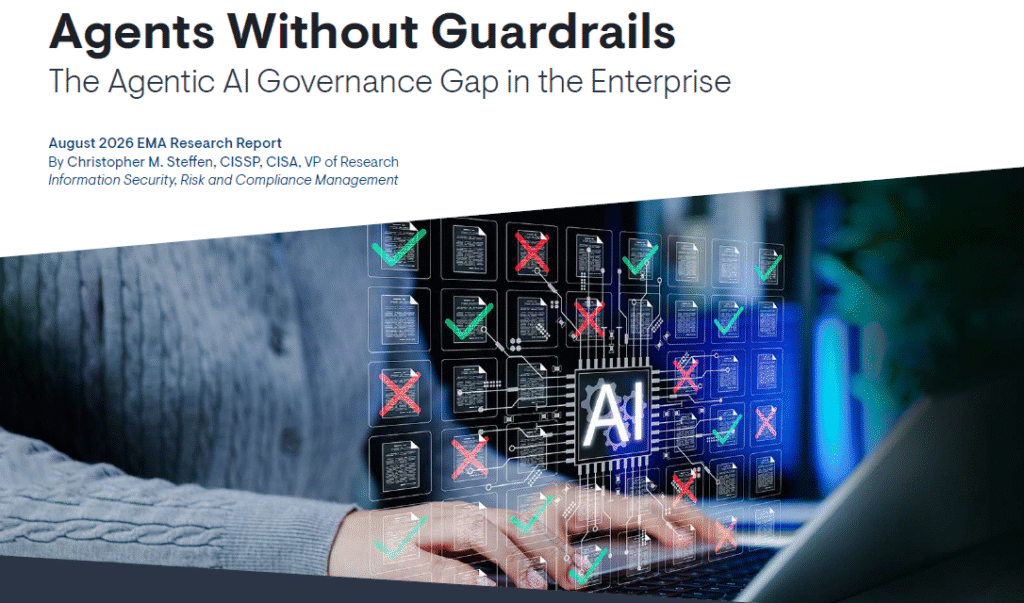
Today, new research from Cequence Security, the leader in application, API, and agentic AI protection, and Enterprise Management Associates (EMA) found that 94% of enterprise IT and security leaders are confident their AI agents do not have more access than they need, yet only 33% actually provision agents with least-privilege access. The remaining two-thirds run on broad standing permissions that are reviewed periodically, rarely reviewed, or never reviewed at all.
That gap between confidence and practice is already showing up in production, not a theoretical risk, but as incidents enterprises are living with right now. Among the organizations surveyed:
- 65% have experienced an AI agent take an action outside its intended scope, including 29% with measurable business impact, including data exposure, financial loss, operational disruption, or reputational damage. Another 36% caught a near-miss before it caused damage.
- Only 32% can detect and contain an out-of-scope agent action within minutes through automated means; 55% need hours and manual steps to respond.
- In approximately 4% of organizations surveyed, the first sign of trouble came from a customer or outside partner, not an internal system.
The findings point to one clear story. Governance has not kept pace with the speed of agentic AI deployment, and that gap is showing up at every stage of the agent lifecycle, from how agents are provisioned, to how their actions are authorized, to how they are decommissioned once a pilot ends. Other key findings from the report include:
Enterprises Have Moved Past the Pilot Stage
The scale of deployment makes the gap more urgent. 46% of organizations report they are already scaling agentic AI across multiple departments and production workflows, and 79% are running generative and agentic AI simultaneously. Further, more than 92% report an increase in AI and bot-driven traffic targeting customer-facing applications and APIs.
Authorization is Checked at the Wrong Time, Or Not At All
That governance gap extends to how access is enforced in the moment an agent acts. Only 34% of organizations evaluate an AI agent’s authorization at the moment it attempts a specific action. The majority rely on periodic policy reviews or standing permissions set once at provisioning and never revisited, meaning an agent’s access can quietly outlive the task it was originally granted for, and keep working long after anyone signed off on it.
Abandoned Pilots Are Leaving Live Credentials Behind
Additionally, there’s an increasing risk in how enterprises manage agents that don’t make it to production. 31% of agentic AI pilots have been paused indefinitely, discontinued, or abandoned. Many were real deployments with real system access and credentials that were never cleaned up. Every abandoned pilot with live credentials is exposure nobody is actively watching.
External Connectivity Carries the Same Risk
14% of organizations allow AI agents to connect to outside tools and data sources via the Model Context Protocol (MCP) without restriction. Among the majority who do limit those connections to an approved list, fewer than half, just 49%, have a dedicated team actively maintaining and auditing that list on a regular basis.
Christopher M. Steffen, CISSP, CISA, VP of Research at EMA, said: “This research shows enterprises have moved well past experimentation with agentic AI right into production, and governance has not kept pace with that shift. The gap isn’t a lack of awareness; most organizations have policies in place and express real confidence in them. The gap is between what’s written down and what’s enforced when an agent takes an action nobody approved. That disconnect shows up most clearly in how organizations authorize agent actions and monitor them once they’re live, and it’s the reason incidents are happening at a rate the industry hasn’t fully reckoned with.”
Shreyans Mehta, Co-founder and CTO at Cequence, said: “The number that jumped out to me is the 92% being confident in their governance frameworks. Confidence like that is a trap; it’s exactly why organizations stop looking for problems, stop investing in monitoring, and let authorization checks lapse until an incident forces the conversation. This is the exact blind spot Cequence is built to close, giving security teams real-time visibility into what AI agents are actually doing and enforcing authorization at the moment an agent acts, not after the fact.”
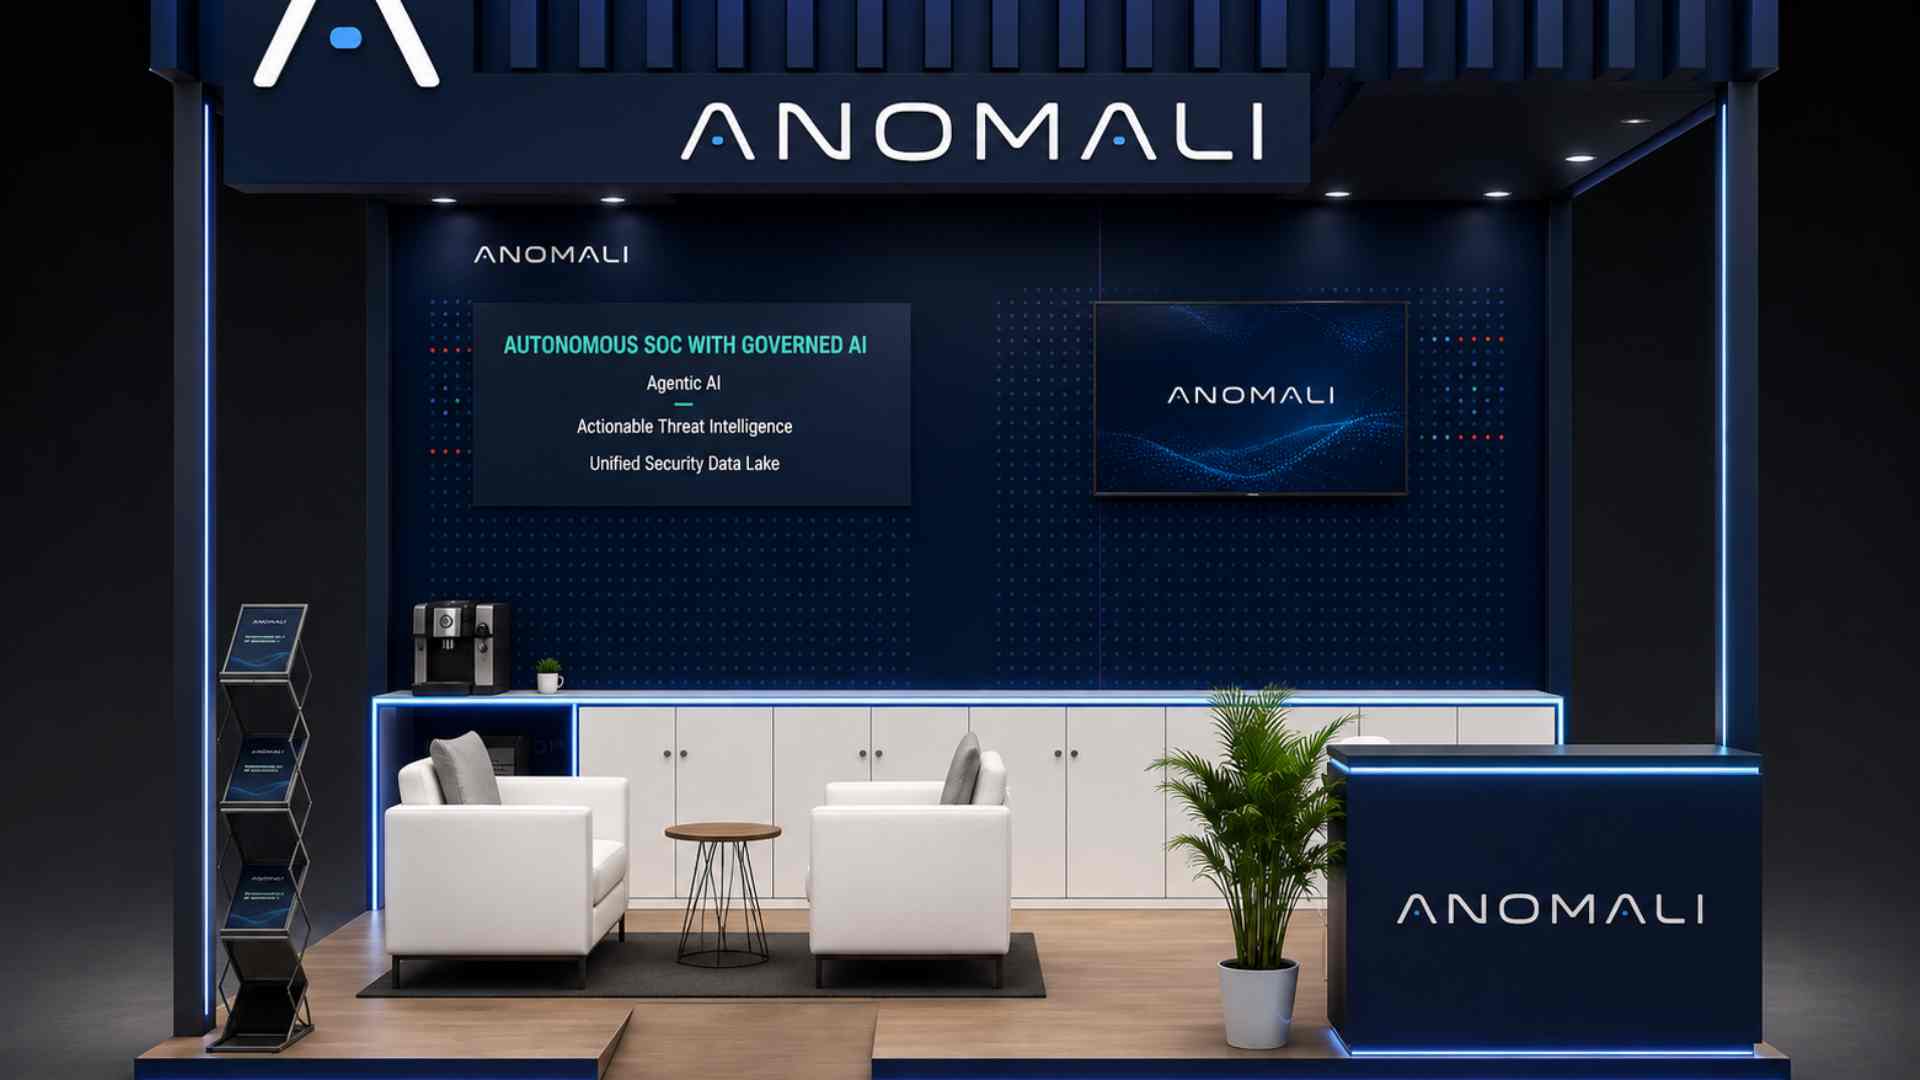
Anomali, the leading global Managed Intelligence and Agentic SOC platform, announced its participation at GISEC Global 2026, taking place through 16-18 September at Dubai Exhibition Centre (DEC), Expo City.
The company’s discussions at GISEC will center on Autonomous SOC with Governed AI, Agentic AI, Actionable Threat Intelligence and Unified Security Data Lake capabilities that are changing the manner in which security teams investigate threats, manage workflows and make decisions.
Samer Jadallah, Vice President, Middle East & Africa at Anomali, will represent the company at GISEC and will focus on the growing impact of AI on both attackers and defenders, emerging shifts in the threat landscape, including the need to counter CEO impersonation attacks as well as key challenges facing modern security teams. He will also highlight AI’s role is helping organizations respond more effectively to evolving threats, Anomali’s commitment to the region and ongoing product innovation and plans to expand adoption of the Anomali platform across global enterprises and government organizations.
A key focus at this year’s event will be the changing nature of cyberattacks. As threat actors promptly adopt AI to scale campaigns and further accelerate attacks, security operations centers (SOC) are under growing pressure to process rising volumes of alerts with limited resources. To help with this, Anomali will demonstrate how AI can support analysts in multiple ways like surfacing higher- value insights, reducing manual effort and enabling quicker, informed responses.
Visitors can find Anomali at Booth E156 and Booth A80.
- Event: GISEC Global 2026
- Booths: E156 and A80
- Location: Dubai Exhibition Centre (DEC), Expo City
- Dates: 16 th to 18 September 2026
- Time: 9:00 am to 5:00 pm GST

VELAA PRIVATE ISLAND ANNOUNCES THE VELAA VAMPIRE CHRONICLES FOR HALLOWEEN 2026

Accor Loyalty Pays Off: Members Spend 2.6x More, Driving Growth at Mövenpick Hotel Apartments Downtown Dubai

Majestic Hotels Celebrates World Tourism Day with Two Decades of Dubai Hospitality and a Growing Homegrown Legacy


-
News11 years ago
SENDQUICK (TALARIAX) INTRODUCES SQOOPE – THE BREAKTHROUGH IN MOBILE MESSAGING
-
 Trending11 months ago
OPPO A6 Pro 5G Review: Reliable Daily Driver
-

 Tech News2 years ago
Denodo Bolsters Executive Team by Hiring Christophe Culine as its Chief Revenue Officer
-
 VAR1 year ago
Microsoft Launches New Surface Copilot+ PCs for Business
-
 Automotive2 years ago
AGMC Launches the RIDDARA RD6 High Performance Fully Electric 4×4 Pickup
-
Tech Interviews2 years ago
Navigating the Cybersecurity Landscape in Hybrid Work Environments
-

 Tech News1 year ago
Nothing Launches flagship Nothing Phone (3) and Headphone (1) in theme with the Iconic Museum of the Future in Dubai
-
 VAR2 years ago
Samsung Galaxy Z Fold6 vs Google Pixel 9 Pro Fold: Clash Of The Folding Phenoms